Identity and Access
Best Secrets Management Tools in 2026: Vault, OpenBao, and SOPS
Pick one runtime store the app fetches, or the encrypted file you can review in git. Another leak scanner will not tell you which process still holds the live value.
Expertise: Identity and Access · Level: Intermediate · 6 min read
Pick 1 store the app fetches at runtime, or the encrypted file you can review in git. The scanner the team already runs finds a string in a gist. It does not say which process still holds the live value.
A lease you operate, config in git, and a hosted store developers will actually use are different retrievals. Another dashboard of last week’s leaks is not a store.
In production the miss is a CI variable that was rotated in the vault UI and still hardcoded in the worker that started on Monday. The leak scan is how you found the old copy. Secrets management is how the new copy is fetched.
Vault-shaped leases, SOPS-style files, and cloud secret stores split that fetch. Choose the retrieval developers will call on the hot path.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether you fetch at runtime or decrypt a file, whether you operate the box, the license, and whether the docs name a lease or decrypt you can run on a secret you own. Azure Key Vault missed because AWS already covers that cloud-button job family.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| HashiCorp Vault | Known open-core secret store | Dynamic leases · BSL / commercial · you host or HCP |
| OpenBao | Open Vault-shaped API you can still fork | Vault-shaped API · MPL-2.0 · you operate it |
| SOPS | Encrypt the file you already commit | In-place encrypt · MPL-2.0 · file stays in git |
| Infisical | Developer-shaped secret SaaS you can also host | Projects and folders · MIT core / commercial · self-host or cloud |
| AWS Secrets Manager | The button if the app already runs on AWS | IAM lock · AWS terms · same account as the app |
| Doppler | Developer SaaS for env sync | Env sync · commercial · CLI they ship |

HashiCorp Vault
Best for known open-core secret store
Vault is the name people already wrote down. Dynamic secrets, leases, many auth methods. The license is BSL, not Apache.
When the question is a lease, not a dotenv, this is the commercial vault most teams already staff. You staff it or you buy HCP.
Key features
- Dynamic secrets on the public docs
- Many auth methods
- You can host it
- HCP if you will not
Why we like it
A lease you can revoke beats a long-lived key that is still in git.
Limits
BSL. You staff it or you buy HCP.
OpenBao
Best for open Vault-shaped API you can still fork
OpenBao is the Linux Foundation fork of Vault. Same shape of API. MPL-2.0. Younger operator memory than Vault.
If the hole is the license, not the API, this is the open fork. You still staff the box. It is not a dotenv SaaS.
Key features
- Vault-shaped API
- MPL-2.0
- You operate it
- LF stewardship
Why we like it
When license talk is the blocker, an MPL fork of the API you already know is the clear buy.
Limits
Younger ecosystem. You still staff the box. Not a dotenv SaaS.
SOPS
Best for encrypt the file you already commit
SOPS encrypts YAML, JSON, and dotenv in place. KMS, age, or PGP unlocks it. The file stays in git.
When the secret is a file the chart already mounts, an envelope is the control that matches how you actually work, because you are not pretending you need a lease. A decrypted leftover is still a leak.
Key features
- In-place encrypt
- age, KMS, PGP
- CI decrypt
- You keep the files
Why we like it
An envelope around a file you already commit beats a second vault nobody fetches.
Limits
Not a dynamic lease. Key ceremony is yours. A decrypted leftover is still a leak.
Infisical
Best for developer-shaped secret SaaS you can also host
Infisical sells folders of secrets for apps and humans. Open core you can host. Cloud if you will not.
Teams that hated Vault ceremony land here, so treat it as a store, not as scanning. You still rotate.
Key features
- Projects and folders
- Self-host or cloud
- CLI and SDKs
- Open core
Why we like it
A developer-shaped store you can also host is useful when ceremony was the reason people stayed on dotenv.
Limits
You still rotate. Cloud is a vendor.
AWS Secrets Manager
Best for the button if the app already runs on AWS
Managed secrets with rotation hooks on the public docs. IAM is the lock. Price is per secret per month on the AWS page.
If the compute is already AWS, a second vault is often vanity, because the app already has a way to call the account. Parameter Store is the cheaper sibling you should name out loud.
Key features
- IAM lock
- Rotation on the public docs
- Same account as the app
- AWS APIs
Why we like it
Honesty. The button in the account you already run beats a second ceremony.
Limits
AWS-only. Cost at scale. Parameter Store is the cheaper sibling you should name.
Doppler
Best for developer SaaS for env sync
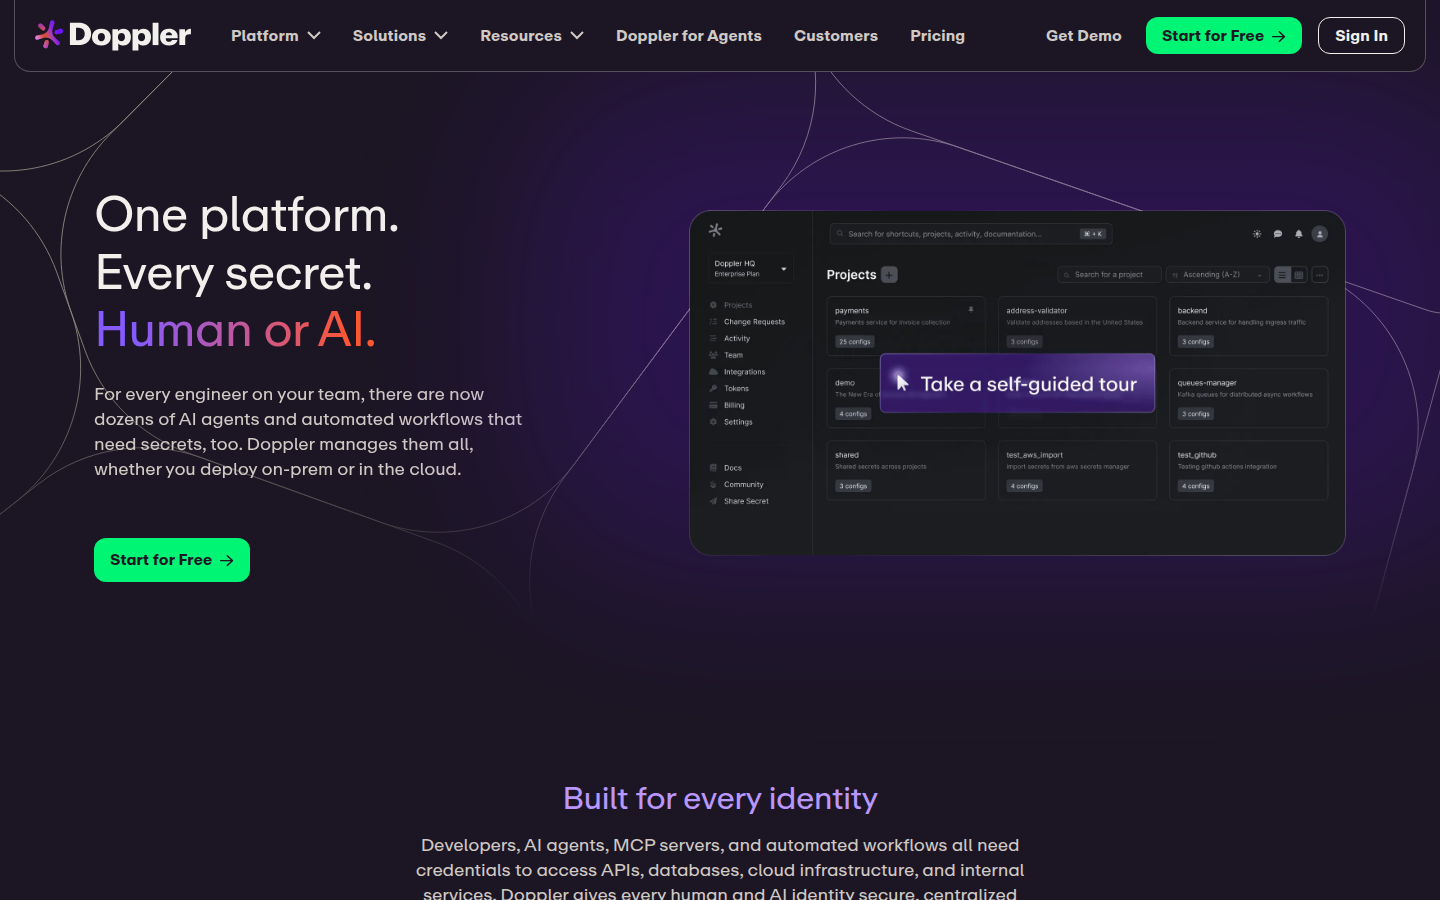
Doppler syncs secrets into the places developers already run. The pitch is fewer dotenv files in chat.
When the hole is a Slack paste, a sync tool is the job. You still need a source of truth. History leaks are on secret scanning.
Key features
- Project configs
- Sync to clouds they list
- CLI
- Commercial
Why we like it
If people are still pasting .env files, sync is the product, not another vault ceremony.
Limits
Commercial. You still need a source of truth.
What we left out
- Azure Key Vault. Teams already running on Azure want the native button. AWS Secrets Manager already covers that cloud-button job family, and one native cloud option is enough on a six-tool page.
- 1Password. People want the vault humans already open. It failed the runtime-fetch-for-apps check. It is a human vault, not an application store.
Vault threads treat ceremony as the tax. SOPS threads treat the file as enough. Name which hole you actually have.
Questions before you buy
A quote that cannot answer these is selling a different product.
- Can a new laptop fetch this secret without copying a .env from Slack?
- Are we buying a lease, a file envelope, or a developer sync tool?
- Do we operate the box, or are we buying a hosted product we cannot export?
Stop copying .env files. Fetch at runtime or decrypt a file you can review.
FAQs
Does a store replace secret scanning?
No. The store holds the next key. Scanning finds the last one. Those are different jobs. Open the matching list for the other one.
Is SOPS a vault?
No. It is an envelope around a file you already commit.
Vault or OpenBao?
Same shape of API. The license and the operator memory differ. Read both pages.
Is this a scored bake-off?
No. Order is editorial.

