Application Security
Best DAST Tools for Web Apps and APIs in 2026
Send a request against the host you operate, including the gateway rewrite SAST never compiled. This is not a license to scan a CIDR you have never opened.
Expertise: Application Security · Level: Intermediate · 6 min read
The OWASP Web Security Testing Guide, section 4.0, defines a web application security test as an active analysis of the application for weaknesses, technical flaws, or vulnerabilities. The methodology is black box: the tester has little to no information about the application under test.
Start with a decision: is this a host you operate, or a stop? A running app includes gateway rewrites the compiler never saw. A neighbor’s CIDR is not your test surface.
A proxy you drive, a known-check runner, and CI against an OpenAPI you own are different ways to send that request. The sink in source stays a finding on SAST tools. Run the check you can name on the app you actually ship.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether it crawls or only asserts known checks, whether you operate it, whether the docs name a host you own, and whether CI is a first-class path. Acunetix missed because Invicti already covers that commercial scanner.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| OWASP ZAP | Open DAST you can script | Open DAST · Apache-2.0 · you script the daemon |
| Nuclei | Known checks on URLs you already have | YAML templates · MIT · URL list you already have |
| Burp Suite | Human proxy on a flow you walk | Human proxy · community / Pro · you walk the flow |
| Caido | Newer proxy desk with a calmer UI | Newer proxy desk · community / paid · web UI |
| Nikto | One dusty pass on a vhost you just stood up | CGI and headers · GPL-2.0 · one pass per vhost |
| Invicti | Paid proof when legal wants a vendor | Proof-based findings · commercial · vendor on the call |
OWASP ZAP
Best for open DAST you can script
ZAP is desktop and daemon. Spider, AJAX spider, OpenAPI import, and an Automation Framework you write in YAML. The HTML report is ugly and honest.
You operate it and you can check the plan into git, so staging you own becomes a repeatable run. It is complementary to SAST. It is not a hunting license.
Key features
- Daemon and CI baseline
- OpenAPI import
- Automation Framework YAML
- Huge add-on market
Why we like it
A plan you can review in git is a crawl plan you can review in git. You stay on hosts you operate.
Limits
SPA crawls still lie. Java heap on large sites. Stay on hosts you operate.
Nuclei
Best for known checks on URLs you already have
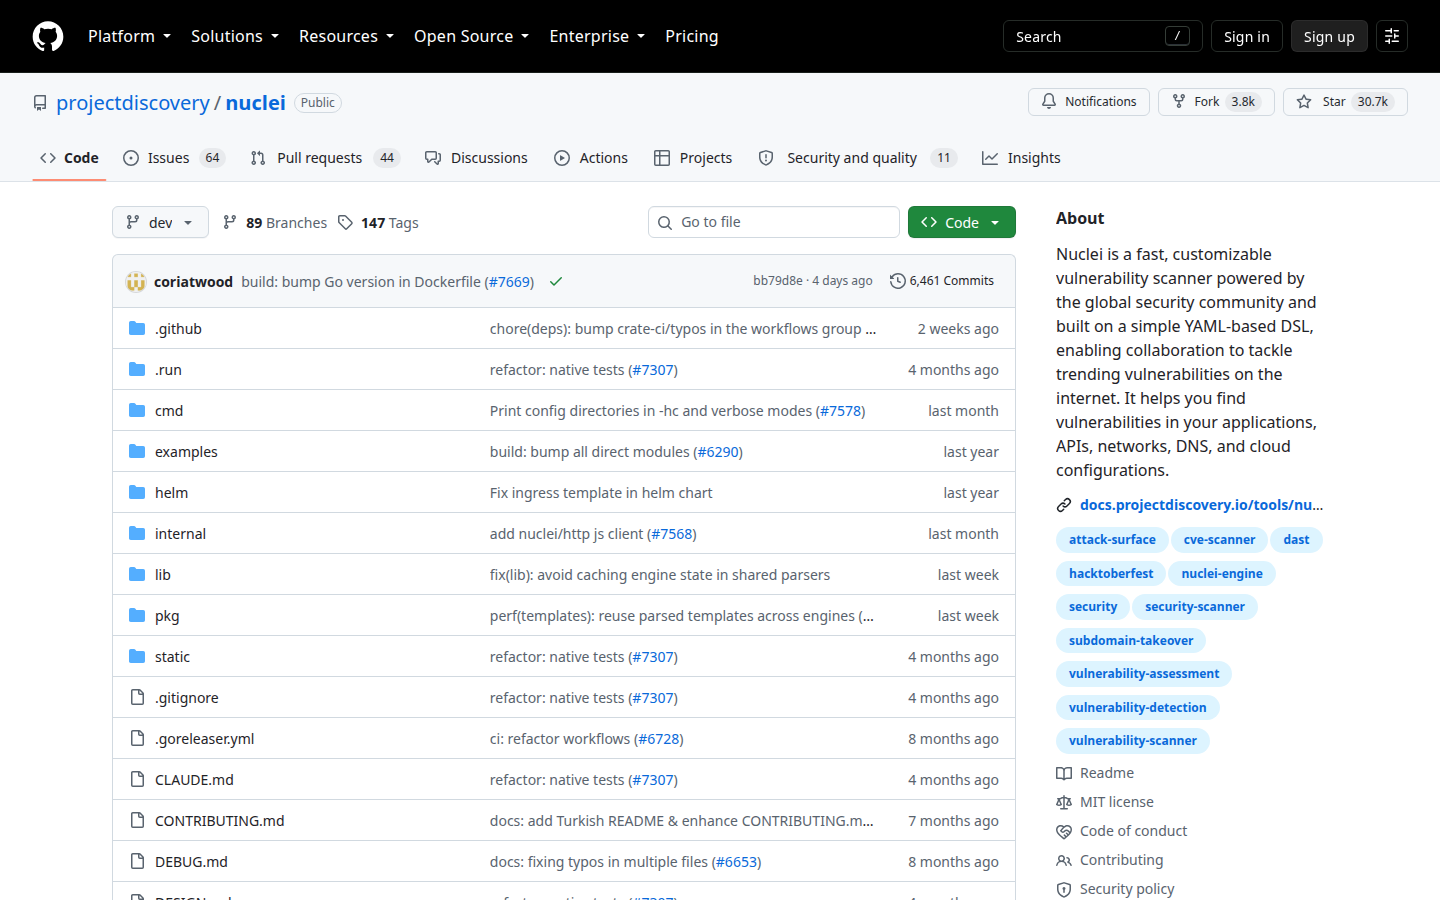
Nuclei is a template engine. It is not a crawler. You pin template versions and point it at an allowlisted URL list you already own.
When inventory already named the host, a known-check runner is the next step, because a spider would only rediscover URLs you have. The catch is it is easy to point at the wrong CIDR.
Key features
- YAML templates
- Fast on a URL list
- SARIF and JSON
- You pin the pack
Why we like it
Known checks on a list you own are faster than pretending a crawler found the route.
Limits
Not a full authenticated crawl. Easy to point at the wrong CIDR. Do not.
Burp Suite
Best for human proxy on a flow you walk
Community is the intercepting proxy. Professional adds the crawler and scanner. When a login has three redirects, a human still opens Burp.
A daemon cannot feel a broken wizard, so the pair of hands is the product. Scope is a written list, not a feeling, because that is how you stay on an app you operate.
Key features
- Intercepting proxy
- Extensions
- Pro scanner
- Enterprise for CI
Why we like it
Authenticated flows with redirects still need a person. That is the proxy a person still has to drive.
Limits
Pro is commercial. Java desktop. Scope is a written list, not a feeling.
Caido
Best for newer proxy desk with a calmer UI
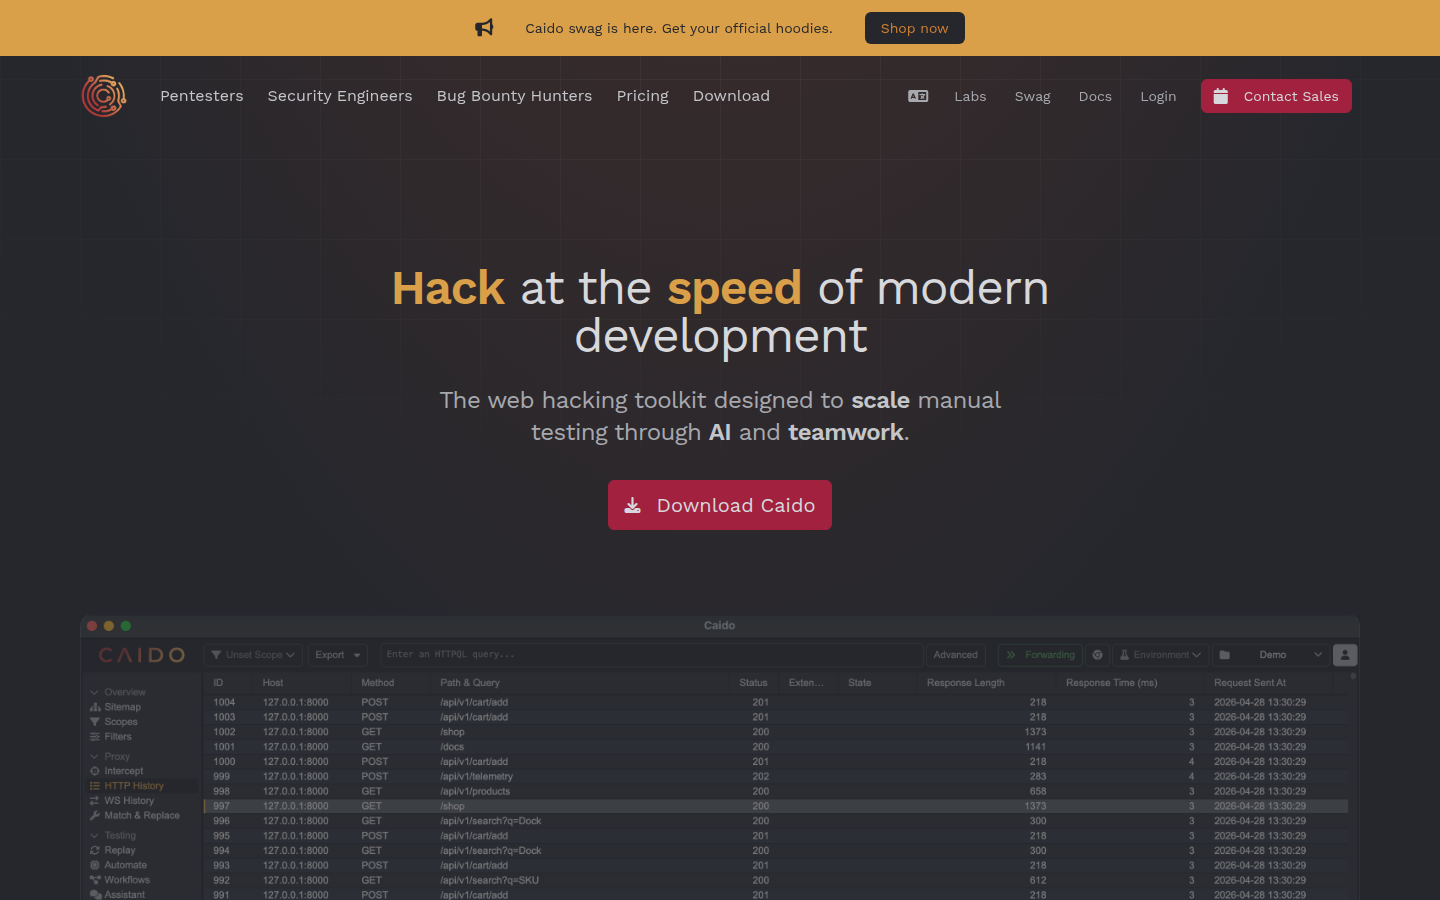
Caido is a newer intercepting proxy with a web UI and workflows on the public docs. It is not a full DAST suite yet.
People move here because Burp felt heavy on a Thursday, so we keep both names. The catch is the scanner and the extension set are younger.
Key features
- Web UI proxy
- Workflows on the public docs
- Growing plugins
- Community tier
Why we like it
A calmer desk is useful when the job is still a human walking a flow you own.
Limits
Younger scanner. Smaller extension set. Own hosts only.
Nikto
Best for one dusty pass on a vhost you just stood up
Nikto is a classic web server scanner. CGI and header checks. Loud. Useful once per host you own.
A new staging vhost still hides a phpinfo, so you run it once, file the real tickets, and move on. It is not a modern authenticated program.
Key features
- Forgotten-file checks
- Perl CLI
- Tuning flags
- Text and HTML out
Why we like it
One dusty pass on a host you just stood up still finds forgotten files. Then you stop.
Limits
Dated signatures. Noise. Not a modern authenticated program.
Invicti
Best for paid proof when legal wants a vendor
Invicti, formerly Netsparker, sells proof-based scanning. The finding tries to demonstrate itself. Tickets come with the license.
A CISO sometimes needs a vendor on the call, so this is the paid proof row. Keep an open daemon in CI because licenses expire and YAML does not.
Key features
- Proof-based findings
- Tickets and roles
- SaaS or engine
- Vendor on the call
Why we like it
When legal wants a logo, a commercial scanner is the practical purchase. It does not retire the open plan.
Limits
Commercial. Crawl tuning.
What we left out
- Acunetix. People want the Netsparker-era commercial scanner they already named in an RFP. Invicti already covers that commercial scanner here.
- StackHawk. Teams want CI DAST next to an OpenAPI they already commit. It is a commercial CI desk, and ZAP Automation Framework already covers scripted DAST you can check into git.
DAST threads treat scope as the first control. A scanner is not a hunting license, and it is not a human.
Questions before you buy
If a first-party page cannot answer these, keep shopping.
- Can I import my own OpenAPI and stay inside a written scope?
- Is this a crawl, a known-check runner, or a human proxy?
- If the URL is not ours, do we close the tab?
Point it at an app you operate. Nuclei is not a crawler. A happy-path collection is not this page.
FAQs
Is scanning other people’s sites legal?
Not without written permission. These tools belong on staging, labs, and production you operate.
Does DAST replace SAST?
No. SAST names the sink in the PR. DAST hits the running app. Those are different jobs. Open the matching list for the other one.
Can Nuclei replace a crawler?
No. Nuclei asserts known checks on URLs you already have.
Is this a scored bake-off?
No. Order is editorial.

