Identity and Access
Best Identity Protection Tools in 2026: Workforce IAM and PAM
Treat a stolen session cookie as a live login. MFA at the prompt does not kill a cookie that already exists.
The login prompt asked for MFA, so the team treated the session as dead. The stolen cookie still worked. 1 stolen session is a live login.
The IdP the team already runs is green on enrollment percentages. Enrollment does not revoke a cookie minted last week. Standing admin is still there after the contractor leaves. Those are two holes.
Workforce identity platforms and privileged access products solve different ones. Customer login is not on this shortlist. The work here is workforce session, MFA, and whether a stolen cookie still opens the app.
Cloud IdPs, a hostable identity stack, and session controls that can step-up or kill a cookie split that hole. Pick the control that can invalidate the session, not only challenge the next password.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof two products do the same work. We cared about whether SCIM is documented, whether session risk or logout exists, whether you operate it, and whether privileged access is the product or an add-on.
| Tool | Best for | What to check |
|---|---|---|
| Okta | Independent cloud IdP with SCIM and session risk | Commercial · cloud workforce · SCIM + session risk |
| Microsoft Entra ID | The cloud directory most Microsoft 365 tenants already have | Commercial · cloud workforce · PIM on P2 |
| Keycloak | Open-source IdP you operate | Apache-2.0 · you operate it · standards IdP |
| authentik | Self-hosted IdP with SCIM in both directions | MIT core · you operate it · SCIM both ways |
| Zitadel | Hosted or self-hosted IdP with B2B orgs | AGPL-3.0 · cloud or you host · B2B orgs |
| CyberArk | Privileged access for the standing admin | Commercial · privileged access · known vault |
Okta
Best for independent cloud IdP with SCIM and session risk
Okta is the independent cloud IdP. Lifecycle Management documents SCIM. Identity Threat Protection documents continuous session risk and Universal Logout.
Use it when the directory cannot be Microsoft-only, and when the app catalog plus SCIM is the actual job.
Key features:
- Workforce SSO, MFA, and Universal Directory
- SCIM 2.0 and 1.1 provisioning in the docs
- Identity Threat Protection: session risk, Universal Logout, Shared Signals
- Lifecycle Management for joiner, mover, and leaver
Why we like it:
An IdP that can deprovision and kill a session is the session-kill path after token theft. Their own pages name those two jobs.
Limits:
Threat protection and privileged access sit on higher suites or as add-ons.
License or pricing: Commercial SaaS.
Microsoft Entra ID
Best for the cloud directory most Microsoft 365 tenants already have
Entra ID is the cloud directory most Microsoft 365 tenants already have. Conditional Access, ID Protection, PIM, and SCIM are the controls that close this list’s holes.
If the estate is already Microsoft, starting a second workforce IdP is usually politics.
Key features:
- SSO, passwordless, and Conditional Access on P1
- ID Protection and risk-based Conditional Access on P2
- Privileged Identity Management: eligible roles, approval, time-bound access
- SCIM 2.0 as a client to SaaS apps and as a service-provider API
Why we like it:
PIM is the first-party answer to standing Global Admin inside Entra and Azure. ID Protection is the first-party session-risk row.
Limits:
PIM and full ID Protection are not the free edition. SCIM deprovisioning follows the soft-delete window on the public docs.
License or pricing: Commercial. Microsoft Entra ID P1 and P2 are add-ons.
Keycloak
Best for open-source IdP you operate
Keycloak is the open-source IdP a lot of shops already run in a container. SSO, brokering, LDAP federation. You operate the server.
There is no per-user card. SCIM is a preview flag in the 26.7 docs, off by default.
Key features:
- OpenID Connect, OAuth 2.0, and SAML 2.0
- Identity brokering and social login
- User federation to LDAP and Active Directory
- SCIM Realm API preview in the 26.7 docs, disabled by default
Why we like it:
When the requirement is a standards IdP on your own iron, and you can staff the upgrades, this is the open-source IdP you can actually host.
Limits:
You run Java, clustering, backups, and the upgrade train. Preview SCIM is not a finished catalog.
License or pricing: Apache-2.0.
authentik
Best for self-hosted IdP with SCIM in both directions
authentik is the self-hosted IdP that keeps the directory on your side of the wire. The vendor does not currently host it for you.
SCIM works in both directions in the docs we read. That is further along than a preview flag.
Key features:
- OIDC, SAML2, LDAP, RADIUS, and an application proxy
- SCIM 2.0 provider to push users and groups into apps
- SCIM source so Entra ID, Okta, or Google Workspace can provision in
- Policies, GeoIP, and OIDC back-channel logout on the public feature list
Why we like it:
If the job is we will run the IdP and SCIM has to push and pull, this is the self-hosted row that documents both.
Limits:
You own uptime. Privileged access and scheduled offboarding sit on Enterprise.
License or pricing: MIT (core).
Zitadel
Best for hosted or self-hosted IdP with B2B orgs
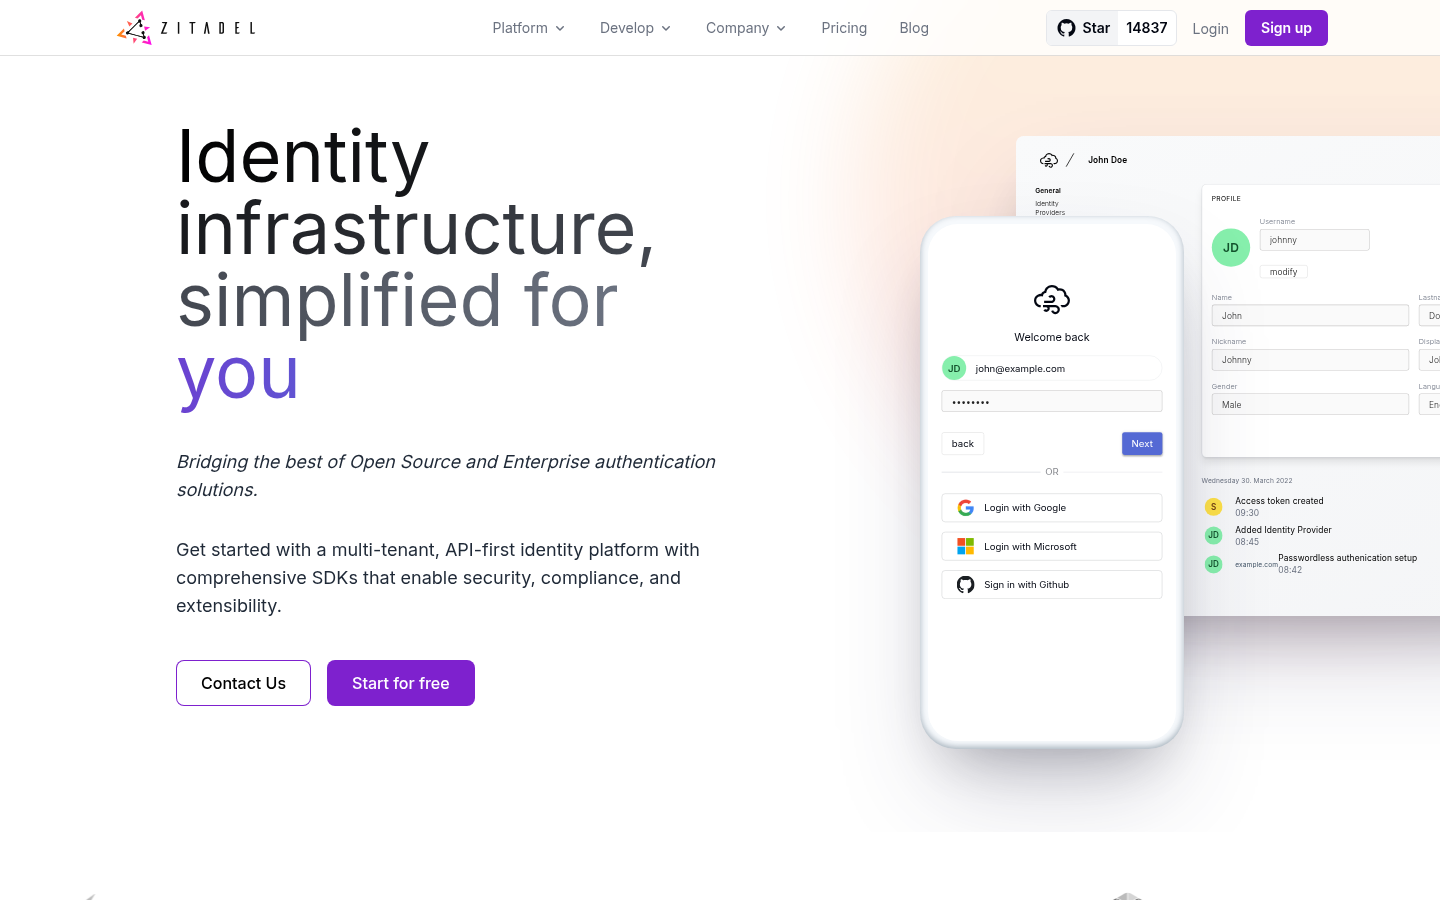
Zitadel sits between self-host and a paid cloud IdP. Hosted login, passkeys, B2B organizations, Actions, and APIs first. Cloud SKU or the same software. AGPL-3.0.
SCIM is a service provider for users. Group provisioning is not supported. Their docs say that out loud.
Key features:
- Hosted login, social IdP templates, MFA, and passkeys
- Organizations and project grants for multi-tenant B2B
- Actions: custom workflow after events
- SCIM v2.0 service provider for user create, update, deactivate, and delete
Why we like it:
When you need tenant isolation that is not another realm and a prayer, or when you want someone else to run the control plane, this is the middle row.
Limits:
SCIM is users only. Required name and email fields are strict.
License or pricing: AGPL-3.0.
CyberArk
Best for privileged access for the standing admin
CyberArk is the privileged-access product on this list. Palo Alto closed the acquisition in 2026 and launched Idira. The same URL now serves that platform.
An IdP can refuse SSO to a host. It cannot rotate the password that is still on that host.
Key features:
- Privileged access management for human admins, with session isolation and vaulting
- Machine and secrets controls on the Idira platform pages
- Zero standing privilege and just-in-time access in current messaging
- Agentic / AI-agent identity as a new platform pillar
Why we like it:
Put it here for the account that is always on and always too powerful. Auditors still ask for PAM.
Limits:
Not a workforce IdP. The brand is in motion.
License or pricing: Commercial.
How to choose an identity protection tool
Four questions before the quote. Names below are tools, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Can we kill this session tomorrow without rotating every password by hand? | A stolen session is a live login. | Okta Universal Logout and session risk. Entra ID Protection and Conditional Access. | MFA at login as the only control. |
| Does SCIM deprovision the app, or only the IdP row? | A leftover app account is standing access. | Okta and Entra document SCIM. authentik documents both directions. Keycloak SCIM is preview. Zitadel is users, not groups. | A login box that cannot deprovision. |
| Is the standing admin an IdP role we can make eligible, or a host password that still needs a vault? | Workforce IdP and privileged access are different jobs. | Entra PIM for eligible roles. CyberArk for the always-on admin. | Calling a vault an IdP. |
| Do we operate the IdP? | Uptime is part of the license. | Okta and Entra are cloud. Keycloak, authentik, and Zitadel you can host. | A self-hosted IdP with no upgrade train. |
IdP threads treat SCIM as the product. A login box that cannot deprovision is a standing account.
Revoke the session, then expire standing admin. If those are two products, buy both on purpose. Do not call a vault an IdP.
FAQs
How do Okta and Entra differ from Keycloak, authentik, and Zitadel?
Okta and Entra ID are commercial cloud IdPs. You pay per user and they run the control plane. Keycloak, authentik, and Zitadel are software you can host (Zitadel also sells a cloud). The protocols overlap. The operations do not.
Which tools on this list document SCIM?
Okta documents SCIM 2.0 and 1.1. Entra ID documents SCIM 2.0 as a client and as a service-provider API. Keycloak documents a SCIM Realm API as a preview feature. authentik documents SCIM in both directions. Zitadel documents a SCIM v2.0 service provider for users, not groups.
Does a workforce IdP replace privileged access management?
No. An IdP authenticates people and, if you turn it on, provisions app accounts. Privileged access management vaults, isolates, and time-boxes the admin session. Entra PIM is just-in-time inside Entra. It is not a vault on the jump box. Open the privileged access list.
Is this a scored bake-off?
No. Order is editorial.

