Application Security
Best SAST Tools for CI in 2026
Point the finding at the call in the pull request. A SQL injection label across 40 files is not review time.
Expertise: Application Security · Level: Intermediate · 6 min read
A finding that says SQL injection is not useful in a pull request if the developer still has to search 40 files for the sink. We cared about review time: does the finding point at the call, can someone read the rule, and can CI fail without becoming noise.
Brochure language counts did not make the cut. Package CVEs are composition analysis. This matrix is the sink in your code.
The scanner the team already runs can be green on volume and still dump a class-level hit. The production miss is a sink that merged because nobody could find the line.
CI SAST you can fail, IDE findings that point at the call, and rules you can read split that review. Pick the tool that names the line, not the count.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether the finding names the file and the call, whether you can read or write the rule, whether CI can fail the PR, and whether the docs show a language you actually ship. A PDF dump with no sink failed.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| Semgrep | Rules you can read in the PR | YAML that looks like the sink · LGPL-2.1 CLI · you run it or their cloud |
| CodeQL | Query language on a GitHub repo | QL queries · GitHub CodeQL license · GitHub-hosted path |
| Bearer | Data-flow SAST you can run locally | Data-flow traces · Elastic License 2.0 · CLI in CI |
| SonarQube | Quality gate that includes security rules | Quality gate plus security · LGPL-3.0 community / commercial · you host it or SonarCloud |
| Snyk Code | Commercial PR comments on the sink | Pull-request comments · commercial · same tenant as SCA |
| Bandit | Python AST checks you can run offline | Python AST · Apache-2.0 · you run it offline |
Semgrep
Best for rules you can read in the PR
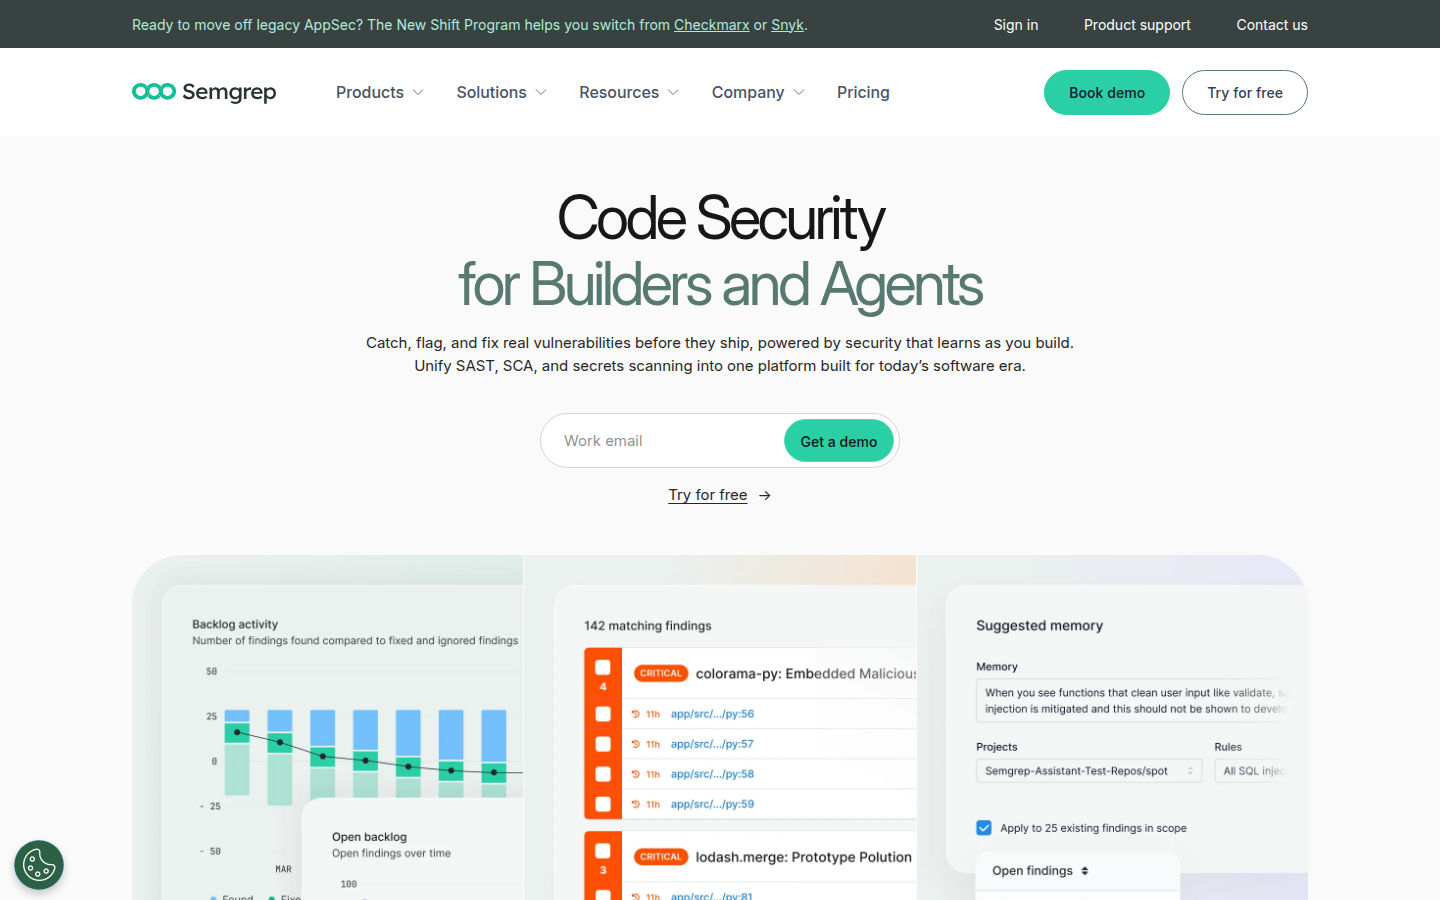
Semgrep matches code with a pattern that looks like the code. Rules are YAML. The CLI is open. Semgrep Cloud is paid.
A rule you can read is a rule you can fix. You still write rules for your frameworks. Cloud features sit behind a contract, so the CLI and the option are different buys.
Key features
- YAML rules that look like the sink
- OSS registry
- CI and PR comments
- You can write a rule in an hour
Why we like it
Patterns that look like the call are reviewable. You can keep the rule next to the repo.
Limits
You still write rules for your frameworks. Cloud features sit behind a contract. It is not a DAST.
CodeQL
Best for query language on a GitHub repo
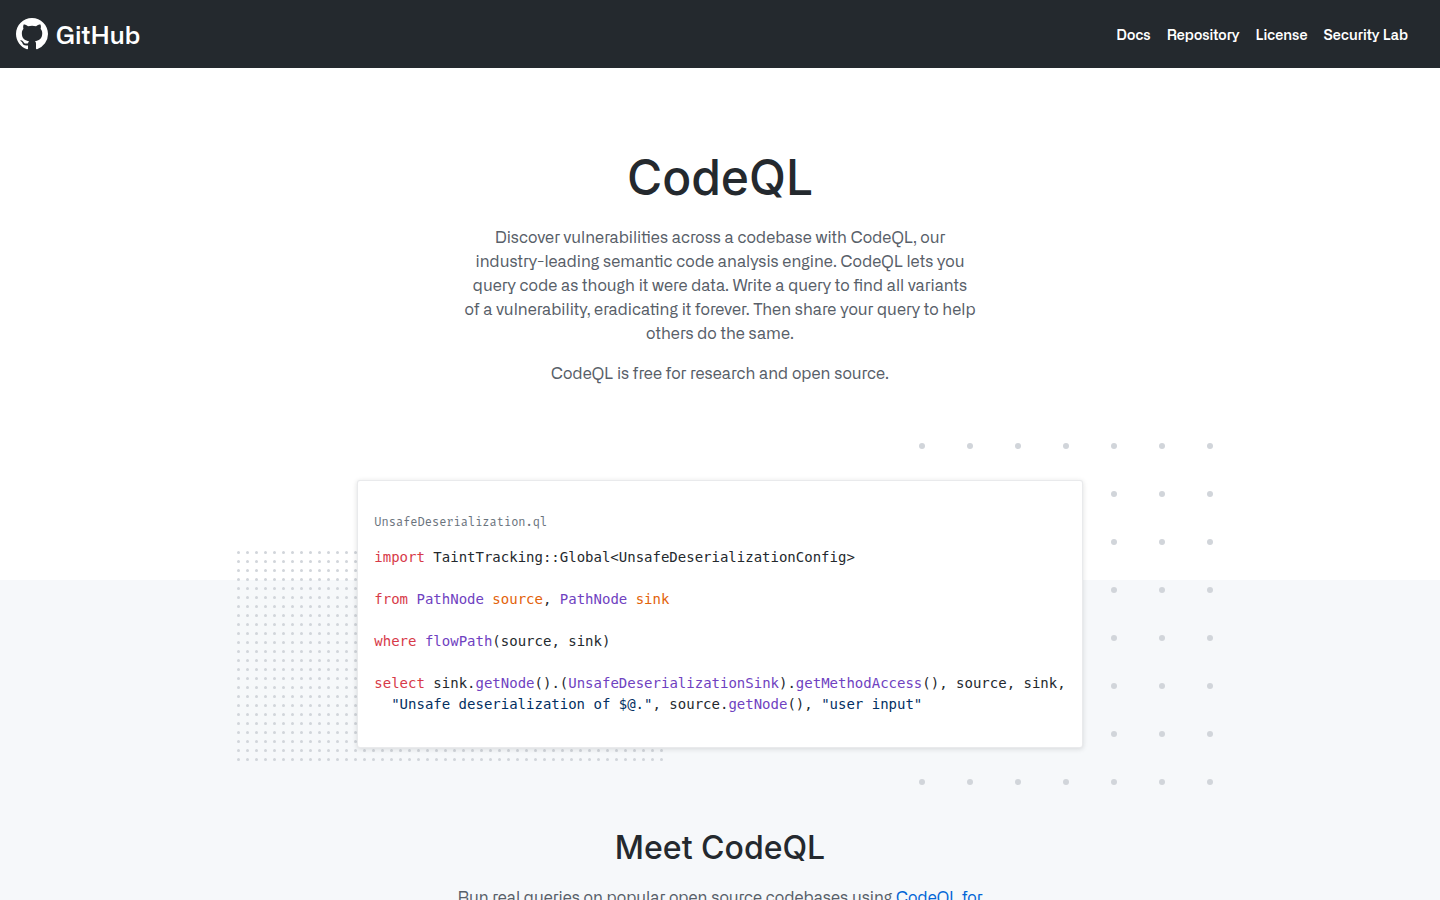
CodeQL treats the repo as a database. Queries are QL. GitHub Actions can run it on public repos under GitHub’s terms.
If the code is already on GitHub, this is the query option that can run without a second vendor. QL is a language your team must learn, and the license is not Apache.
Key features
- QL queries
- GitHub-hosted analysis
- Pack of security queries
- Results as SARIF
Why we like it
A query language on the repo you already host is the GitHub-native scanner.
Limits
The license is not Apache. Self-hosting has terms. QL is a language your team must own.
Bearer
Best for data-flow SAST you can run locally
Bearer traces data to a sink. The CLI is open under Elastic License 2.0. The product page still sells privacy and security findings.
When the bug is that an email reached the logger, a regex analyzer will miss it. This is the open data-flow option on this list. Language coverage is not every stack.
Key features
- Data-flow traces
- CLI you can run in CI
- Language support listed in the repo
- JSON and SARIF
Why we like it
A trace you can read beats a line match when the hole is where the data went.
Limits
ELv2 is not OSI Apache. Language coverage is not every stack. You still review the trace.
SonarQube
Best for quality gate that includes security rules
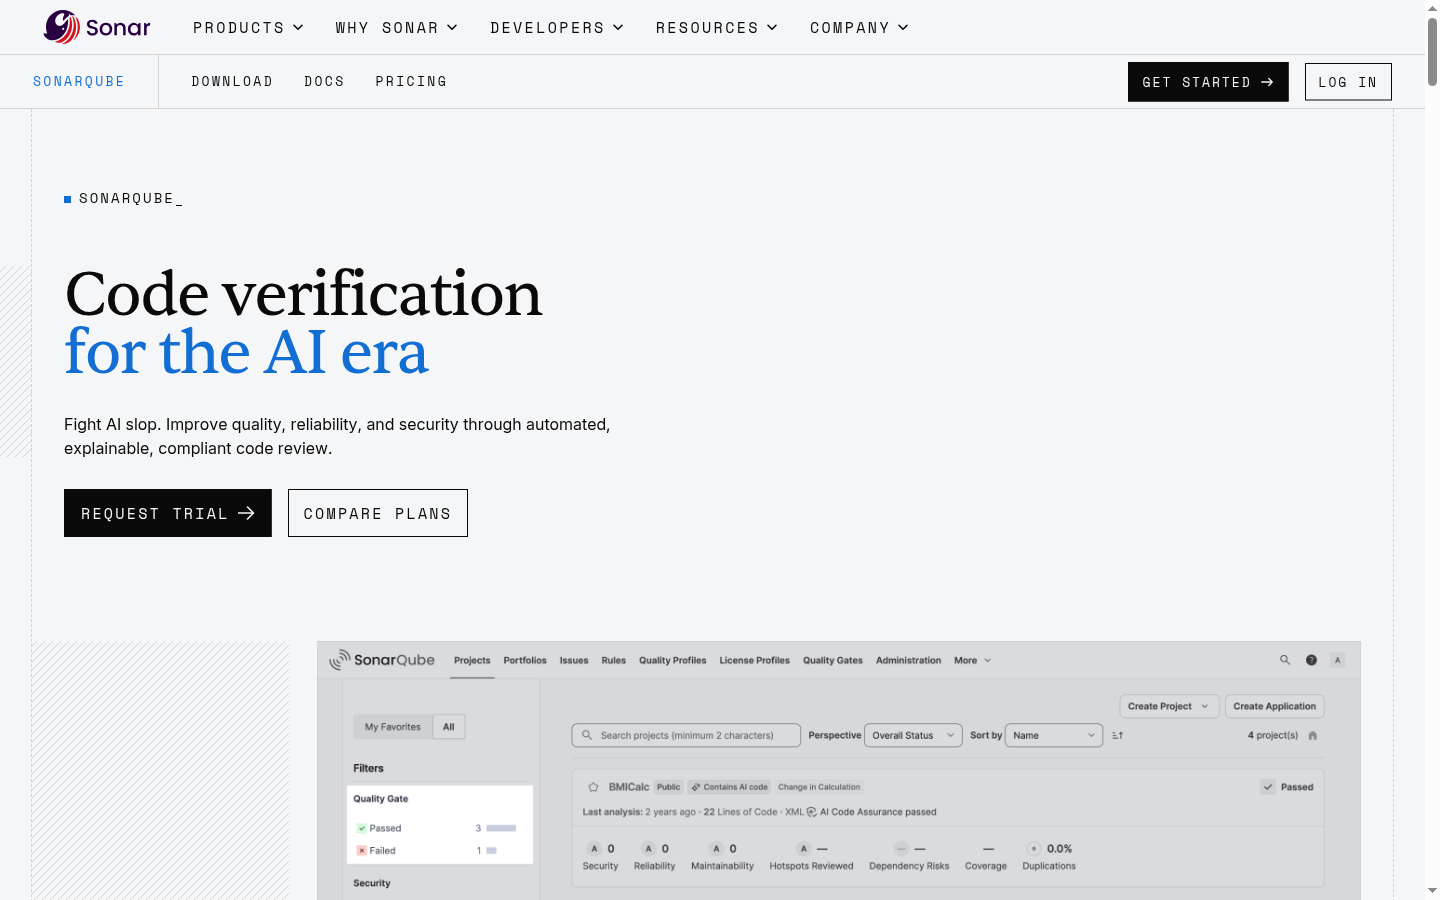
SonarQube is the known quality platform. Security rules ship in the same gate as bugs and smells. Community is LGPL. Enterprise is paid.
It is already in a lot of pipelines. A hotspot is not always a sink, so you still open the call. Edition splits hide rules.
Key features
- Quality gate in CI
- Security hotspot UI
- Many languages
- Self-host or SonarCloud
Why we like it
Using the gate you already staff beats a parallel SAST nobody opens.
Limits
A hotspot is not always a sink. Edition splits hide rules. This is not a pentest.
Snyk Code
Best for commercial PR comments on the sink
Snyk Code is the SAST product next to Snyk Open Source. Findings land in the pull request. The SCA job is a different list.
If the org already bought Snyk for the lockfile, this is the SAST they will enable. Rules are not a public YAML repo, so you still want a rule you can read somewhere.
Key features
- PR annotation
- IDE plugin
- Snyk rule engine
- Same tenant as SCA if you already pay
Why we like it
Enabling the analyzer on the tenant you already pay for is the practical commercial path.
Limits
Price is commercial. Rules are not a public YAML repo.
Bandit
Best for python AST checks you can run offline
Bandit walks a Python AST. Tests have ids like B201. It is the language specialist on this list.
A Python service that only needs these checks should not wait for a platform RFP. The ids are greppable. There is no data-flow across files the way Bearer claims.
Key features
- AST tests with stable ids
- Config as YAML
- CI friendly
- Apache-2.0
Why we like it
Stable ids you can grep are enough when the service is Python and the team is small.
Limits
Python only. No cross-file data-flow. Framework sinks still need a check you enable.
What we left out
- Checkmarx. Enterprise RFPs already print the name. Public pages are quote-led and Snyk Code already covers the commercial pull-request job.
- Veracode. Teams want a known hosted SAST with an auditor login. It is a sales-led platform this shortlist cannot price.
Semgrep threads on HN keep landing on what a match actually proves. We agree. A clean scan is not a sink you tested.
Questions before you buy
If a first-party page cannot answer these, keep shopping.
- Does the finding open the file and the call, or does it hand me a score?
- Can we write or fork a rule, or is the engine a black box?
- Are we buying SAST, SCA, or a quality gate, and which of those is already in CI?
If the finding cannot name the call, it will die in the backlog. Start with CodeQL when GitHub already runs it. Start with Semgrep when you need a rule you can grep.
FAQs
Is SAST the same as SCA?
No. SAST reads your code. SCA reads the lockfile. Supply chain owns the lockfile list.
Does a clean SAST mean the app is safe?
No. It means these rules did not fire. IDOR and authZ still need tests. Open authorization.
Should I run every tool?
No. Pick one rule engine you can write for, plus the platform you already pay for.
Is this a scored bake-off?
No. Order is editorial. We did not score true-positive rates in a lab.

