Identity and Access
Privileged Access Management Tools: A 2026 Guide
Time-box the path to a privileged target and expire it. A standing break-glass user is not PAM.
Expertise: Identity and Access · Level: Intermediate · 6 min read
The break-glass user has been standing for 90 days, since the last audit. The control the team already has is a named admin account and a password vault. Both can be green on the spreadsheet.
Green is not expiry. Privileged access management is the request, the approval, the open session, and the clock that kills that session. Skip expire and you bought another standing admin.
In production the failure is a contractor who left 90 days ago and can still open the jump box. Workforce login is a different hole. PAM is the time-boxed path to a privileged target, not the everyday IdP.
Vaulted sessions you operate, cloud PAM that wraps hyperscaler roles, and just-in-time elevation inside an identity platform you already run are different clocks. Choose the one that actually expires the path.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether the admin session expires, whether you operate the control plane, whether the product is a vaulted PAM desk or infra access, and whether the docs name a target you can point at a host you own.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| Teleport | SSH Kubernetes and app access with short certs | Short-lived certs · AGPL-3.0 / commercial · you host it or their cloud |
| Boundary | HashiCorp sessions to private endpoints | Just-in-time targets · BUSL · workers you deploy |
| CyberArk | Classic privileged vault and session | Password vault plus sessions · commercial |
| StrongDM | Commercial proxy to infra | Proxy to infra · commercial · identity from your IdP |
| Delinea | Secret Server and privilege on Windows estates | Secret Server plus privilege · commercial · Windows-heavy estates |
| Pomerium | Identity-aware proxy you can host | Policy on the URL · Apache-2.0 · you host the proxy |
Teleport
Best for SSH Kubernetes and app access with short certs
Teleport issues short-lived certificates for SSH, Kubernetes, and web apps. The core is open. Enterprise is paid.
The certificate expires. That is the job. You still connect it to an identity provider. The ZTNA list rows the same plane as a path. PAM is the privileged session.
Key features
- Short-lived certs
- Audit of sessions
- Kubernetes access
- Self-host or cloud
Why we like it
An access plane you can host, with a cert that ends, is the open answer to a standing key.
Limits
AGPL-3.0 on the core. Enterprise features are paid. You still connect it to an IdP.
Boundary
Best for HashiCorp sessions to private endpoints
Boundary brokers a session to a private IP without putting a standing key on the laptop. It sits next to Vault in the HashiCorp story.
If Vault already holds the secret, this is the session that does not copy it onto disk. BUSL is not Apache. You operate workers. It is not a password vault UI.
Key features
- Just-in-time targets
- Workers you deploy
- Vault integration
- Identity-aware
Why we like it
A broker that never drops the secret on the laptop is the pairing that avoids a second cloud lock when Vault is already the locker.
Limits
BUSL is not Apache. You operate workers. This is not a vault console.
CyberArk
Best for classic privileged vault and session
CyberArk is the known PAM option. Vaulting, session isolation, and privilege. The identity list already puts it on the matrix as the privileged specialist.
Procurement already wrote this name. We keep it so the open planes have a neighbor. This page does not reprint the identity six.
Key features
- Password vault
- Session recording
- Privilege on the endpoint
- Enterprise connectors
Why we like it
Naming the vault those estates already bought keeps the open planes from pretending the RFP is empty.
Limits
Sales-led. A vault that still issues standing passwords is the wrong use.
StrongDM
Best for commercial proxy to infra
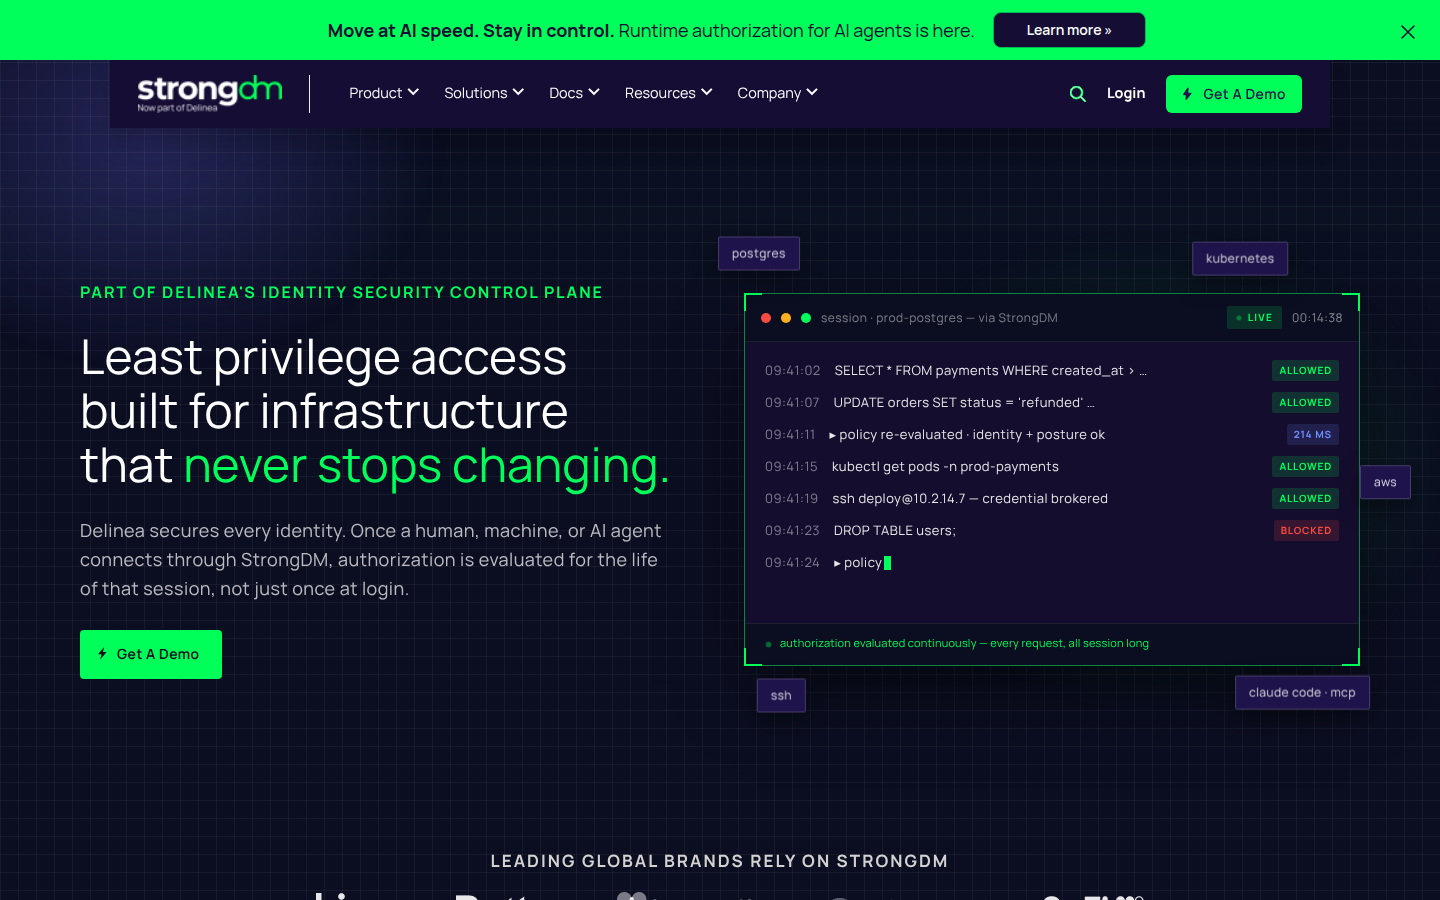
StrongDM is a commercial access proxy. People, roles, and audit sit on the path to the database and the cluster.
When the team will not host Teleport, this is a commercial shape of the same job. You still map roles. Price is commercial.
Key features
- Proxy to infra
- Identity from your IdP
- Session logs
- Least privilege grants
Why we like it
A brokered path with session logs is the commercial buy when you will not staff an open plane.
Limits
Price is commercial. You still map roles.
Delinea
Best for secret Server and privilege on Windows estates
Delinea is Secret Server and privilege products. Common on Windows-heavy estates.
If the standing admin is a domain admin, this is a option those teams already know. It is not a cloud-native certificate plane.
Key features
- Secret Server
- Privilege manager
- Session control
- Enterprise directory hooks
Why we like it
Privilege on the estate you already run is the practical classic row next to CyberArk.
Limits
Commercial. Not a cloud-native cert plane.
Pomerium
Best for identity-aware proxy you can host
Pomerium is an identity-aware proxy. Access policies sit on the route. The core is Apache-2.0. The ZTNA list rows it as a cousin.
When the admin tool is a web app, a proxy that expires the session is PAM-shaped even if the brochure says ZTNA. You operate the proxy. It is not a password vault.
Key features
- Policy on the URL
- IdP in front
- Self-host
- TCP and HTTP routes
Why we like it
Ending the session on the admin URL is enough when the privilege is a browser tab, not a standing SSH key.
Limits
You operate the proxy. It is not a password vault. If the job is the path, open ZTNA.
What we left out
- BeyondTrust. Windows-heavy estates already put the name next to the other classic vault. CyberArk already covers that known PAM option, and public pricing is quote-only.
- HashiCorp Vault. Teams already keep the secret there. It is a secret store, not a session broker, and Boundary already sits next to it on this page.
Teleport’s early HN threads already treat the IdP as the front door. PAM still has to expire the session after that.
Questions before you buy
If procurement cannot get written answers, you are still buying a brochure.
- Does admin access end when the ticket closes, without someone editing a group?
- Are we buying a password vault, a session broker, or both, and which one do we already pay for?
- Can we export the session record if we leave the plane next year?
Expire the admin. If the product is really ZTNA with a vault, buy it as ZTNA. If the RFP wants a PAM desk, do not substitute Teleport and hope.
FAQs
Does PAM replace the IdP?
No. The IdP says who logged in. PAM says the admin session ends. Open identity protection.
Is Teleport ZTNA or PAM?
Both, for different buyers. PAM is the privileged session. The ZTNA list is the path to the app.
Can I keep a shared root?
No. That is the hole. A vault that still hands out a standing password is the wrong door.
Is this a scored bake-off?
No. Order is editorial.

