Vulnerability and exposure
Vulnerability Management Platforms Compared: 6 Scanners and Prioritization Tools
Assign the finding. A fourth scanner still has no owner on the ticket.
Expertise: Vulnerability and exposure · Level: Intermediate · 6 min read
A fourth scanner still has no owner on the ticket. The team already has 3 ways to find a CVE. The queue is green in the sense that it is full.
Vulnerability management is that assignment. The scanner is how you found it. Some platforms still scan assets you own. Others take findings you already have and make someone take them.
If the gap is a public name you did not know you had, start with attack surface work. This shortlist is the ticket that has an owner, a due date, and a risk that is not just CVSS.
Scanners you still run, prioritization layers on top of existing findings, and cloud VM that already lives in the account split the queue. Buy the assignment, not the fifth way to discover the same CVE.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We grouped by job: scan an asset you own versus queue and prioritize findings you already have. We also asked whether you operate it, and whether ownership is a first-class field.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| DefectDojo | Open finding queue you can host | Open finding queue · BSD-3-Clause · you host it |
| Faraday | Open-core workspace for findings you already collected | Open-core workspace · GPL / commercial · you host community |
| Qualys | Known enterprise scanner plus queue | Enterprise scanner · commercial · agents they sell |
| Tenable | The other known scanner estate | Nessus-shaped estate · commercial · agents they sell |
| Cisco Vulnerability Management | Kenna-shaped risk on a Cisco contract | Risk on findings · commercial · ex-Kenna |
| Vulcan | Aggregate findings into a queue you can assign | Aggregation · commercial · tickets they sell |
DefectDojo
Best for open finding queue you can host
DefectDojo ingests scanner exports and dedupes into findings. You operate it. DefectDojo is the finding queue you operate.
A second scanner is useless if the ticket is a spreadsheet, so this is the open finding desk. You staff it. Importers lag. It is not a network scanner by itself.
Key features
- Many parser importers
- Dedup on the public docs
- You host it
- BSD-3-Clause
Why we like it
Dedup into one finding is the job when you already have scans.
Limits
You staff it. Importers lag. Not a network scanner by itself.
Faraday
Best for open-core workspace for findings you already collected
Faraday is a workspace for pentest and scanner output. Community edition you can host. Enterprise if you pay.
When the work is still a pentest export, a workspace is the practical option. GPL on community. You still own the scan scope. Not Qualys.
Key features
- Workspaces
- Importers
- Self-host community
- Commercial extra
Why we like it
Pentest output needs a workspace, not another network scanner.
Limits
GPL on community. Not Qualys. You still own the scan scope.
Qualys
Best for known enterprise scanner plus queue
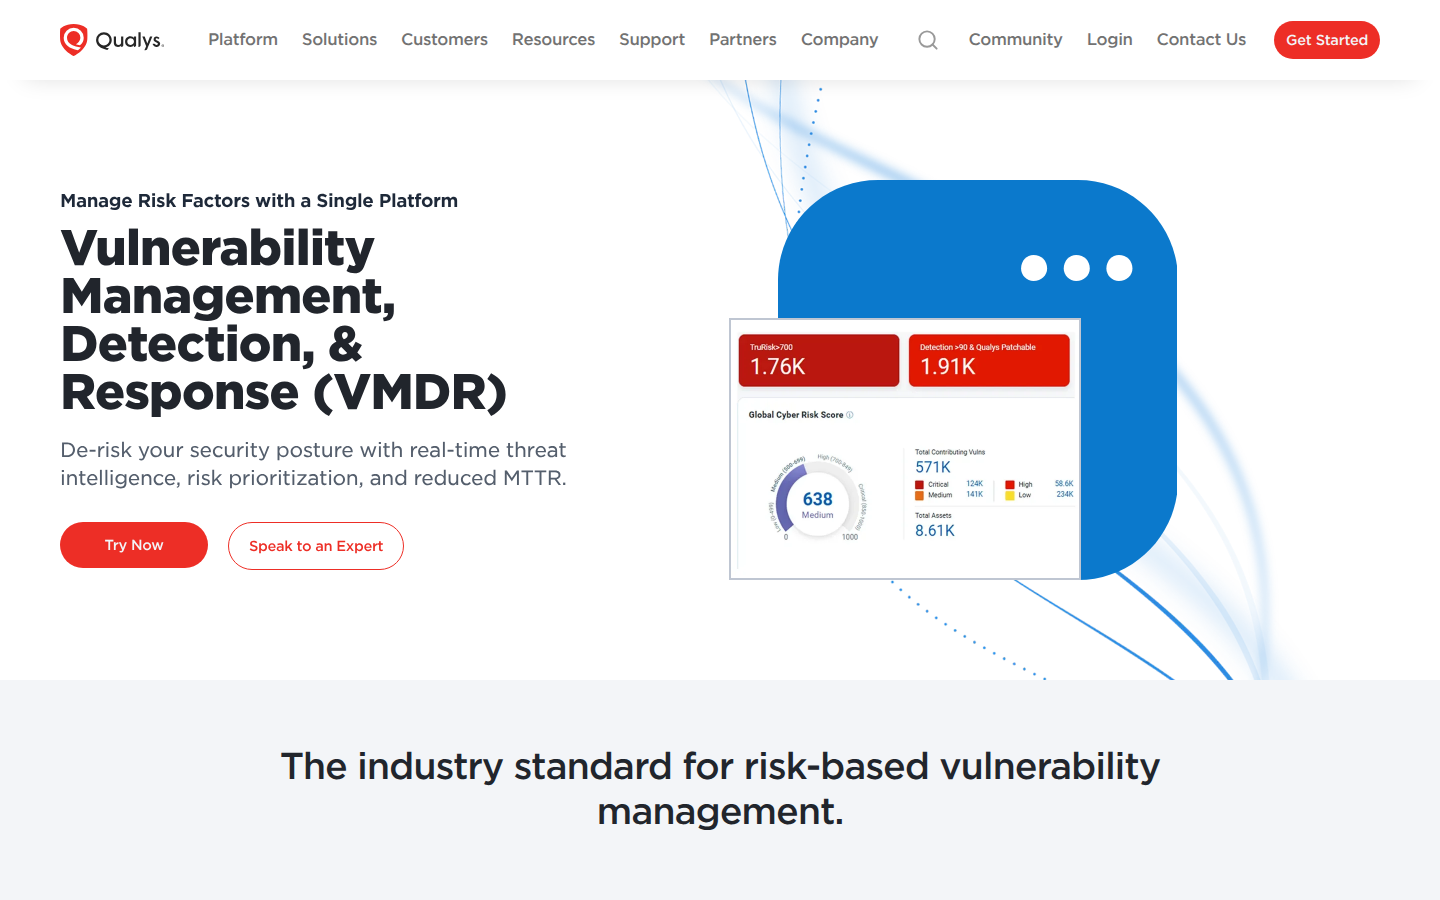
Qualys VMDR is the known scanner estate. Agents, appliances, a ticket story. Procurement already wrote the name.
If it is already scanning, start by feeding a queue or the built-in ticket, not a fourth scanner. Agent tax. Own assets only.
Key features
- Authenticated scan they sell
- Agents
- Dashboards
- Commercial
Why we like it
The estate you already scan with is the first commercial engine.
Limits
Commercial. Agent tax. Own assets only.
Tenable
Best for the other known scanner estate
Tenable Vulnerability Management, formerly Tenable.io, is Nessus at estate scale. Overlap with Nessus-the-engine is declared.
Second known scanner so Qualys is not a one-logo page. Noise. Own assets only.
Key features
- Nessus-shaped engine
- Estate console
- Agents they sell
- Commercial
Why we like it
The other known scanner estate keeps this page from becoming a single-vendor recap.
Limits
Commercial. Noise. Own assets only.
Cisco Vulnerability Management
Best for kenna-shaped risk on a Cisco contract
Kenna is now Cisco Vulnerability Management. The pitch is risk on findings you already have, not a new scanner brand.
Name the rename so old Kenna bookmarks still work. You still need scanners.
Key features
- Risk scoring they sell
- Connectors
- Cisco estate
- Commercial
Why we like it
Risk on findings you already have is a different buy than a new scanner logo.
Limits
Commercial. You still need scanners.
Vulcan
Best for aggregate findings into a queue you can assign
Vulcan sits on top of scanners. The product is prioritization and tickets. Nucleus is a sibling you can evaluate the same way.
When you already bought two scanners, the hole is the merge. Another console is the catch. Public pages are not a lab.
Key features
- Aggregation they sell
- Tickets
- Connectors
- Commercial
Why we like it
The merge is the product when two engines already run.
Limits
Commercial. Another console. Public pages are not a lab.
What we left out
- Rapid7 InsightVM. People want the Nexpose-shaped estate they already run. Qualys and Tenable already cover the enterprise scanner job on this page.
- Nucleus Security. Teams want another aggregator on top of scanners they already bought. Vulcan already covers that work, and Nucleus is the sibling you evaluate the same way.
VM threads treat the unowned finding as the real metric. A critical with no team is theater.
Questions before you buy
A quote that cannot answer these is selling a different product.
- Do two scanners on the same host we own become one ticket?
- Are we buying a scanner, a queue, or both, and which one is already paid for?
- Who owns a critical if the dashboard has no team field?
Buy the queue if you already scan. Start with attack surface if you cannot list the asset.
FAQs
Does this replace ASM?
No. ASM is the public name. Vulnerability management is the ticket. Those are different jobs. Open the matching list for the other one.
Scanner or queue first?
If you already scan, buy the queue. If you scan nothing, start with a scoped scanner on assets you own.
Will you publish exploits?
No.
Is this a scored bake-off?
No.

