Which ASPM queue should you hire: Dazz or Ox Security?
Choose Dazz (now Wiz UVM) when the painful week is finding-to-fix ownership across the scanners you already run. Choose Ox Security when you need Active ASPM platform breadth and reachable risk scored on a Pipeline Bill of Materials.
Monday starts the same way in a lot of AppSec shops: SAST, SCA, container, and cloud scanners have already dumped hundreds of findings into separate UIs. Someone still has to dedupe them, name an owner, open the ticket or PR, and chase the fix before the next release train.
That week splits into stages. One stage is the remediation queue after scanners fire: correlate findings, map owners, push tickets, and cut mean time to remediate. The other stage is ASPM platform breadth: inventory the pipeline, score which issues are actually reachable in what you ship, and fail CI on policies you trust. Between these two, Dazz productized the first stage as a unified remediation engine and now ships that shape as Wiz Unified Vulnerability Management inside Wiz Exposure Management after the November 2024 acquisition. Ox Security productizes the second stage around VibeSec, Code, Cloud, and Agentic Pentester on a Pipeline Bill of Materials.
If you already shortlisted Ox against another ASPM graph vendor, see Ox Security vs Cycode. This compare is the remediation-ownership fork, not that breadth-vs-breadth pair.
| Job | Unified remediation and fix ownership across ingested scanners (live path: Wiz UVM) | Active ASPM platform breadth with PBOM lineage across VibeSec, Code, Cloud, and Agentic Pentester |
|---|---|---|
| How a bad day closes | Dedupe findings, assign owners, kick off tickets or fix PRs, and ship AI remediation guidance on the queue | Prioritize reachable and exploitable risk on PBOM context; validate with Agentic Pentester; orchestrate remediation on the platform |
| What fails CI | Not the primary native CI gate; closes work after your existing scanners fire | OX Code pipeline scanning and blocking across SAST, SCA, secrets, IaC, and containers |
| Deploy | Wiz platform connectors / UVM ingest into the stack you already run | Connect SCM, CI/CD, and cloud; platform features list on-prem and broker options |
| License/pricing | Sales-quoted inside Wiz packaging; dazz.io no longer publishes a standalone price table | Sales-quoted Get Quote; meters by AI user, contributing developer, cloud asset, and agent hours |
| Who operates it | AppSec and vulnerability management owning the remediation queue and owner routing | AppSec and platform engineering; developers meet VibeSec in the IDE; security owns PBOM and issues |
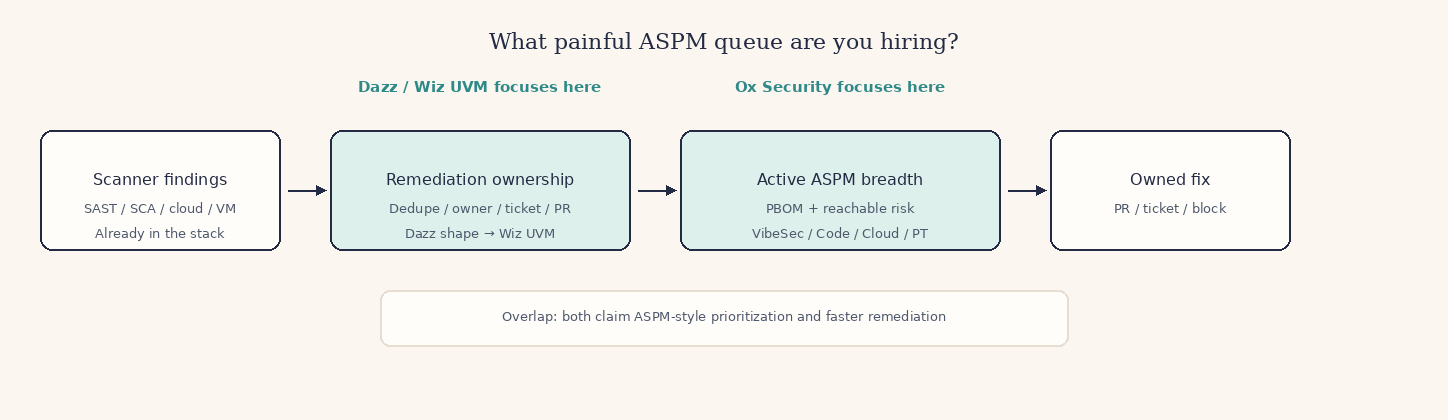
That is the Dazz claim operators still make after the acquisition: ingest the scanners you already bought, then prioritize and own the fix. On 6 August 2025 Wiz described Wiz UVM as coming from the Dazz acquisition, with ingest, dedupe, ownership, and AI remediation on the Exposure Management path.
We reviewed first-party documentation, public pricing pages, acquisition and product posts, and live community threads. We did not test the products in paid production environments, so this is not a hands-on benchmark.
Dazz (Wiz ASPM / UVM)
Ox Security
Editions and pricing
Neither side publishes a trustworthy self-serve dollar table a spreadsheet can freeze without sales. Packaging still differs: Dazz no longer sells from dazz.io as a standalone SKU, while Ox sells four named pillars with explicit meters.
| Public price table | No standalone dazz.io SKU (verified 11 Sep 2026; site redirects to Wiz). Expect Wiz sales packaging for UVM / Exposure Management | Get Quote on ox.security/pricing (verified 11 Sep 2026). No public dollar SKU |
|---|---|---|
| Named lines | Wiz UVM inside Exposure Management; remediation workflows shared with Wiz ASPM / Wiz Code paths | OX VibeSec, OX Code, OX Cloud, OX Agentic Pentester, plus OX Platform features |
| What the quote usually meters | Wiz platform commercial terms (confirm UVM / Exposure Management modules in the same quote) | AI users, contributing developers, cloud assets, and agent hours, depending on pillars selected |
| Free forever SKU | None as a standalone Dazz free tier | None on the public pricing page |
If procurement needs a published monthly number before a call, both paths will stall that spreadsheet. Ask which Wiz modules cover UVM versus which Ox pillars are in scope, and how contributing developers or AI users are counted.
Closing the remediation queue
This is the queue operators close when the scanners already exist and the backlog does not. The work is correlation, ownership, SLA, and getting a fix into the right developer’s hands.
| Primary unit of work | Ingested findings from existing vuln, SAST, DAST, and related scanners, then deduped issues with owners | Platform issues with PBOM lineage; remediation orchestration opens PRs, tickets, and messages |
|---|---|---|
| Owner routing | Assign and kick off remediation workflows to resource owners across security, development, and infrastructure | Developer dedicated issue view on OX Code; SLA and MTTR tracking on the platform |
| Fix artifacts | AI-generated remediation guidance, root-cause fixes, and one-click fix PRs described on the Wiz Exposure Management path | AI remediation recommendations plus open PR / ticketing / messaging orchestration |
| What teams argue about | Whether UVM replaces a separate ASPM graph or only closes the queue on top of scanners already paid for | Which pillar owns the ticket when Code, Cloud, and Agentic Pentester all touch the same service |
Between these two, do not buy “remediation” as a unique checkbox. Both talk about faster fixes. Buy the week you actually staff: closing an ownership queue on ingested scanner output, or living inside Ox’s platform issues and pillar policies.
Scoring reachable risk on ASPM breadth
This is the other stage: not only “who owns the ticket,” but whether the finding is reachable in what you ship, and whether the platform covers prompt-to-runtime controls in one product.
| Context graph | Enrichment against the Wiz Security Graph when findings land in UVM / Exposure Management | Pipeline Bill of Materials lineage from source control through pipeline and cloud |
|---|---|---|
| Reachability proof | Prioritization with code-to-cloud and runtime context on the Wiz path; not Dazz’s original standalone center | Reachable and exploitable prioritization; Agentic Pentester validates exploitability and links it back to code |
| Native scanners | UVM is built to ingest third-party scanners; Wiz Code adds native AppSec scanning on the wider Wiz path | OX Code covers SAST, SCA, secrets, IaC, containers, CI/CD, and related engines in-platform |
| AI-era control point | AI remediation guidance and IDE / MCP workflows on the Wiz path | VibeSec governs AI users, MCPs, skills, and generated code before insecure patterns land |
In a February 2026 r/devsecops thread on best ASPM tools, operators pointed at Ox Security for pulling scanner signals and pipeline context into one prioritization view for a DevSecOps workflow. That matches the breadth stage: context on what actually deploys, not only a prettier Jira for CVEs. On 12 March 2026 Ox announced Agentic Pentester for continuous AI-driven exploit validation tied back to source.
Where they overlap
Both show up on ASPM shortlists. Both promise prioritization beyond raw severity and both sell remediation workflows that open tickets or PRs. Both are sales-quoted enterprise buys in 2026. If your RFP only says “ASPM with ownership and faster MTTR,” both will tick boxes.
When to use both
Running both is uncommon. Teams that already standardized on Wiz for cloud risk sometimes add UVM to close the remediation queue without buying a second ASPM platform. Teams that want prompt-to-runtime ASPM controls and native OX Code gates usually pick Ox and skip a separate aggregator.
Skip Ox for this pair if the buying committee already lives in Wiz and the open pain is ownership and MTTR on findings from scanners you will keep. Skip a Dazz-shaped UVM buy for this pair if you need Ox’s PBOM-backed Active ASPM pillars, VibeSec at the prompt, and Agentic Pentester proof as the default operating model.
Decide the queue first. If the product must close finding-to-fix ownership across scanners you already run, that is the Dazz shape now sold as Wiz UVM. If the product must be PBOM-backed breadth with named pillars and reachable risk scoring, that is Ox. Only then open the sales quotes.
FAQs
Is Dazz still a standalone product?
No standalone dazz.io buy in 2026. Wiz announced the acquisition on 21 November 2024, and dazz.io redirects to that story. The remediation job now ships as Wiz UVM inside Exposure Management, with related ASPM remediation on the Wiz path.
Are Dazz and Ox Security the same ASPM?
No. Both show up on ASPM shortlists, but between these two Dazz centered unified remediation and ownership across scanners, while Ox centers PBOM-backed platform breadth with reachable risk scoring.
Do either publish list prices?
Not a trustworthy self-serve dollar table for this pair on the first-party surfaces we checked on 11 Sep 2026. Expect sales-quoted contracts.
Is this a scored bake-off?
No. Order is editorial.

