Cloud Security
Best CIEM Tools for Cloud Entitlements in 2026
Right-size human and non-human permissions before an overprivileged role becomes blast radius.
Capital One’s 2019 cyber incident disclosure says the event affected about 100 million individuals in the United States and about 6 million in Canada.
Court filings and later technical writeups showed how a foothold on a misconfigured WAF became a data read once the attached IAM role could list and fetch far more S3 objects than a firewall instance needed. The configuration check can look green while the entitlement still owns the blast radius.
That is the cost of getting cloud permissions wrong. CSPM answers whether a resource is exposed or misconfigured. CIEM answers who can still reach production data after the foothold, including human users, service roles, and federated identities across AWS, Azure, and GCP.
The category also moved. Standalone entitlement products were absorbed into CNAPP suites. Microsoft retired Entra Permissions Management on November 1, 2025, and pointed customers toward partners and Defender CSPM identity features. Buyers now choose between graph CIEM inside a platform, identity-first analysis with JIT, and open-source AWS path mapping.
How we evaluated
We read first-party CIEM and CNAPP product pages, docs, licenses, and pricing CTAs. We asked whether the tool computes effective permissions across clouds, whether unused or toxic entitlements are a named job, whether JIT or zero standing privilege exists, and whether remediation is policy right-sizing or only a finding export. Marketing pages count as claims, not as proof two tools do the same work.
| Tool | Best for | What to check |
|---|---|---|
| Wiz | Graph CIEM inside a CNAPP | Commercial · multi-cloud · Security Graph |
| Tenable Cloud Security | Identity-first CIEM plus JIT | Commercial · Ermetic lineage · quote |
| Sonrai Security | Least privilege with identity platform depth | Commercial · Cloud Permissions Firewall |
| Prisma Cloud | RQL-queryable entitlements in a CNAPP | Commercial · Palo Alto · multi-cloud |
| Britive | Zero standing privilege / JIT access | Commercial · AWS/Azure/GCP/OCI |
| PMapper | Open-source AWS privilege-path mapping | AGPL-3.0 · AWS-focused · self-hosted |
Wiz
Best for graph-based CIEM inside a CNAPP
Wiz maps effective access between human and non-human identities and cloud resources on the Security Graph, including boundaries, ACLs, SCPs, and related controls. First-party CIEM pages emphasize unused admin permissions, missing MFA, excessive privileges, and attack paths that reach admin identities or sensitive data.
CIEM Explorer and the Non-Human Identities dashboard sit next to vulnerability, secret, and data risk. That is the platform cut: entitlement risk ranked with the rest of the cloud attack surface rather than as a standalone IAM spreadsheet.
Key features:
- Effective permissions across IdP, SaaS, and cloud identities
- Security Graph attack paths to crown-jewel assets
- Least-privilege policy generation and guided remediation
- Non-human identity monitoring for privileged service accounts
Why we like it:
When the morning queue is which identity can still reach this datastore after the foothold, a graph that already holds vulns and data context is the right shape.
Limits:
Commercial CNAPP packaging. CIEM is not sold as a tiny standalone SKU on the pages we read. Multi-cloud onboarding and graph scale are a security review, not a weekend CLI.
License or pricing: Commercial. Demo and guided-tour CTAs. No public per-resource list price on the CIEM pages we read.
Tenable Cloud Security
Best for identity-first CIEM with JIT access
Tenable Cloud Security carries the Ermetic entitlement engine into Tenable One Cloud Exposure. First-party CIEM pages describe continuous analysis of entitlements across AWS, Azure, and GCP, toxic combinations, stale or overly broad access, and just-in-time access to enforce least privilege.
Identity risk is correlated with misconfigurations, vulnerabilities, and sensitive data so remediation can target exposures that actually compose into blast radius. IdP integrations such as Entra ID, Okta, and Google Workspace show federated users mapped into cloud accounts.
Key features:
- Multi-cloud effective permission and toxic entitlement analysis
- JIT access controls for least privilege
- Correlation of identity risk with vulns and data exposure
- IdP integrations for federated identity inventory
Why we like it:
Teams that still remember Ermetic as the identity-first CIEM buy get that depth inside Tenable exposure management instead of a separate orphaned SKU.
Limits:
Commercial quote path. Packaged as Tenable One Cloud Exposure / CNAPP, not a free analyzer. Confirm CIEM module scope on the contract, not only the marketing noun.
License or pricing: Commercial. Request-pricing and demo CTAs. No public CIEM-only list rate on the pages we read.
Sonrai Security
Best for least-privilege enforcement on an identity platform
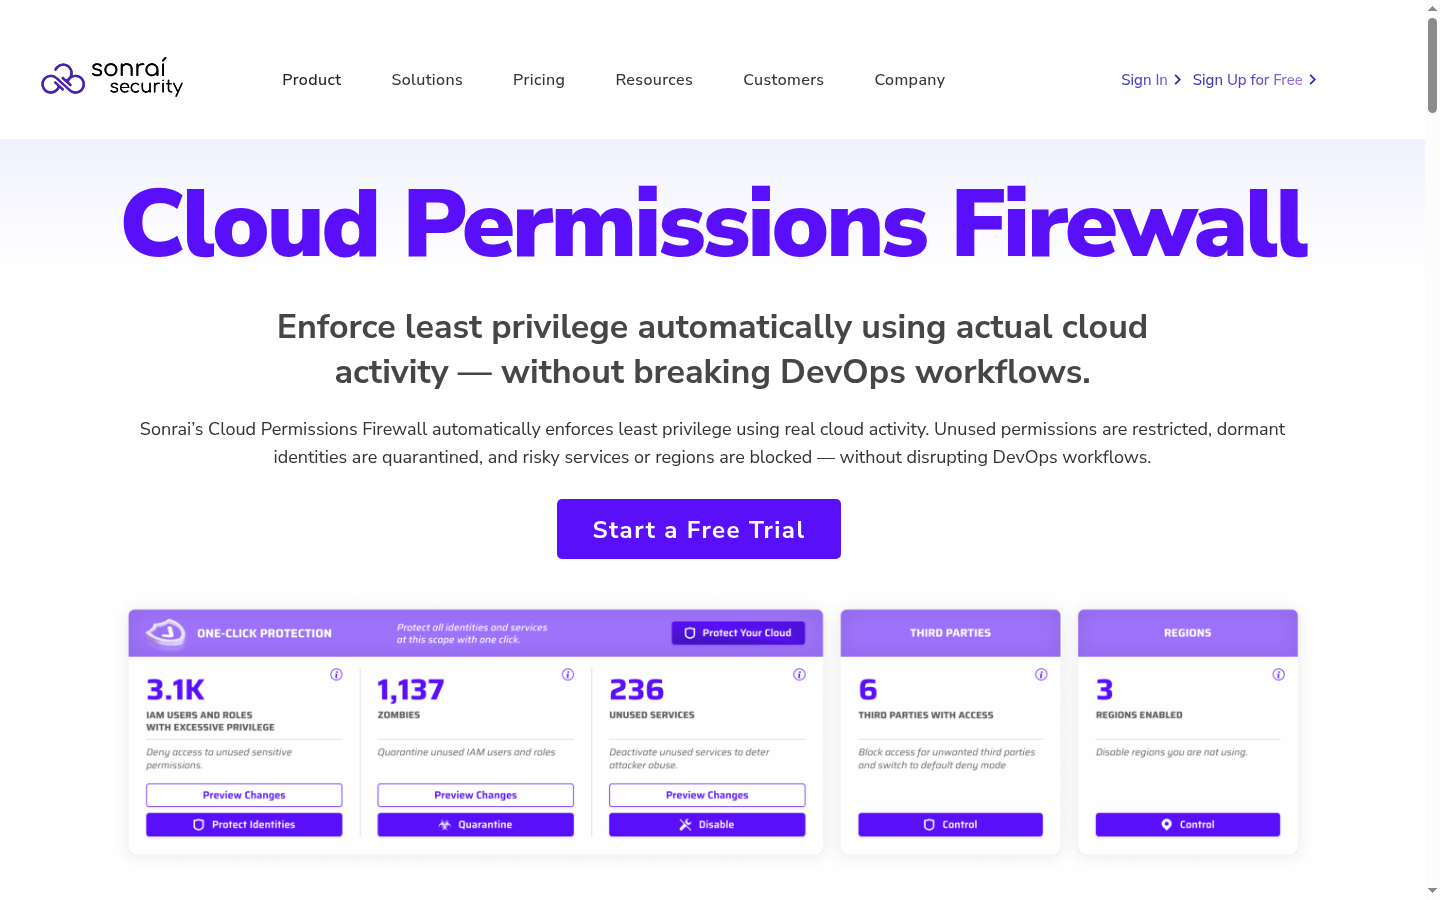
Sonrai positions as a cloud identity and access platform with a path to least privilege and a Cloud Permissions Firewall style control for privileged access. The public story is identity-to-permission governance across AWS, Azure, and GCP rather than a general CNAPP catalog.
That makes Sonrai the specialized seat when toxic permission paths and standing privilege removal are the program, and when you do not want identity work buried as a module inside a larger posture suite.
Key features:
- Cloud identity and access platform across major CSPs
- Least-privilege workflows aimed at DevOps velocity
- Cloud Permissions Firewall style privileged access control
- Public pricing and resource library entry points
Why we like it:
When the RFP language is identity graph and least privilege first, Sonrai still reads as a dedicated CIEM-shaped platform rather than a CNAPP checkbox.
Limits:
Commercial. Confirm multi-cloud depth and enforcement modes in a demo. Not a substitute for CSPM workload scanning.
License or pricing: Commercial. Public pricing CTA on the site. Demo and quote for production scope.
Prisma Cloud
Best for RQL-queryable entitlements inside Palo Alto CNAPP
Prisma Cloud CIEM analyzes entitlements across clouds and turns RQL queries into IAM security policies with compliance and remediation context. First-party pages frame identity risk inside the broader CNAPP: posture, workload, and network-aware scoring.
For estates already standardized on Palo Alto, entitlement queries that look like the rest of Prisma operations can beat introducing a second identity console.
Key features:
- Cross-cloud entitlement analysis in Prisma Cloud
- RQL queries over identities and permissions
- Integration with CNAPP posture and workload context
- Policy-oriented remediation for IAM findings
Why we like it:
Operators who already live in RQL get CIEM without learning a second query language or buying a pure-play graph from scratch.
Limits:
Enterprise CNAPP commercial packaging. CIEM depth varies by edition. Per-managed-resource commercial models are a recurring community complaint for this sector.
License or pricing: Commercial via Palo Alto. Quote-based. No public CIEM unit price on the pages we read.
Britive
Best for zero standing privilege and JIT cloud access
Britive sells runtime privileged access for humans, non-human identities, and AI agents with zero standing privileges across AWS, Azure, GCP, and OCI. First-party pages treat JIT as more than a temporary ticket: standing admin disappears until the task needs it.
That is a different job from discovering unused actions. Discovery tools still matter for the backlog of wildcards you already granted. Britive is the seat when the program is to stop leaving those grants hot.
Key features:
- Zero standing privileges (ZSP) across major clouds
- JIT privileged access for humans and NHIs
- API-first, agentless access model on first-party pages
- Break-glass and on-call access patterns
Why we like it:
CIEM without an enforcement path leaves a spreadsheet of overprivileged roles. Britive is built for the access moment, not only the inventory.
Limits:
Commercial. Not a full CNAPP. You still need discovery and posture elsewhere. Scope which apps and clouds sit behind JIT before ripping standing roles.
License or pricing: Commercial. Request-pricing CTA. No public per-seat list rate on the pages we read.
PMapper
Best for open-source AWS privilege-path mapping
Principal Mapper (PMapper) is NCC Group’s open-source tool and library for modeling AWS IAM users and roles, then checking privilege escalation and alternate paths an attacker could take. It is AWS-focused analysis you run yourself, not a multi-cloud SaaS console.
The AGPL-3.0 license and GitHub releases make it the credible OSS seat on a CIEM shortlist when the job is local graphing of trust policies and escalation edges before you pay for a hosted platform.
Key features:
- Local model of AWS account or organization IAM
- Privilege escalation and alternate-path checks
- Graph-oriented view of effective permissions
- AGPL-3.0 source on GitHub
Why we like it:
Pentest and cloud IAM reviews still need a tool that answers who can become admin from here without a sales call. PMapper is that AWS graph.
Limits:
AWS-only. You operate it. AGPL-3.0 may constrain how you ship derivatives. Not a continuous multi-cloud CIEM platform with JIT.
License or pricing: AGPL-3.0 open source. No vendor subscription. Your compute and IAM read permissions are the cost.
How to choose a CIEM tool
Start from the failure you cannot afford. If an overprivileged role can still read production data after a foothold, you need effective-permission analysis and a right-sizing path. If standing admin is the cultural default, add JIT. If AWS is the only cloud and you can run a local graph, OSS can clear the first review.
- Platform already chosen? Prefer the CIEM module in Wiz, Prisma, or Tenable before adding a seventh console.
- Identity program first? Shortlist Tenable Cloud Security, Sonrai, or Britive for depth and enforcement.
- AWS-only tactical review? Run PMapper (and first-party Access Analyzer) before the RFP.
- Retired Microsoft SKU? Entra Permissions Management is not a live option after November 1, 2025.
What we left out
- Orca Security and CrowdStrike Falcon Cloud for credible CNAPP CIEM peers; cut to keep the mix platform vs identity-first vs JIT vs OSS.
- AWS IAM Access Analyzer for first-party unused and external access findings; belongs in every AWS program, not as a sixth commercial seat.
- Delinea PCCE as Microsoft’s named migration partner after MEPM retirement; evaluate if you are exiting Entra Permissions Management.
- Cloudsplaining for strong AWS IAM assessment OSS; PMapper covers the privilege-path graph seat here.
What practitioners argue about CIEM
Live threads keep returning to the same split: least privilege is hard to write by hand, commercial CIEM often prices per managed resource, and open-source graphs still matter for AWS reviews.
Hacker News · Mar 2024
“The sector of tools is called CIEM. Cloud Infrastructure Entitlement Management. Here’s the thing though… PA and MS charge PER MANAGED RESOURCE. It’s crazy.”
The same comment names CloudKnox (later Microsoft Permissions Management) and Prisma as the commercial shape. The dissenting pressure is that entitlement analysis feels like it should be platform-native, not a meter.
Information Security Stack Exchange · 2019
“IAM access analyzer is an interesting service that might be some help to you. It is quick and free way to audit cross account access given to AWS resources.”
Practitioners reach for first-party analyzers for cross-account trust even when commercial CIEM is on the roadmap. That is the gap PMapper and Access Analyzer still fill on AWS-only desks.
Hacker News · May 2015
“Have you ever tried to setup AWS IAM permissions for a user pursuant to the principle of least privilege? Because Amazon’s APIs are about as far from friendly as you can get in this respect.”
The older least-privilege frustration still explains why CIEM products sell unused-permission mining and policy generation: humans lose patience writing action-level allows by hand.
If identity risk must sit next to vulns and data on one graph, start with Wiz or Prisma. If entitlement depth and JIT are the program, shortlist Tenable Cloud Security, Sonrai, or Britive. Keep PMapper for AWS privilege-path reviews you will run yourself.
FAQs
Is CIEM the same as CSPM?
No. CSPM finds misconfigurations and posture gaps on cloud resources. CIEM computes who can do what with which entitlements and helps right-size those permissions. Many CNAPPs ship both.
Did Microsoft kill Entra Permissions Management?
Yes. Support ended November 1, 2025. Microsoft pointed customers to partners such as Delinea and to CIEM capabilities inside Defender for Cloud CSPM. It is not on this shortlist as a live product.
Can open source replace a CIEM platform?
For an AWS privilege-path review, PMapper can answer hard questions without a subscription. Continuous multi-cloud entitlement ops, IdP mapping, and JIT usually need a commercial desk.
Is this a scored bake-off?
No. Order is editorial.

