Identity and Access
Passkey Tools in 2026: Libraries vs Managed Platforms
Ship enrollment that can recover when the only phone is lost. The backup must not be the old password hash by accident.
Expertise: Identity and Access · Level: Intermediate · 6 min read
Someone lost the only phone that held the passkey, and the backup was still the old password hash. Enrollment that cannot recover is how the weekend demo never ships. 1 lost phone should not restore the old password hash.
A WebAuthn library you call from the app is one path. A managed identity platform that already issues passkeys is another. A hardware authenticator in someone’s pocket is a third. Mixing those jobs is how passkey projects stall.
The IdP the team already has may offer passkeys as a checkbox. The checkbox does not design recovery. This shortlist is how you issue and recover the credential.
Choose the path you can support on Monday: call a library, turn on the platform, or issue a key, and write the recovery before the first demo.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether you implement WebAuthn or the IdP does, whether you store the credential, whether recovery is documented, and whether the docs name a platform authenticator path you can try on a device you own.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| SimpleWebAuthn | Node and browser WebAuthn you can read | Node and browser · MIT · you store credentials |
| go-webauthn | Go WebAuthn on a server you own | Go library · BSD-3-Clause · you store credentials |
| Cisco Duo | IdP passkeys next to the MFA you already bought | IdP passkeys · commercial · existing MFA estate |
| Microsoft Entra ID | Passkeys on the directory you already have | Directory policy · Microsoft terms · workforce tenant |
| Corbado | Passkey-first SaaS for an app login | Passkey SaaS · commercial · hosted ceremony |
| Yubico | Hardware keys and reference libraries | Hardware keys · mixed libs · you write recovery |
SimpleWebAuthn
Best for node and browser WebAuthn you can read
Server and browser packages for WebAuthn. Types you can follow. The docs start from an origin you own.
If the app is Node and the password is still the only factor, this is the library you read. You still design recovery. An origin mismatch fails closed, and that is a feature.
Key features
- @simplewebauthn/server
- Browser helper
- MIT
- Passkey examples on the public docs
Why we like it
A typed WebAuthn stack you can read beats a SaaS overlay on a Node app you already own.
Limits
You still design recovery. An origin mismatch fails closed. That is a feature.
go-webauthn
Best for go WebAuthn on a server you own
The Go library people actually import. Registration and assertion. You store the credential yourself.
When the app is Go, a SaaS passkey overlay is often vanity, because you already own the user table. Recovery is still a product decision.
Key features
- Registration and login
- You store credentials
- BSD-3-Clause
- Actively kept
Why we like it
A Go login should call a Go library. You keep the credential next to the user you already have.
Limits
You own the user table. Recovery is still a product decision.
Cisco Duo
Best for IdP passkeys next to the MFA you already bought
Duo added passkeys on the IdP you may already run. The human enrolls in their prompt, not in your app code.
If the lock is already Duo, start there before you write a WebAuthn server. App-owned credentials still need a library.
Key features
- Passkeys on the public docs
- Existing MFA estate
- SSO they sell
- Commercial
Why we like it
Humans already enroll here. A second ceremony in app code needs a reason.
Limits
Commercial. App-owned credentials still need a library.
Microsoft Entra ID
Best for passkeys on the directory you already have
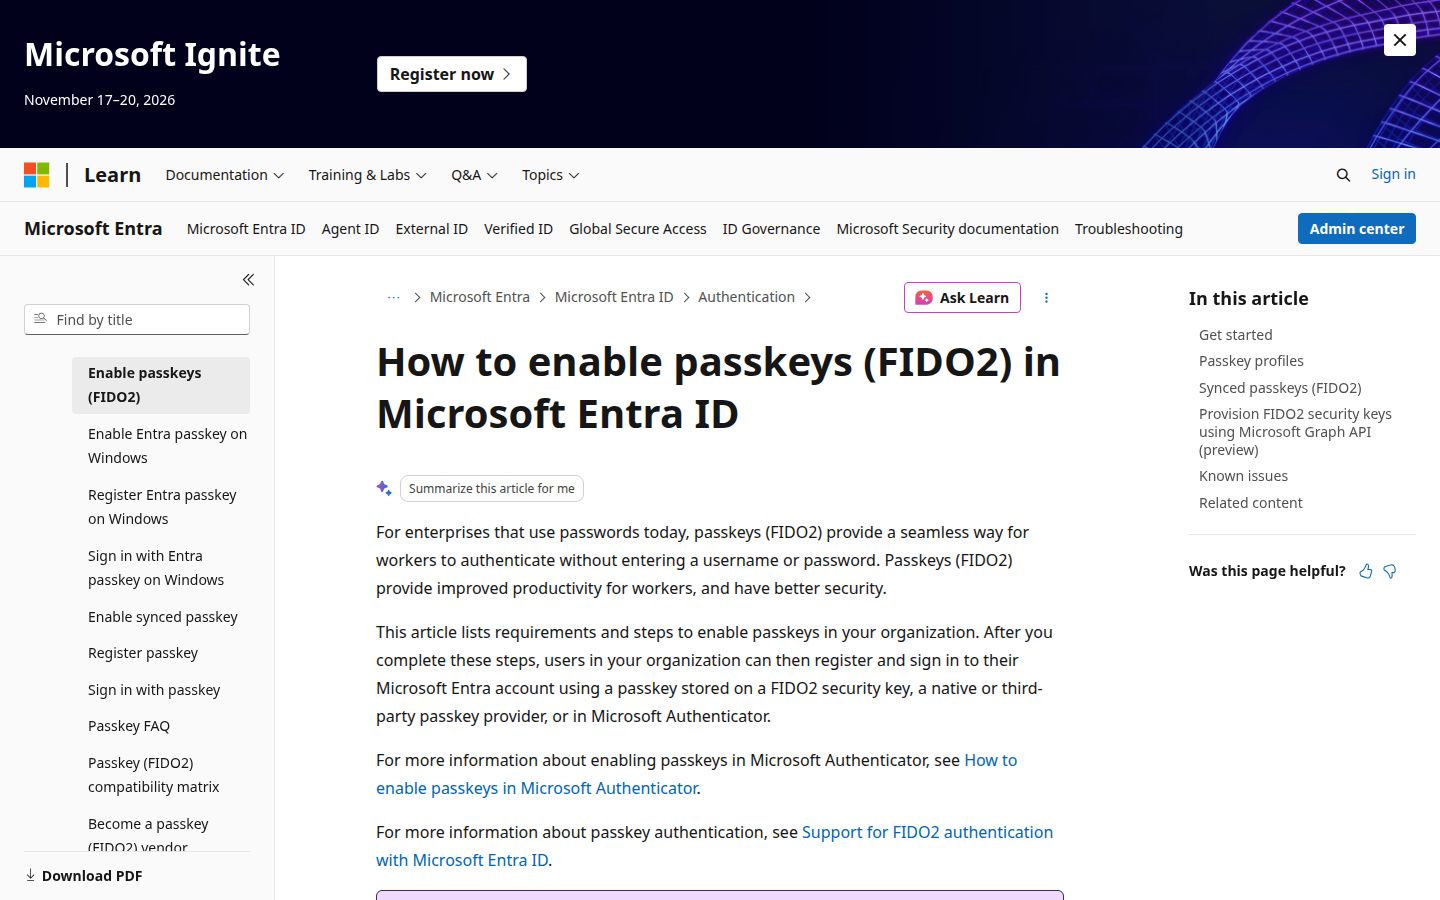
Entra documents FIDO2 and passkey sign-in for the workforce tenant. The control is a directory policy, not a Node package.
A lot of humans already live here, so do not invent a second login. Consumer apps still need a library. License SKUs apply.
Key features
- FIDO2 / passkey policy
- Same Entra tenant
- Conditional Access neighbor
- Microsoft docs
Why we like it
Honesty. The directory you already have is the first passkey control for workforce apps.
Limits
Workforce-shaped. Consumer apps still need a library. License SKUs apply.
Corbado
Best for passkey-first SaaS for an app login
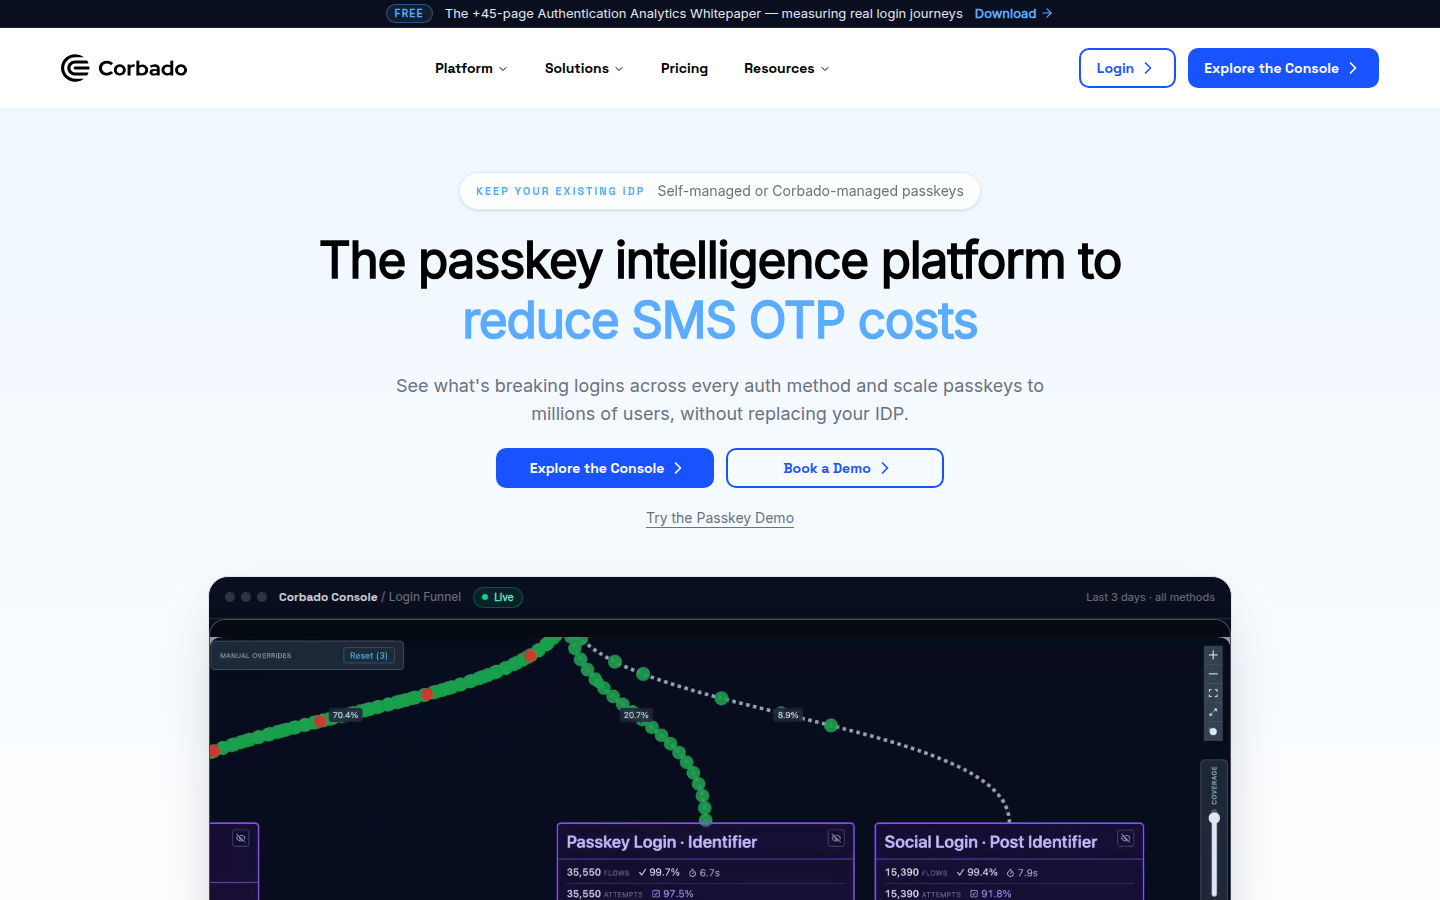
Corbado sells passkey login as a service. SDKs in front of your users. You are not storing the authenticator data.
When you will not staff WebAuthn, a specialist SaaS is the commercial option when you will not staff WebAuthn. The catch is vendor lock on the login, so recovery still needs a story you can export.
Key features
- Passkey UI they ship
- SDKs
- Hosted ceremony
- Commercial
Why we like it
If you will not staff the ceremony, paying for one is clearer than a half-built library.
Limits
Vendor lock on the login. Commercial. Recovery still needs a story.
Yubico
Best for hardware keys and reference libraries
YubiKeys plus developer libraries. WebAuthn, FIDO2, and the older OTP stack. The key is an object a human can lose.
A passkey that only lives in one phone vendor is a different risk than a key on a ring, so hardware is the other side of the split. Libraries are not an IdP.
Key features
- Hardware authenticators
- Reference libs
- FIDO2 on the public docs
- You still write recovery
Why we like it
A key a human can hold is a different recovery story than a cloud-bound passkey.
Limits
Hardware cost. Lost-key process. Libraries are not an IdP.
What we left out
- Auth0. People want the IdP they already pay for. This page is WebAuthn libraries plus the two IdPs already in many estates, not an identity-platform bake-off.
- Passage by 1Password. Teams want a passkey SaaS without staffing the ceremony. Corbado already covers that work on this page.
Passkey threads treat recovery as the real product. A demo origin is not a program.
Questions before you buy
If a first-party page cannot answer these, keep shopping.
- Can we register and assert on a staging origin we own?
- Do we own the user table, or do humans already live in an IdP?
- What happens when the phone is gone and the hardware key is in a drawer?
Turn on passkeys on an IdP you already pay for, and write recovery. Do not call a YubiKey an IdP.
FAQs
Is a passkey MFA?
It can replace the password plus a second factor. Say what your IdP actually enrolled.
Library or IdP?
IdP if humans already live there. Library if the app owns the user table.
What about recovery?
Design it before launch. A lost phone is not an afterthought.
Is this a scored bake-off?
No. Order is editorial.

