Platform security
Best IaC Scanners for Terraform CI in 2026: 6 Tools Compared
Fail the pull request on the Terraform you are about to apply. A Monday CSPM ticket is too late.
Expertise: Platform security · Level: Intermediate · 6 min read
Friday’s merge put a public security group in the account. Monday’s CSPM ticket was the first time anyone saw it. The file had already been applied.
NSA and CISA’s Kubernetes Hardening Guide (updated August 2022) exists to stop common misconfigurations before they sit in the cluster. An IaC scanner fails the pull request on the plan you are about to apply. A live-account scan is posture, which is a different product.
Policy-as-code you host, vendor IaC sitting on the PR, and checks that only run after apply are different gates. Live-account findings belong on CSPM tools. Fail the file first.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about Terraform coverage, custom policies, CI exit behavior, and whether findings point back to the resource a developer actually edits. A platform that only sees the live account missed, because that job is CSPM.
For this category a small fixture is possible: an intentionally open Terraform security group on infrastructure you control.
| Tool | Best for | What to check |
|---|---|---|
| Checkov | Open IaC scan you can run in CI | Open IaC · Apache-2.0 · many flavors |
| KICS | Open queries on IaC you already wrote | Query pack · Apache-2.0 · SARIF out |
| Terrascan | Open policy runner on Terraform you own | Policy packs · Apache-2.0 · Terraform-shaped |
| Trivy | One binary after tfsec merged in | Config scan · Apache-2.0 · tfsec successor |
| Conftest | Rego on any file you already have | You write Rego · Apache-2.0 · many inputs |
| Snyk IaC | Commercial IaC next to Snyk OSS | PR annotations · commercial / free tier · same Snyk tenant |
Checkov
Best for open IaC scan you can run in CI
Checkov scans Terraform, CloudFormation, Kubernetes YAML, and more. Policies you can extend. Prisma stewards it.
Fail the plan before CSPM opens a Tuesday ticket. Noise on generated modules is the catch. Prisma gravity. Not a live-account CSPM.
Key features
- Many IaC flavors
- Custom policies
- Apache-2.0
- CI on the public docs
Why we like it
A CI fail on the plan is the first control worth installing.
Limits
Noise on generated modules. Prisma gravity. Not a live-account CSPM.
KICS
Best for open queries on IaC you already wrote
Keeping Infrastructure as Code Secure. Query-based. Checkmarx opened it. You run the engine.
Second open engine so Checkov is not a one-logo open row. Query tuning is yours. You still own false friends.
Key features
- Query pack
- Many platforms they list
- Apache-2.0
- SARIF out
Why we like it
A second open query engine keeps the open row from becoming a recap.
Limits
Query tuning. You still own false friends.
Terrascan
Best for open policy runner on Terraform you own
Terrascan evaluates IaC against policies. Tenable-adjacent history. You run it in CI.
Third open runner so the page is not a Checkov recap. Mind the project pulse. Read the current repo before you promise it.
Key features
- Policy packs
- Terraform-shaped
- Apache-2.0
- CI
Why we like it
Another open runner is useful when you already rejected the first pack’s noise.
Limits
Mind the project pulse. Read the current repo before you promise it.
Trivy
Best for one binary after tfsec merged in
Trivy scans images, filesystems, and IaC. tfsec merged into it. The SBOM and Kubernetes lists already name Trivy. Here it is the Terraform misconfig scan. Overlap declared.
If Trivy is already in CI, enable config before you add a fourth engine. One binary, many jobs. Say which job you turned on.
Key features
- config scan
- Same binary as image scan
- Apache-2.0
- tfsec successor
Why we like it
The binary you already run is the first IaC job. Enable it.
Limits
One binary, many jobs. Say which job you turned on.
Conftest
Best for rego on any file you already have
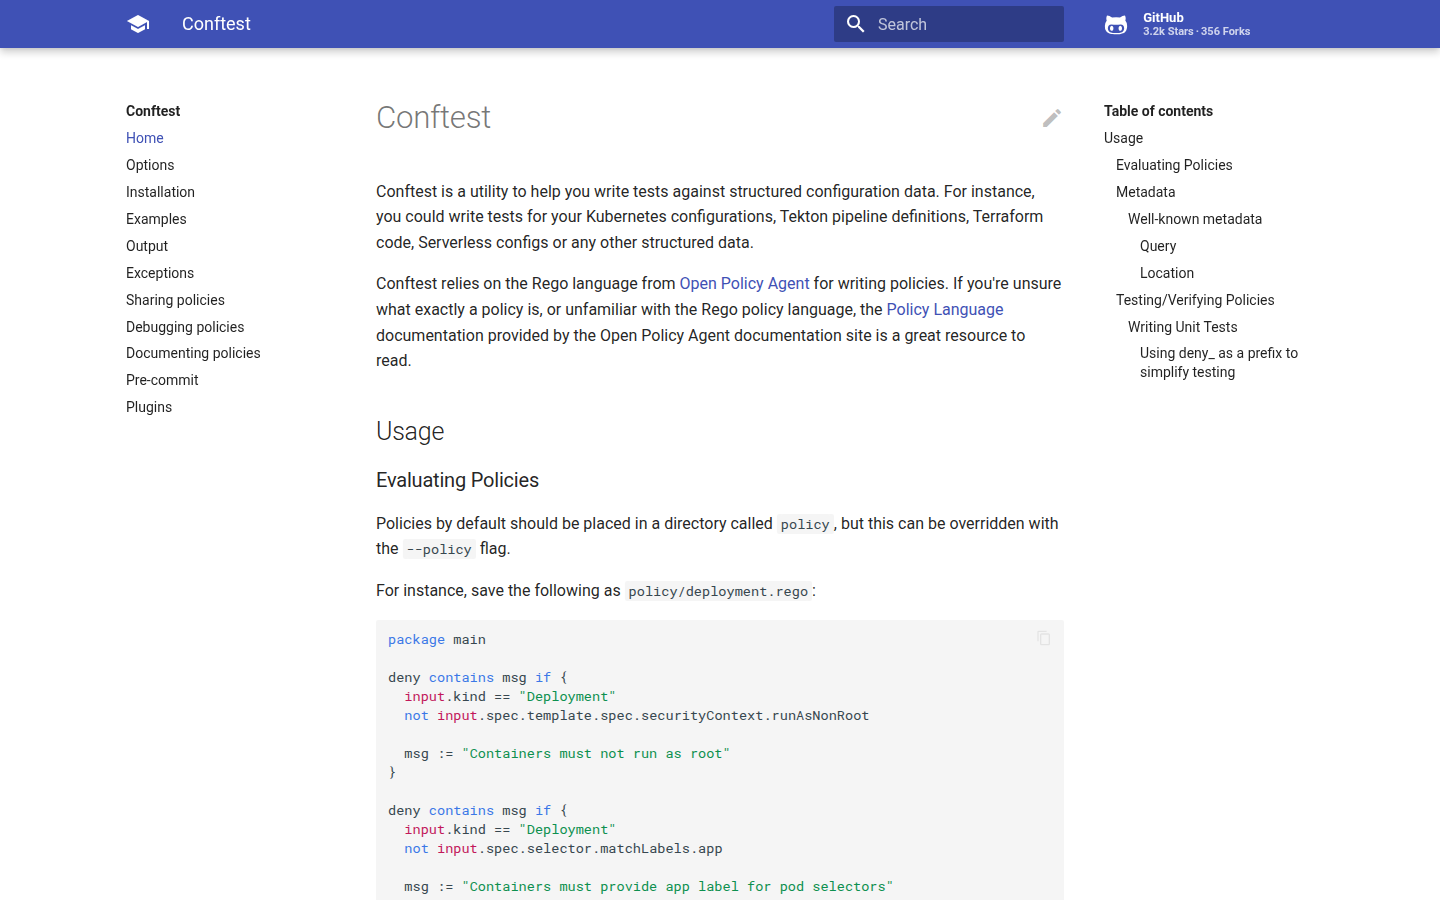
Conftest runs OPA Rego against JSON, YAML, HCL. You write the policy. There is no vendor pack theater unless you add one.
When the rule is yours, a wrapper around Checkov is the wrong door. You write Rego. That is the cost and the point.
Key features
- You write Rego
- Many inputs
- Apache-2.0
- OPA-shaped
Why we like it
A policy you authored is the pick when a pack cannot say your exception.
Limits
You write Rego. That is the cost and the point.
Snyk IaC
Best for commercial IaC next to Snyk OSS
Snyk IaC is the commercial file scan. If Snyk OSS is already on the PR, this is the sibling. Overlap with SCA is the vendor, not the job.
Do not add Checkov and Snyk IaC on the same files without a reason. Commercial. Noise.
Key features
- PR annotations
- Terraform and friends
- Same Snyk tenant
- Free and paid
Why we like it
The desk already on the PR is the commercial IaC job.
Limits
Commercial. Noise.
What we left out
- tfsec. People want the Terraform linter they already pinned in CI. It merged into Trivy, so it failed the still-a-separate-product check.
- Prisma Cloud IaC. Teams want the file scan on the CSPM they already bought. Checkov is the Prisma-stewarded open engine, and Snyk IaC already covers the commercial file scan.
IaC threads treat post-apply CSPM as late. tfsec merged into Trivy. A green plan is not a live-account proof.
Questions before you buy
Ask these before the trial clock starts. Vague answers usually mean a neighboring category.
- Does a fixture open security group in Terraform we own fail CI?
- Is the rule ours, or are we inheriting a pack, and which engine is still a separate product?
- Do we already run Trivy or Snyk on the PR and refuse to enable the IaC job?
Fail the plan. Then read the live account.
FAQs
Does IaC scanning replace CSPM?
No. The file is the intent. The account is the truth. Those are different jobs. Open the matching list for the other one.
Where did tfsec go?
It merged into Trivy. Use Trivy config scan.
Does this replace Kubernetes admission?
No. Admission is the cluster gate. This is the git file. Open Kubernetes security.
Is this a scored bake-off?
No.

