ConductorOne vs Veza: Which One Fits Your Access Request Queue?
Choose ConductorOne when the weekly queue is self-service access requests, RBAC profiles, and just-in-time grants for people and agents (C1 Access). Choose Veza when the weekly queue is an authorization Access Graph that answers who can take what action on apps, data systems, and non-human identities, now on the ServiceNow path.
Buyers often score both as “authorization platforms” and ship one RFP. That assumption fails on Monday. One product clears access requests, auto-approves routine grants, and expires elevated access when the task ends. The other product maps effective permissions across Salesforce objects, Snowflake tables, and service accounts so reviews are not guesswork. Treating those as the same hire leaves either a request backlog with no graph, or a graph with no self-service JIT path.
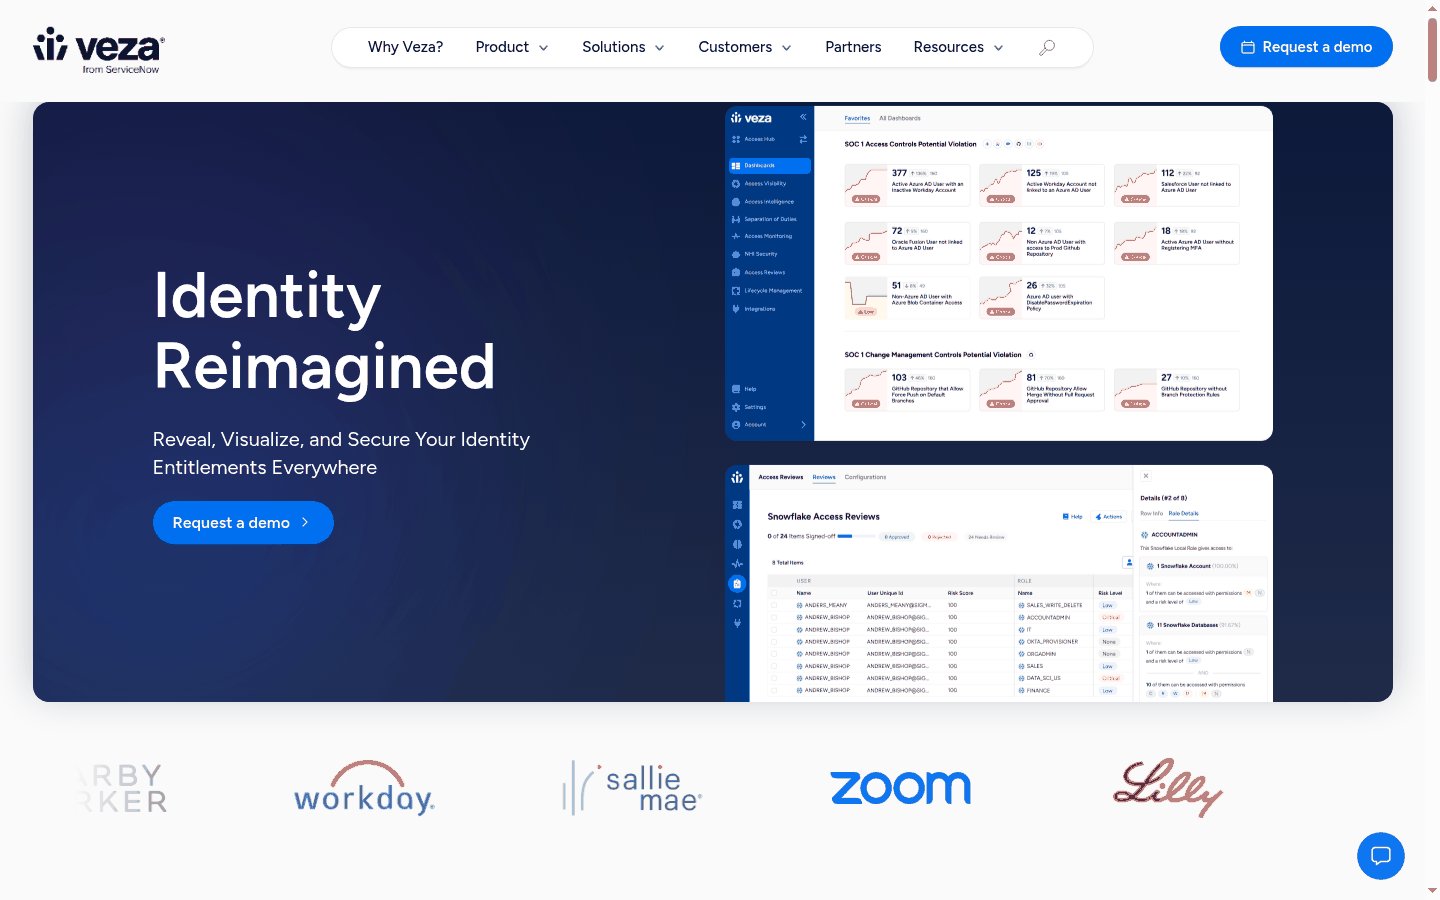
Between these two the centers differ. ConductorOne brands as C1 and productizes C1 Access: policy-driven requests from Slack, Teams, MCP, CLI, or web, plus lifecycle and compliance modules for people and agents, with AI Access Management in early preview after 19 March 2026. Veza productizes an Access Graph for people and non-human identities across apps, data, and cloud, with reviews and AuthZ automation on the ServiceNow path after the 2 March 2026 close. ConductorOne still shows entitlements. Veza still runs reviews. For Veza versus cloud Permissions Firewall see Veza vs Sonrai. NHI shortlists live under non-human identity tools. More pairs under Compare.
| Job | IGA-shaped access desk: self-service requests, RBAC profiles, JIT grants/expiry, lifecycle and reviews for people and agents | Authorization Access Graph for people and NHI across apps, data, SaaS, and cloud; intelligence, reviews, AuthZ automation (ServiceNow path) |
|---|---|---|
| How a bad day closes | Route or auto-approve the request, provision the entitlement, expire JIT when the window ends, keep request-to-revoke evidence | Search effective permissions, explain identity-to-resource paths, drive graph-backed reviews and AuthZ grant/revoke |
| Operator morning unit | Open request tasks, approval queues, JIT expiries, and lifecycle exceptions | Access risks, review campaigns, and provisioning exceptions tied to the Access Graph |
| Deploy | SaaS C1 platform; connectors across SaaS, cloud, infra, MCP; Terraform and APIs for extension | SaaS Access Platform; connectors plus Open Authorization API; ServiceNow integration in phases after Mar 2026 close |
| License/pricing | Demo / sales quote; no public dollar SKU (checked 13 Sep 2026) | Sales / ServiceNow packaging; no public dollar SKU (checked 13 Sep 2026) |
| Who operates it | IT and identity owners closing access requests and JIT without standing privilege piles | Identity, IAM/IGA, and security owners answering effective access across the app and data map |
That is an access-request and grant-scope problem. Between these two, ConductorOne productizes the request and JIT path for people and agents. Veza productizes the graph that proves what those grants actually allow across systems.
We reviewed first-party documentation, pricing pages, product announcements, and live community threads. We did not test the products in paid production environments, so this is not a hands-on benchmark. This page does not include exploit proofs of concept.
ConductorOne
Veza
Editions and pricing
Both are sales-quoted in 2026. Ownership differs: ConductorOne remains independent on c1.ai. Veza closed into ServiceNow on 2 March 2026.
| Owner (2026) | ConductorOne / C1 (independent) | ServiceNow (acquisition completed 2 Mar 2026) |
|---|---|---|
| How you buy it now | Demo and enterprise quote for C1 Access, Lifecycle, Comply, and AI Access Management preview | Sales / ServiceNow security and risk packaging; confirm Access Graph modules on the invoice |
| Public units | No public dollar SKU on c1.ai pages checked 13 Sep 2026 | No public dollar SKU on veza.com pages checked 13 Sep 2026 |
| What the invoice covers | Request catalog, policies, JIT, connectors, reviews/SoD scope, optional AI Access Management preview terms | Access Platform modules: graph visibility, intelligence, reviews, lifecycle, AuthZ, Access AI |
| Self-serve start | Book a demo | Demo / enterprise onboarding |
If procurement needs a published public list-price meter this week, neither pair member publishes one. Price the queue you will operate, not a shared “identity platform” label.
Access requests and just-in-time grants
| Primary surface | C1 Access request catalog with policy auto-approve or routed approval; Slack, Teams, MCP, CLI, web entry points | Access Requests exist on the Veza platform, but the product center is graph visibility and AuthZ automation across systems |
|---|---|---|
| Time-bound elevation | JIT grants with automatic expiry; breakglass with reason and approver retained | Lifecycle and AuthZ change access in connected systems; confirm JIT packaging in the ServiceNow quote |
| Agent and AI tools | AI Access Management preview: agent identities, MCP tool-call authorization, vaulted credentials, self-service AI tool provisioning | NHI and AI-agent nodes on the Access Graph; Access AI for risk analysis; not marketed as an MCP request catalog |
| What teams argue about | Whether connectors cover every app in the request catalog without custom work | Whether graph findings close the Slack request queue without a dedicated IGA request product |
If operators live in approval queues and need grants to expire without another ticket, ConductorOne is the clearer hire between these two.
Authorization graph and effective permissions
| Primary surface | Entitlements and profiles tied to connected apps for requests and reviews; not marketed as a cross-system effective-permissions search product | Access Graph across IdPs, SaaS, data systems, cloud, NHI, and custom apps via Open Authorization API |
|---|---|---|
| Effective access question | Which requestable entitlements and profiles apply to a user or agent under policy | Who can take what action on what data, with path explanation for investigation and reviews |
| Governance follow-through | C1 Comply campaigns, SoD, and evidence from the same policy model as requests | Graph-backed reviews, lifecycle, and AuthZ automation on the ServiceNow path |
| What teams argue about | Whether request evidence alone satisfies auditors who want blast-radius paths across data systems | Whether ServiceNow packaging covers the connectors the IGA team already runs |
That sentence is Veza-shaped morning work. If operators still cannot answer effective access across SaaS and data, an Access Graph hire beats another request catalog alone.
Where they overlap
Both talk least privilege for humans and machines. Both show up when an RFP says IGA or authorization. Overlap is category language, some review workflows, and identity connectors. It is not the same weekly queue: clearing requests and JIT grants versus mapping effective permissions on an Access Graph.
When to use both
Running both can make sense when the jobs stay separate: ConductorOne for the request and JIT desk, Veza for Access Graph reviews and AuthZ across SaaS and data. That is complementary coverage, not two copies of the same IGA.
Skip Veza for this pair if the only funded job is self-service requests and time-bound grants, and effective-permissions analysis is already owned elsewhere. Skip ConductorOne for this pair if the only funded job is graph-backed authorization across apps and NHI on ServiceNow, and the request desk is already owned by another IGA.
Decide the weekly queue first. If the product must run self-service requests and just-in-time grants for people and agents, that is ConductorOne. If the product must answer who can take what action on what data across apps and NHI, that is Veza on the ServiceNow path. Only then open the quotes.
FAQs
Are ConductorOne and Veza the same authorization product?
No. Between these two, ConductorOne (C1 Access) leads with self-service access requests, RBAC profiles, and just-in-time grants for people and agents. Veza leads with an authorization Access Graph for effective permissions across apps, data, and NHI on the ServiceNow path.
Did ConductorOne rebrand to C1?
First-party sites resolve ConductorOne URLs to c1.ai and brand the platform as C1. Product names on this page follow C1 Access, Lifecycle, and Comply as published on c1.ai (checked 13 Sep 2026).
Is Veza still independent?
ServiceNow completed the Veza acquisition on 2 March 2026. Ask which ServiceNow security SKU invoices the Access Graph this quarter.
Does either publish list prices?
Neither published a public dollar SKU on first-party pages checked 13 Sep 2026. Both are demo and sales quoted.
Is this a scored bake-off?
No. Order is editorial.

