Identity
Best PAM Tools for Vault, JIT, and Privileged Access in 2026
Standing admin still works at 3 a.m. PAM is how you stop shipping that privilege permanently.
Machine identities already outnumber humans 109 to 1 in Idira’s 2026 Identity Security Landscape. Standing Domain Admin and always-on cloud AdministratorAccess still look convenient until one compromised laptop owns the estate.
Privileged Access Management vaults credentials, brokers sessions, and increasingly issues just-in-time grants so humans and machines borrow privilege for a task. Some products are classic password safes with session recording. Others are cloud JIT brokers or dynamic secret engines.
If you need secrets for application config, start with secrets management tools. If the job is discovering non-human identities at scale, see NHI tools.
How we evaluated
We read first-party PAM, privileged access, and dynamic-credential product pages, license notes, and pricing CTAs on 17 Sep 2026. We asked whether the product vaults or brokers privileged credentials, whether JIT / zero standing privilege is a named workflow, whether machine access is in scope, and whether an open or infra-native path exists. Marketing pages are claims, not bake-off proof.
| Tool | Best for | What to check |
|---|---|---|
| Idira (CyberArk) | Enterprise vault and session PAM | Commercial · platform rename in flight |
| BeyondTrust | Password safe + privileged remote access | Commercial · modular |
| Delinea | Secret Server vault + elevation | Commercial · AD-heavy ops |
| Britive | Cloud JIT / zero standing privilege | Commercial |
| HashiCorp Vault | Dynamic machine credentials | BSL / Enterprise |
| Teleport | Certificate infra access | Open core · commercial |
Idira Privileged Access (CyberArk)
Best for enterprise vault and session PAM across humans and machines
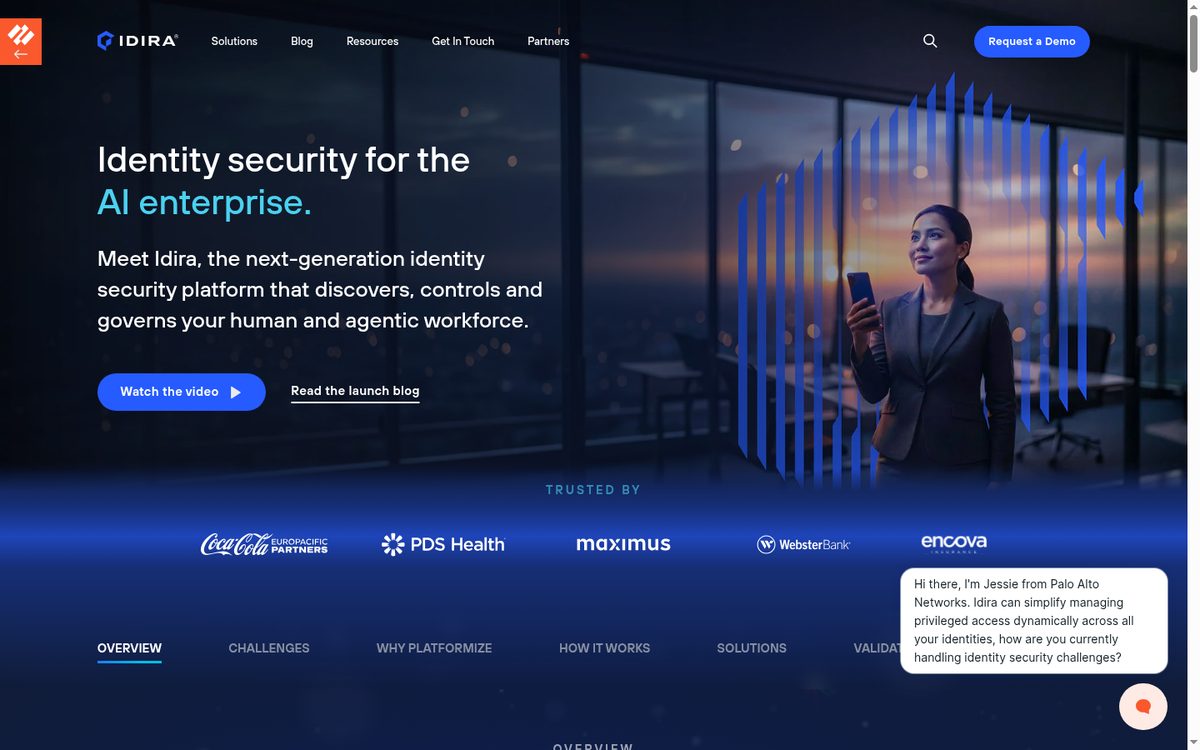
Idira is the CyberArk PAM lineage under Palo Alto Networks branding: credential vaults, session isolation, and privilege controls that now extend toward machine and agentic identities.
On this shortlist it is the enterprise suite seat. It is not a cloud-only JIT broker, and it is not a substitute for a secrets-manager shelf aimed at application config.
Key features:
- Privileged account discovery and vaulting
- Session recording and isolation for admin paths
- Just-in-time and zero standing privilege workflows they document
- Machine and agentic identity controls on the Idira platform story
Why we like it:
When auditors ask who can become Domain Admin and for how long, Idira/CyberArk still sets the reference shape for vault plus session evidence.
Limits:
Commercial, sales-quoted. Platform renaming from CyberArk to Idira is in progress; confirm SKU names on the quote. Depth is a program, not a weekend install.
License or pricing: Commercial. No public list price on 17 Sep 2026.
BeyondTrust
Best for password safe plus privileged remote access in mixed estates
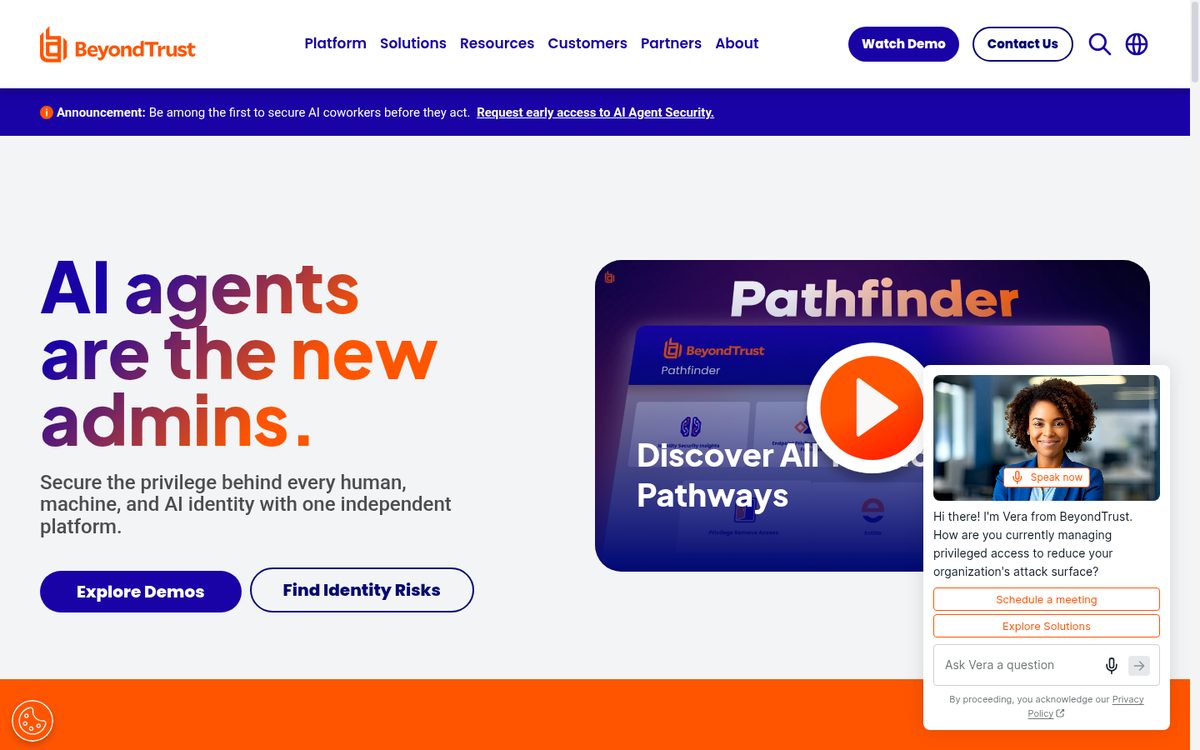
BeyondTrust covers password vaulting, endpoint privilege management, and privileged remote access for vendors and admins who should not keep standing RDP.
It is a strong alternative when the painful queue is shared local admin and third-party remote access, not only Active Directory vault checkout.
Key features:
- Password Safe style vaulting for privileged credentials
- Privileged Remote Access for vendor and admin sessions
- Endpoint privilege management to remove local admin sprawl
- Analytics and threat integrations they document
Why we like it:
Teams that already fight shared Windows admin passwords and contractor VPN jump boxes get a coherent BeyondTrust story without buying a full IdP rewrite.
Limits:
Commercial quote. Module boundaries matter: Password Safe, PRA, and EPM are not one line item everywhere. Confirm which modules land in year one.
License or pricing: Commercial. No public list price on 17 Sep 2026.
Delinea
Best for Secret Server style vaulting with privilege elevation on endpoints
Delinea (Secret Server lineage) is classic PAM vaulting with privilege elevation and DevOps-oriented secret workflows for teams that outgrew spreadsheets and shared admin passwords.
Pick it when the center of gravity is Windows/AD vault operations and endpoint elevation, not only Kubernetes SSH.
Key features:
- Secret Server vault for privileged credentials
- Privilege Manager style elevation without standing local admin
- Cloud and hybrid connector coverage they list
- DevOps and machine credential patterns in their docs
Why we like it:
Secret Server remains a familiar operations model for identity teams that already staff a vault desk and need elevation without handing out permanent admin.
Limits:
Commercial. Confirm cloud vs self-hosted edition and which connectors are in the quote. Not the leanest path if you only need cloud IAM JIT.
License or pricing: Commercial. No public list price on 17 Sep 2026.
Britive
Best for cloud just-in-time privilege and zero standing access
Britive focuses on just-in-time privileged access across cloud and SaaS so humans and workloads borrow permission for a task instead of keeping standing admin roles.
It is the cloud JIT seat on this list. It is not a replacement for an on-prem password vault when Domain Admin still lives in Active Directory.
Key features:
- Just-in-time elevation across cloud IdPs and accounts
- Zero standing privilege workflows for humans and workloads
- Secrets and dynamic permission patterns they document
- Audit trails for temporary grants
Why we like it:
When the blast radius is always-on AWS AdministratorAccess and Okta super-admin, Britive’s JIT framing matches the failure mode better than another shared password vault.
Limits:
Commercial. Confirm which cloud and SaaS targets are in the connector matrix. On-prem AD vault depth is not the product center.
License or pricing: Commercial. No public list price on 17 Sep 2026.
HashiCorp Vault
Best for dynamic machine credentials and SSH OTP style privilege
Vault issues short-lived credentials for databases, cloud, and SSH so machines and humans borrow privilege instead of shipping long-lived secrets in env files.
On the secrets management shortlist Vault is the store. Here the PAM-relevant job is dynamic privileged credentials and access workflows, not SOPS-style file encryption.
Key features:
- Dynamic secrets for databases, cloud, and infrastructure
- SSH secrets engine and OTP style host access
- Fine-grained policies and namespaces
- Audit devices and enterprise replication on paid editions
Why we like it:
Platform teams that already run Vault for application secrets can extend the same control plane to privileged machine access without buying a second vault brand.
Limits:
Open source Vault uses Business Source License terms; Enterprise is commercial. Operating Vault well is staff cost. It is not a turnkey Windows Domain Admin session recorder.
License or pricing: BSL for community editions as HashiCorp documents; Enterprise commercial quote. Checked 17 Sep 2026.
Teleport
Best for open-protocol infra access with certificate-based SSH and Kubernetes
Teleport brokers SSH, Kubernetes, databases, and web apps with short-lived certificates instead of shared bastion keys.
It is the infra access seat. Compare it with the sibling privileged access management page when session brokers are the whole story; here it sits next to vault and JIT options.
Key features:
- Certificate-based SSH and Kubernetes access
- Session recording for infra protocols
- Roles mapped to IdP groups
- Open-source and enterprise editions
Why we like it:
Engineering-led orgs that hate shared bastion keys get a protocol-native access path without pretending Teleport is a CyberArk password vault.
Limits:
License and free-tier caps matter: community discussions note employee and revenue limits on free plans. Enterprise is commercial. Not a full Windows password-safe PAM suite.
License or pricing: Open-source and commercial editions. Confirm current free-tier caps on 17 Sep 2026.
How to choose a PAM tool
Four questions before the quote. Names are the shortlist, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Is the first pain Domain Admin passwords or cloud roles? | Vault/session and cloud JIT fix different standing-privilege shapes. | Idira / BeyondTrust / Delinea for vault; Britive for cloud JIT. | A single slide that claims both without a connector list. |
| Do machines need short-lived credentials? | Env-file secrets are a privilege problem, not only a developer convenience. | Vault dynamic secrets; Britive workload grants; Idira machine identity story. | Human-only vault with no machine path on the roadmap. |
| Do you need recorded sessions for auditors? | Checkout without evidence fails most access reviews. | Idira, BeyondTrust, Teleport session recording as documented. | JIT chatops with no session artifact. |
| Can engineering operate an access proxy? | Staff time is part of the license. | Teleport or Vault if platform owns the control plane. | Expecting Secret Server ops from a two-person SRE team overnight. |
What practitioners argue about PAM
Live threads rarely say “PAM” as a category noun. They argue about standing bastion keys, free-tier caps on access proxies, and whether Vault is a privilege broker or only a secret store.
Hacker News
“Teleport is a good software if you can’t configure your SSH servers with Kerberos… Unfortunately, the Teleport open-source version has been discontinued and the free version doesn’t allow companies above 100 employees or with more than 10 million dollars of revenue per year.”
Ask HN thread, Oct 2024 (linked in the Delinea entry). The dissenting instinct nearby is that Kerberos or native Kubernetes auth can replace a broker if you staff it. License caps change the free-path math.
Idira / CyberArk research
“Machine identities per human in the enterprise hit 109:1 this year, up from 82:1 last year.”
2026 Identity Security Landscape (same Idira research linked in the opener). First-party survey framing: privilege is no longer only the human admin desk.
If the hole is still application secrets in git, read secrets management tools. If you need workforce IdP MFA and recovery, start with identity protection tools.
FAQs
Is PAM the same as secrets management?
No. Secrets management stores and delivers application secrets. PAM vaults and brokers privileged admin access, often with session control and JIT elevation. Vault can sit in both conversations for different jobs.
Is Idira still CyberArk?
Palo Alto Networks acquired CyberArk and markets the identity platform as Idira. Existing CyberArk PAM capabilities continue under that lineage; confirm SKU names on your quote.
Does Teleport replace CyberArk?
Usually no. Teleport is strong for certificate-based infra access. Classic Windows password vault and enterprise session isolation remain a different operations model.
Is this a scored bake-off?
No. Order is editorial.