Apono vs Common Fate: active JIT PAM or wound-down AWS/GCP workflows?
Choose Apono when the queue is runtime JIT privileges for humans, machines, and AI agents on a live commercial path. Treat Common Fate as the AWS/GCP engineer workflow shape that wound down in April 2025.
Pick Apono if platform and security still close cloud privilege requests with standing admin rights that linger after the task. It is the active commercial just-in-time PAM path for humans, machines, and AI agents, and it joined 1Password on 15 June 2026.
Between these two, Common Fate was the AWS and GCP engineer access-workflow product (Cedar policies, Terraform, optional BYOC, on-call grants) that announced a wind-down on 15 April 2025. Its Granted CLI continues as open source under fwd:cloudsec. Apono productizes runtime privilege orchestration that creates short-lived permissions in cloud-native policy language, then revokes them when the work ends.
Match the queue you still fail every week: close JIT cloud privilege on a live vendor path with agent and NHI coverage, or keep a Cedar-shaped AWS/GCP workflow while you plan a replacement because Common Fate is no longer selling.
| Job | Cloud-native JIT / zero standing privilege PAM: runtime permissions for humans, machines, and AI agents across AWS, Azure, GCP, Kubernetes, and databases | Was cloud-native JIT access workflows for AWS and GCP: Cedar policy-as-code, Terraform, IdP sync, on-call grants, optional BYOC (wind-down announced Apr 2025) |
|---|---|---|
| How a bad day closes | Engineer or agent requests scoped access in Slack, CLI, Teams, or Jira; Apono mints short-lived roles in provider-native language; access expires; audit trail keeps request, approval, grant, and revoke | While live: time-bound AWS/GCP access via policy workflows and contextual checks (on-call, department). After wind-down: no new commercial close path; Granted remains for AWS account/role switching under fwd:cloudsec |
| Day-to-day workflow | Pending privilege requests, standing-privilege findings, AI agent privilege boundaries, approval escalations, audit evidence for SOC 2 and peers | Historically: pending AWS/GCP access requests, Cedar/Terraform policy drift, on-call grant queues. Today: migration off Common Fate SaaS and whether Granted still covers CLI needs |
| Deploy | Cloud integrations (85+ named on first-party); request paths in Slack, Teams, Jira, CLI; modules Infrastructure Guard, Privileged Cloud, Agent Privilege Guard | Was SaaS with optional BYOC so automation stayed in customer cloud; AWS and GCP focus; IdP sync (Okta, Entra, Google Workspace) |
| License/pricing | Sales / demo; no public self-serve dollar SKU on apono.io (checked 30 Sep 2026); now part of 1Password | Historical public list on commonfate.io/pricing ($1,980 annual minimum; per-user Access Workflows and Cloud Access tiers). Not a current purchase path after wind-down |
| Who operates it | Security, IAM, and platform/DevOps owning standing-privilege removal and agent access guardrails | Was platform/cloud security owning AWS/GCP engineer access workflows; survivors may keep Granted for CLI only |
We reviewed apono.io product and blog pages, the 1Password acquisition press release, commonfate.io product and winding-down post, historical Common Fate pricing, and live community threads the same day (30 Sep 2026). We did not run either product in a paid tenant, so this is not a hands-on benchmark. Apono is an active commercial product inside 1Password. Common Fate announced its wind-down in April 2025; Granted is OSS under fwd:cloudsec.
Apono
Common Fate
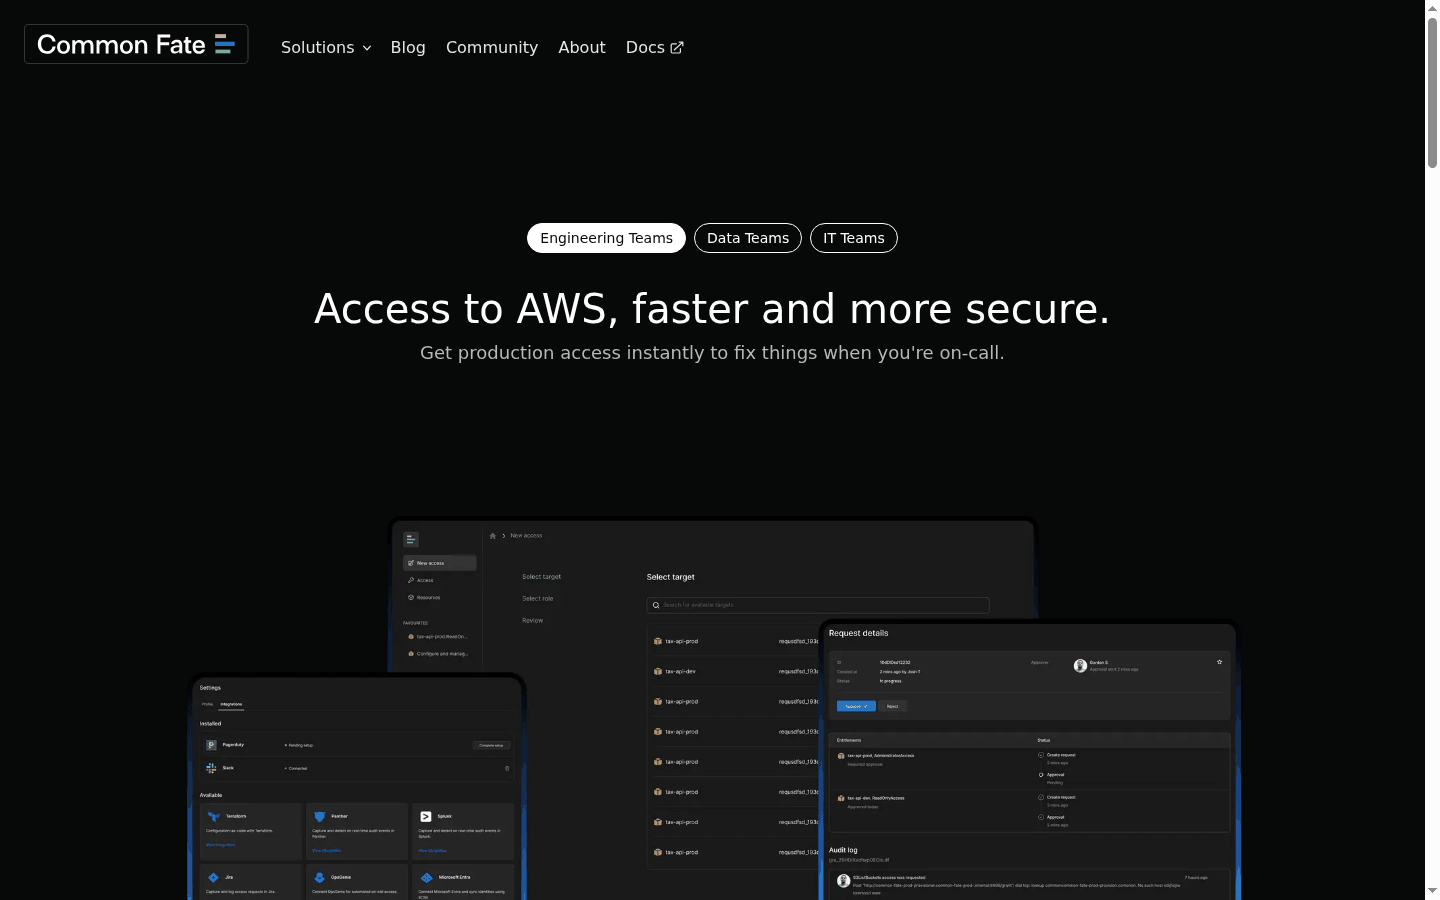
Apono’s recent first-party product signal is Agent Privilege Guard (18 Mar 2026): runtime privilege controls and Intent-Based Access Control for AI agents. Common Fate’s decisive 2025 signal is the wind-down and the Granted donation to fwd:cloudsec, not a new enterprise SKU.
Editions and pricing
Status decides the invoice more than a feature matrix. One vendor is selling JIT PAM under a larger identity company. The other stopped commercial operations and left an OSS CLI.
| Ownership (30 Sep 2026) | Part of 1Password since 15 Jun 2026; first-party says platform and team continue under Unified Access | Wind-down announced 15 Apr 2025; Granted donated to fwd:cloudsec for vendor-neutral governance |
|---|---|---|
| How you buy it now | Book a demo / sales on apono.io; ask whether the quote routes through 1Password for your account | No new commercial rollout path. Existing customers were directed to wind-down communications. Granted remains free OSS |
| Public units | No public dollar table verified on first-party pages (checked 30 Sep 2026) | Historical list only (not a buy path): ~$1,980 annual minimum with per-user Access Workflows / Cloud Access add-ons on the old commonfate.io/pricing page; confirm nothing current remains |
| What the invoice covers | JIT PAM scope across Infrastructure Guard, Privileged Cloud, and Agent Privilege Guard under one policy and audit story | Was Access Workflows, Cloud Access, and optional Network / Data Warehouse / IdP Groups modules. Commercial invoice path ended with wind-down |
If procurement needs a live self-serve meter this week, neither first-party site is a checkout. Budget Apono from a quote. Do not treat Common Fate’s old pricing page as a buy path.
How privilege requests close
| Request surface | Slack, Microsoft Teams, Jira, CLI, Apono Assist; approvals with escalation and justification coaching on first-party launches | Was automated access workflows with contextual checks (on-call status, department) feeding time-bound grants |
|---|---|---|
| Permission shape | Creates IAM roles and policies at request time in AWS, Azure, GCP, Kubernetes, and database native language; revokes when the task ends | Was fine-grained, time-bound AWS and GCP access defined in Cedar and deployed with Terraform |
| Standing privilege stance | Zero standing privilege as default: access exists only for the scoped task | Same least-privilege / time-bound intent while the product was live; wind-down announced April 15, 2025 |
| Audit output | Unified trail of request, approval, grant, revoke, and AI session summaries aimed at SOC 2, HIPAA, GDPR, PCI DSS evidence | Was audit export / SIEM-friendly platform security included on historical plans |
That long-lived credential failure is why both products aimed at short-lived grants. Between these two, only Apono is still the commercial product that closes the Monday request queue for multi-cloud and agent identities.
Policy and identity scope
| Policy model | Dynamic guardrails at request time (who, what, where, risk); runtime privilege orchestration instead of a growing library of standing roles | Was Cedar policy-as-code with Terraform provider and CI/CD deployment of authorization policies |
|---|---|---|
| Human identities | Engineers and operators requesting JIT access through chat and CLI paths they already use | Was engineer-facing AWS/GCP access with IdP group sync and SAML SSO on all historical plans |
| Machines and AI agents | First-party Agent Privilege Guard with Intent-Based Access Control (IBAC): agent declares intent, runtime checks actions, access revokes when the task ends | Human/cloud workflow center while live; not positioned as an agentic IBAC PAM product in first-party materials reviewed |
| Cloud breadth | AWS, Azure, GCP, Kubernetes, databases, plus on-prem/hybrid via Infrastructure Guard | AWS and GCP as the published cloud center; optional BYOC deployment |
Cedar-shaped fine-grained policy was Common Fate’s published center. Apono’s published agent story is runtime IBAC on Agent Privilege Guard, which is the split to probe in a PoC if AI agents are already touching production.
Where they overlap
Both aimed at just-in-time cloud access and standing-privilege removal for cloud-native teams. Both talked time-bound grants, IdP integration, and developer-friendly request paths. Common Fate is not a new purchase in 2026. The remaining split is commercial life and identity breadth: Apono is live multi-cloud JIT PAM with agent coverage under 1Password; Common Fate is a wound-down AWS/GCP workflow product whose lasting artifact is Granted OSS.
Related identity and access compares live under Compare. Broader NHI context sits on non-human identity tools.
Migrating from Common Fate
Common Fate is not selling, so dual-platform is not a 2026 plan. Center the migration on policy intent (Cedar or equivalent), approval paths (who signs Slack/Jira/IdP requests), audit exports for evidence you still need, connector replacement for each cloud and SaaS target, and revocation of standing grants as you cut over. Keep the Granted CLI (under fwd:cloudsec) clearly separate from the former Common Fate SaaS; it is an AWS access CLI, not a drop-in replacement for the access-workflow product. Apono is the active commercial JIT PAM for multi-cloud and agents. If you only need AWS account/role switching, Granted alone may be enough.
Choose Apono when you need active just-in-time privileged access for humans, machines, and AI agents under 1Password. Treat Common Fate as the AWS/GCP engineer access-workflow shape that announced wind-down on April 15, 2025, and retain Granted only if the CLI still earns its place separate from the former SaaS.
FAQs
Is Common Fate still a vendor you can buy?
No for a new enterprise rollout. Common Fate announced it was winding down operations on 15 April 2025 (announcement date; not every customer operation ended that day). Granted was donated to fwd:cloudsec and remains available as open source. Marketing pages may still render; that is not a purchase path.
Was Apono acquired?
Yes. Apono joined 1Password on 15 June 2026. First-party messaging says the Apono platform continues and the team keeps building under 1Password Unified Access. Reconfirm invoice routing on the quote.
Does Apono replace Common Fate for AWS access?
For teams that used Common Fate as a JIT privilege-request platform across AWS (and wanted Azure, GCP, Kubernetes, databases, and agents), Apono is the active commercial category peer between these two. For teams that only needed Granted-style AWS account switching, the OSS CLI under fwd:cloudsec may still be enough without a PAM platform.
What happened to Granted?
Common Fate donated Granted to fwd:cloudsec so the independent cloud security community can keep stewarding the AWS access CLI. It is open source, not a commercial Common Fate SKU.
What public prices should buyers note?
Apono did not post a self-serve dollar SKU on first-party pages checked 30 Sep 2026; budget from a sales quote. Common Fate’s old pricing page is historical only (wind-down announced April 15, 2025) and should not drive a new purchase. Granted remains separate OSS under fwd:cloudsec.