Claroty vs Nozomi Networks: shared passive, active, and on-prem OT detection
Both run passive SPAN monitoring, optional active enrichment, and on-prem paths. Claroty when that mix lands in xDome or CTD with threat detection named on the quote. Nozomi Networks when Guardian on the mirror port, sized to published node and throughput bands, rolls up in Vantage or an on-prem console.
Both Claroty and Nozomi Networks sell OT/ICS network detection that starts on a SPAN or tap, can add active enrichment where the plant allows it, and can stay on premises when packet data must not leave the site. In the 12 months before its 14 April 2026 announcement, Claroty’s Team82 said it verified more than 200 cyber attacks in which attackers reached cyber-physical devices by scanning internet-exposed gear and abusing default credentials and insecure protocols (Claroty, 14 April 2026). An IT EDR agent never decodes that plant traffic. Device-graph inventory of the kind on Armis vs Axonius is a different shortlist.
Shared capabilities land first. Passive monitoring copies industrial traffic without generating plant packets. Active enrichment (Claroty Safe Queries; Nozomi Smart Polling) fills quiet or thin-protocol assets when a query is allowed. On-prem paths cover air-gapped or residency-bound sites: Claroty Continuous Threat Detection (CTD) and Nozomi Guardian with a Central Management Console. Cloud rollups are Claroty xDome and Nozomi Vantage.
The remaining split is protocol depth claims, how each sizes sensors, how long baselines take to tune, where packet metadata goes, and which contract line actually includes threat detection. Claroty Marketplace xDome dollars leave the billing unit undefined, so those rows are not a plant budget. Nozomi’s listed Vantage Bundle T5K meters up to 5,000 assets per 12 months with a defined asset band.
| Primary use case | OT/ICS network detection on Claroty: passive SPAN monitoring, optional Safe Queries / Edge / project-file enrichment, xDome SaaS or on-prem CTD | OT/ICS network detection on Nozomi Networks: Guardian on a mirror or tap, optional Smart Polling, Vantage cloud or on-prem Central Management Console |
|---|---|---|
| How an alert closes | DPI on the span builds asset detail and a communication baseline; anomaly, policy, and known-threat alerts go to xDome or CTD, then to SIEM or ticketing when threat detection is on the contract | Guardian learns a behavior baseline from mirrored traffic, flags anomalous traffic, unusual process values, and unwanted operations, then routes them into playbooks and integrated tools |
| Day-to-day workflow | Plant network keeps the SPAN alive; security tunes baselines and false positives, and decides when Safe Queries, Edge, or project-file parsing may run | Plant network keeps the SPAN or tap alive; security tunes Guardian baselines and false positives, and turns Smart Polling on only where a query is allowed |
| Deploy | xDome SaaS or on-prem CTD. Passive monitoring is built into both. Sensors or collectors sit on mirror ports; Edge can run without extra SPAN hardware | Guardian as hardware, VM, embedded sensor, or container, with published node and throughput bands by model. Air-gapped sites can stop at the on-prem Central Management Console. Vantage is the cloud rollup |
| License/pricing | Sales quote for xDome and CTD. AWS Marketplace lists xDome SaaS contract tiers (checked 3 Oct 2026) but does not define what one unit counts, so those dollars are not used here as a plant budget. Confirm threat detection is named on the quote. Marketplace rows are not a CTD appliance price | Quote by monitored asset count. AWS Marketplace Vantage Bundle T5K: 218,880 USD per 12 months for up to 5,000 assets; sensors not billed separately on that bundle. Hardware and other asset bands are separate lines |
| Who operates it | OT security with a plant network owner for span placement, often feeding an existing SIEM rather than replacing the controls team | Same split: OT security tunes Guardian, plant network owns the tap, and air-gapped sites may never send packet data to Vantage |
We reviewed Claroty’s passive-monitoring page and CTD / xDome packaging, the 14 April 2026 xDome announcement, Nozomi Guardian, Nozomi technical specifications (sensor node and throughput bands), the 28 October 2025 Arc announcement, both AWS Marketplace contract rows, and an August 2026 practitioner comment that names both platforms, all on 3 Oct 2026. We did not run either product in a plant, so this is not a hands-on benchmark. Claroty’s Marketplace page does not define what one unit counts. A current numeric protocol total on Nozomi’s protocol-support download was not found on the public pages opened.
Claroty
Nozomi Networks
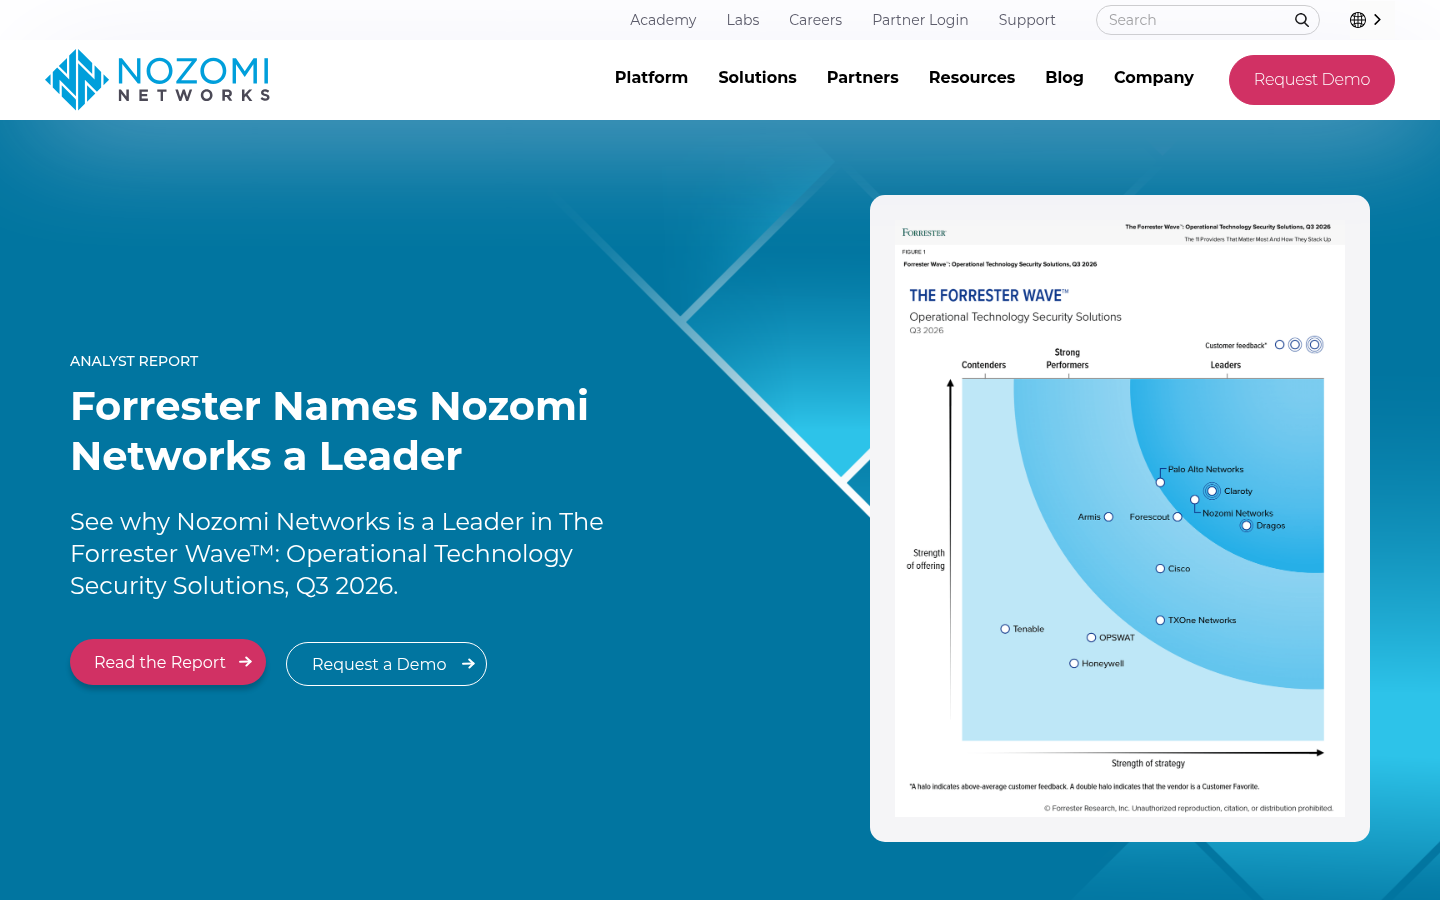
Claroty remains an independent company. Its 22 January 2026 Series F ($150 million led by Golub Growth, with up to $50 million more from existing investors) was growth funding, not a change of owner. Nozomi Networks is a wholly owned subsidiary of Mitsubishi Electric after that acquisition closed on 28 January 2026, and it is still sold as Nozomi Networks.
Editions and pricing
Neither vendor posts a credit-card total for a full plant program. Prefer the meter you can define on the quote over an undefined Marketplace unit.
| How you buy it now | Sales quote for xDome and for on-prem CTD. Marketplace listing is xDome SaaS with a private-offer note | Sales quote for Vantage or an on-prem Central Management Console, metered by assets. Guardian hardware can be purchased or taken as Hardware as a Service |
|---|---|---|
| Public units (3 Oct 2026) | AWS Marketplace lists xDome SaaS contract tiers (Essential through Advanced) with 12-month dollars. The listing never defines whether a unit is an asset, a site, or something else, so those dollars are not treated here as a capacity budget. Confirm modules and CTD hardware on the sales quote instead | AWS Marketplace Vantage Bundle T5K: 218,880 USD per 12 months for up to 5,000 monitored assets. Sensors are not a separate meter on this bundle. Hardware is not included. Other asset bands stay on the quote |
| What the invoice covers | xDome modules (visibility versus named threat detection, and secure access on higher packaging) plus any CTD sensors and Edge / Safe Queries paths scoped on the order form | Vantage license for the asset band, plus Guardian sensors you still deploy. Hardware as a Service still needs a separate Vantage license. Yearly HaaS subscription SKUs require a three-year minimum commitment |
| Main buying consideration | Is threat detection named on the xDome or CTD quote, without treating an undefined Marketplace unit as the plant budget? | Does the 5,000-asset / 12-month T5K band match the controllers and HMIs Guardian will inventory, with hardware and any Vantage IQ add-on still outside that number? |
Passive, active, sizing, and data handling
| Shared passive path | Passive monitoring copies packets from a SPAN, mirror, or monitor port for DPI. Creates no plant traffic. Built into CTD and xDome | Guardian sits on a mirrored port or tap and generates no extra traffic. Passive-only is documented for sites that forbid queries (NERC CIP, nuclear, and defense examples on the Guardian page) |
|---|---|---|
| Shared active path | Safe Queries send targeted active queries when allowed. Claroty Edge and project-file analysis enrich without a full network scan. Claroty’s passive page says quiet or thin-protocol assets (many Modbus devices) will not yield firmware from the span alone | Smart Polling is the active enrichment path when the plant allows it. Remote Collectors and Arc endpoint sensors can feed Guardian. Skip active paths on sites that must stay passive-only |
| Shared on-prem path | On-prem CTD keeps analysis on site. xDome is the SaaS rollup when cloud is allowed | Guardian plus Central Management Console can stay fully on premises / air-gapped. Vantage is the cloud rollup when cloud is allowed |
| Protocol coverage | Claroty states support for 450+ protocols on the passive-monitoring page (checked 3 Oct 2026) | Guardian ships an OT/ICS protocol library updated every 3 to 6 months per Nozomi technical specifications. A current public numeric total was not found on the protocol-support page opened for this compare; confirm the live library on the quote |
| Sensor sizing | CTD and xDome place sensors or collectors on mirror ports; Edge can run without extra SPAN hardware. A public Claroty node and throughput matrix matching Nozomi’s published ladder was not found on claroty.com pages opened for this revise, so size sensors from the sales architecture review rather than inventing a capacity table | Nozomi technical specifications publish Guardian models from rugged / portable bands (hundreds to a few thousand nodes, about 100 to 800 Mbps) through mid enterprise (about 1,000 to 40,000 nodes, up to 1 Gbps) and large enterprise racks (about 100,000 to 500,000 nodes, about 3 to 6 Gbps). Virtual sensors publish up to 40,000 nodes. Values are “up to” and vary with traffic mix |
| Tuning | Baselines learn communication patterns; security tunes anomaly and policy alerts. Practitioner comment below names long false-positive tuning as a shared heavy-platform cost | Guardian learns behavior baselines from mirrored traffic; security tunes anomalies and process-value alerts. Same practitioner comment names protocol-parser updates and long false-positive tuning as operating costs |
| Data handling | CTD keeps packet analysis on premises. xDome is SaaS; confirm residency and what metadata leaves the plant on the order form. Passive monitoring does not alter assets | Air-gapped sites can stop at the Central Management Console and skip Vantage. Vantage is the cloud management path when sites may phone home. Confirm what sensor metadata leaves each plant |
| April 2026 vs October 2025 releases | The 14 April 2026 xDome release adds Visibility Orchestration: a visibility score and prioritized tasks that fill asset gaps via Edge, active queries, and EDR integrations. That is inventory quality on top of the span, not a second anomaly engine | The 28 October 2025 Arc release adds Detection, Quarantine, and Delete modes for malicious files on Windows, Mac, and Linux OT endpoints. It does not replace Guardian on the mirror port |
| Main buying consideration | Will you staff shared passive plus optional active enrichment on xDome or CTD, with sensor size set by Claroty’s architecture review and threat detection named on the quote? | Will you staff Guardian on a published node / throughput model, including passive-only and on-prem console sites that must not phone home? |
Parser updates and a long tuning period are shared operating costs after either platform is on the span. Protocol coverage claims and sensor sizing decide whether the first sites fit. Segmentation and a real mirror port are the entry ticket.
What the alert is for
| Detection content | Anomalies, policy violations, and malicious activity on CPS traffic, plus CVE and misconfiguration context from the asset profile. Early detection is meant to avoid touching the process | Deviations from the learned baseline: anomalous traffic, unusual process values, malware, suspicious communications, unwanted operations. Vulnerability matches sit on the asset record Guardian built from the same traffic |
|---|---|---|
| What you should not automate | Passive monitoring creates no traffic and does not alter assets. Blocking a PLC write is a controls change, not a feature of the span copy. Secure remote access, on the Advanced xDome tier, governs who connects. It is not inline prevention on the process network | Arc can quarantine or delete a malicious file on an endpoint, in a mode the operator chooses. That is not an automatic block of a controller command. Vantage IQ is described on the Marketplace listing as an add-on analytics engine, not as the thing that decides a trip |
| Who gets the ticket | Security investigates in xDome or CTD, then hands context to the SIEM, SOAR, or the controls engineer who owns the setpoint | Security investigates in Vantage or the Central Management Console, then uses playbooks and the same handoff. Process-variable alerts often belong to operations before they belong to a SOC queue |
| Main buying consideration | Do you need threat detection in the contract you will sign, not only an asset list from Essential? | Do you need process-aware anomalies from a passive sensor, with file response limited to Arc on endpoints you are willing to touch? |
Between these two, both will show a conversation map and both will raise anomalies. The difference in the alert path is module boundaries: Claroty names threat detection on higher xDome tiers, and Nozomi names endpoint file actions on Arc while Guardian stays on the copy of the traffic.
Where they overlap
Both are bought when IT detection never learned the industrial protocol and a vulnerability scanner is too blunt to run on the control network. Shared capabilities are real: passive SPAN monitoring, optional active enrichment, on-prem paths, baseline tuning, protocol parsers, and a SIEM export. An RFP that only says “passive OT monitoring” will draw both.
The remaining split is depth and contract. Claroty leads with a 450+ protocol claim and five collection methods, with threat detection named as a module on higher xDome packaging rather than assumed from a visibility tier. Nozomi Networks leads with Guardian models that publish node and throughput bands, passive-only and air-gapped console paths, and a Vantage T5K asset-band price. Claroty Marketplace unit dollars stay undefined as capacity.
Broader cyber-physical asset inventory that is not this span job stays on Armis vs Axonius.
When to use both
Pointing Claroty and Nozomi Networks at the same span doubles baseline tuning and leaves operators unsure which alert is the system of record. The pattern that can work is a site boundary: Guardian passive-only, with the on-prem console, on a plant that cannot query controllers or ship packet data to a vendor cloud; xDome or CTD on commercial sites that will use Edge or Safe Queries. Each site still needs one owner for the alert. If one team would tune both products on one mirror port, pick the packaging you will staff.
Choose Claroty when the shared passive / active / on-prem job lands in xDome or CTD, with a 450+ protocol claim, five collection methods, and threat detection named on the quote rather than assumed from an undefined Marketplace unit. Choose Nozomi Networks when that shared job lands on Guardian models with published node and throughput bands, including passive-only and on-prem console sites, licensed by asset count on Vantage.
FAQs
Is this the same decision as Armis vs Axonius?
No. Armis vs Axonius is cyber-asset inventory and attack-surface context across IT and device classes. Claroty vs Nozomi Networks is passive OT/ICS network detection: span or tap traffic, industrial protocol decoding, and anomaly alerts. Some programs run an inventory platform beside one of these sensors. They are not the same quote.
Do I have to replace the engineering workstations’ EDR?
No. Neither product is an IT EDR agent for the corporate fleet. Nozomi Arc is an endpoint sensor for OT Windows, Mac, and Linux hosts, with optional file quarantine as of the October 2025 release. Claroty can ingest EDR context as one enrichment method. The plant detection job remains the network copy.
What public prices can a buyer check?
Checked 3 Oct 2026. Claroty xDome SaaS appears on AWS Marketplace with Essential through Advanced 12-month contract tiers, but the listing does not define the billing unit, so those dollars are not a plant capacity budget. Confirm modules and CTD hardware on the sales quote. Nozomi Vantage Bundle T5K: 218,880 USD per 12 months for up to 5,000 assets, sensors not metered separately on that bundle. Hardware and other asset bands stay on the quote.
Will passive monitoring inventory every PLC?
No. Passive monitoring only sees assets that speak. Claroty’s passive-monitoring page says quiet assets and thin protocols such as many Modbus devices will not reveal vendor or firmware from traffic alone, which is why it sells other collection methods. Nozomi documents a passive-only Guardian mode and a separate Smart Polling path when a query is allowed. A redundant controller that stays silent until failover can be missing from both inventories.
Can either product automatically stop a bad PLC write?
Do not plan on it. Claroty passive monitoring does not generate traffic or change assets. Nozomi Arc can quarantine or delete a file on an endpoint in a mode you select. A command block on a controller is a process-safety decision and was not a documented behavior of either network sensor in the pages reviewed on 3 Oct 2026.
Is this a hands-on bake-off?
No. The comparison uses first-party product, announcement, and Marketplace pages plus one community comment. We did not install either product.