Best AI-SPM Tools: What CSPM Still Misses
CSPM can inventory the SageMaker endpoint and still miss the model behind it.
A team can have every SageMaker endpoint inventoried and still miss the risky model sitting behind it.
That is the gap AI security posture management is trying to close. Traditional CSPM can tell you whether a cloud service is exposed or misconfigured. It does not necessarily tell you whether a downloaded model contains malicious code, which agents can reach sensitive data, or how many unsanctioned AI tools employees have connected to company systems.
Those risks now live across models, pipelines, agents, and the cloud services around them. That is why AI-SPM has started to emerge as a category of its own. JFrog counted 495 malicious AI models on Hugging Face in its May 2026 supply-chain report. A CSPM check on the endpoint still would not have opened those files.
The six tools on this list approach that problem differently. Wiz extends the cloud security graph into AI infrastructure. Noma and Mindgard focus more heavily on agents and shadow AI. Protect AI, HiddenLayer, and ModelScan go deeper into the model artifacts themselves.
The right choice depends on what your existing cloud security stack still cannot see. Posture-only cloud checks stay on CSPM.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof two products do the same work. We asked whether the product inventories AI services and models, whether it scans a model file before load, whether it is a CNAPP module or a specialist, and whether a finding can leave the product.
| Tool | Best for | What to check |
|---|---|---|
| Wiz | AI-BOM and attack paths on cloud AI services | Commercial · CNAPP AI-SPM · agentless |
| Noma Security | Agent, MCP, and model discovery with blast radius | Commercial · specialist AI-SPM · agents |
| Protect AI | Model-file scanning now inside Prisma AIRS | Commercial · 35+ formats · Palo Alto |
| HiddenLayer | Model supply chain and runtime posture | Commercial · model/runtime · supply chain |
| Mindgard | Attacker-aligned discovery of models and agents | Commercial · recon + posture · lesser-known |
| ModelScan | OSS scan of pickle, H5, and SavedModel | Apache-2.0 · you run it · file scan |
Wiz
Best for AI-BOM and attack paths on cloud AI services
Wiz coined AI-SPM and now ships it inside AI Application Protection. Agentless AI-BOM across SageMaker, Bedrock, Azure OpenAI, Vertex, and self-hosted stacks such as Llama. Attack paths on the same Security Graph as the CNAPP you may already buy.
For AI-SPM, the relevant capabilities are discovery of AI services, exposed inference endpoints, training-data access, and shadow AI. The broader CNAPP write-up is on cloud security platforms.
Key features:
- Agentless discovery of AI services, models, SDKs, and pipelines (AI-BOM)
- Built-in rules for misconfigured OpenAI, Bedrock, and sibling managed services
- Attack-path analysis from an exposed API to training data
- AI Security Dashboard with project RBAC for builders
Why we like it:
If the estate already pays Wiz, this is the module that sees Bedrock next to the bucket. Their academy writing puts 81% of orgs on managed AI services and 25% still blind to which AI services run.
Limits:
Sales-quoted. No public list on wiz.io. A graph of AI services still leaves the pickle unopened. Runtime block wants the sensor they sell as optional.
License or pricing: Commercial. No public list price.
Noma Security
Best for agent, MCP, and model discovery with blast radius
Noma’s AI-SPM page is discovery first: every agent, MCP server, skill, and model across endpoint AI, SaaS agents, and homegrown stacks. They claim teams often find 10 to 100x more agents than they expected.
The useful extra is blast radius. Tools, data access, triggers, and connected agents scored as toxic combinations, then fed into access control and runtime. Framework maps they name: NIST AI RMF, EU AI Act, ISO 42001, OWASP LLM Top 10, MITRE ATLAS.
Key features:
- Continuous discovery across cloud, SaaS, and developer environments
- Agent risk map: connections, permissions, data access
- Supply-chain checks on models, MCP servers, skills, and unpinned packages
- Posture context into a runtime engine they call Open Enforcement
Why we like it:
When Copilot Studio and a homegrown Bedrock agent sit next to a laptop coding assistant, a CNAPP AI-BOM still misses two of those. Noma’s first-party job is that sprawl.
Limits:
Commercial, sales-quoted. No public list price. Red teaming and AI-DR are sibling products. Noma’s relevant work here is discovery of agents, models, and shadow AI, not those adjacent SKUs.
License or pricing: Commercial. No public list price.
Protect AI
Best for model-file scanning now inside Prisma AIRS
Palo Alto completed the Protect AI buy on 22 July 2025. protectai.com now serves Prisma AIRS. For this comparison, Protect AI is most relevant for its model-security capabilities: AI Model Security scans 35+ formats for tampering, malicious scripts, and deserialization attacks. AI Posture Management is the inventory sibling.
Guardian, Radar, Recon, and Layer were the pre-buy names. The live first-party pages talk about scanning Hugging Face and internal repos in place, locally, then wiring the scan into CI and MLOps.
Key features:
- AI Model Security across 35+ file types (PyTorch, ONNX, TensorFlow, GGUF, pickle, safetensors)
- AI Posture Management over training data, agents, and deployed-model access
- Rules in blocking or non-blocking mode, grouped by source (S3, Hugging Face, local)
- CLI and SDK scan path into build pipelines
Why we like it:
If the hole is a third-party weight file, this is the commercial scanner with the format list. The CNAPP next door is Prisma Cloud. That is a different SKU and a different list.
Limits:
You are buying Palo Alto now. No public list price. Red teaming and runtime firewall sit on the same Prisma AIRS brochure. Confirm the model-scan SKU on the quote.
License or pricing: Commercial (Prisma AIRS). No public list price.
HiddenLayer
Best for model supply chain and runtime posture
HiddenLayer’s platform is four modules: AI Discovery, AI Supply Chain Security, AI Attack Simulation, and AI Runtime Security. The relevant work here is the model before it loads and the inference path after it does. They inspect prompts with deterministic classifiers they keep outside the model’s inference path.
They also published the May 2026 Open-OSS/privacy-filter takedown. That is supply-chain work: a trending Hugging Face repo, a loader, an infostealer.
Key features:
- Inventory of models and shadow AI across environments
- Pre-deploy scan of model artifacts, including air-gapped paths on the public docs
- Runtime inspection of prompts and responses without taking weights
- Attack simulation as a sibling module, mapped to MITRE ATLAS
Why we like it:
When the requirement is “scan the file, then watch inference, and do not hand the vendor the weights,” their first-party pages are unusually specific.
Limits:
Commercial, sales-quoted. No public list price. Attack Simulation is red teaming; this list is posture and supply chain. We did not treat the AWS Marketplace placeholder as a real bill.
License or pricing: Commercial. No public list price.
Mindgard
Best for attacker-aligned discovery of models and agents
Mindgard’s platform page lists AI Security Posture Management as asset discovery: models, agents, MCP/A2A servers, connected tools, and shadow AI inside your products. Recon then maps the attack surface the way an adversary would, before the red-team loop runs.
Born from Lancaster University AI security research. They cite 150+ public vulnerability disclosures feeding the knowledge base. CI/CD and Burp Suite are the integrate-here claims.
Key features:
- Discovery of models, agents, MCP/A2A servers, and shadow AI
- Automated recon of instructions, tools, and behaviors
- Risk reports routed into ticketing and engineering workflows
- Runtime detection and hardening as a later stage on the same platform
Why we like it:
Lesser-known, research-led, and the discovery step is a real AI-SPM job. Useful when the gap is “what did we ship” more than “what did SageMaker enable.”
Limits:
Mindgard puts much of its marketing emphasis on autonomous red teaming, which extends beyond the posture-management focus of this article. Commercial. No public list price.
License or pricing: Commercial. No public list price.
ModelScan
Best for an open-source scan of pickle, H5, and SavedModel
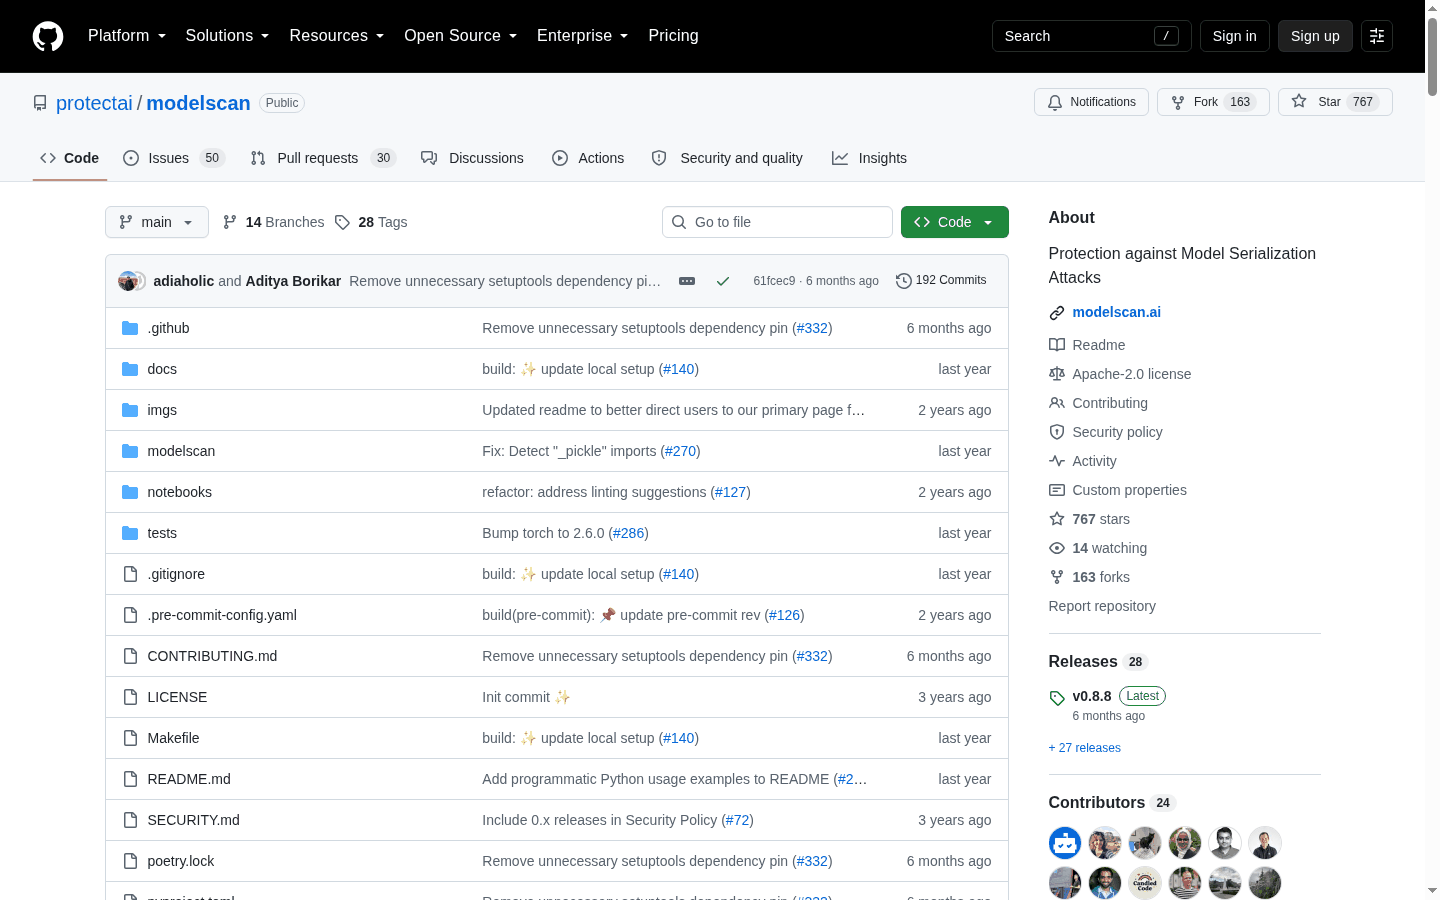
ModelScan is Protect AI’s OSS scanner. pip install modelscan, then point it at a path. It reads the file as bytes and looks for unsafe operators, so a malicious pickle does not execute during the scan. README formats: Pickle, H5, Keras, TensorFlow SavedModel, plus classic ML dumps (sklearn, XGBoost).
The README tells you to scan before load, after train, and before deploy. That is the whole job. Guardian, now Prisma AIRS AI Model Security, is the commercial sibling with the wider format list.
Key features:
- CLI and Python API; JSON or console reports; CI exit codes
- Severity ranks: CRITICAL, HIGH, MEDIUM, LOW
- Apache-2.0. Python 3.9 to 3.12 on the README we read
- GitHub still moving in 2026 (H5 nested-config fixes in June)
Why we like it:
A model file check you can run without a sales call. That is the OSS row this category actually has.
Limits:
Blocklist of unsafe operators, fewer formats than Prisma AIRS AI Model Security. The same March 2026 HN thread argues blocklists miss novel pickle opcodes. It does not inventory Bedrock.
License or pricing: Apache-2.0.
How to choose an AI-SPM tool
Four questions before the quote. Names below are the shortlist, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Do we need the cloud graph on Bedrock, or the pickle in the registry? | CSPM sees the endpoint. AI-SPM has to open the file or the pipeline. | Wiz for managed AI services on a graph you may already pay. ModelScan, Protect AI, HiddenLayer for the file. | A Bedrock CIS check sold as model security. |
| Is this a module on a CNAPP we already pay for, or a specialist? | A fourth platform with no AI-BOM export is a dashboard. | Wiz if the graph is already Wiz. Protect AI if the buy is already Palo Alto. Noma and HiddenLayer if the CNAPP never saw the agent. | Prisma Cloud relabeled as AI-SPM. |
| Can we scan a model file before torch.load, in CI we operate? | Load is code execution for pickle. | ModelScan tonight. Protect AI / Prisma AIRS AI Model Security for 35+ formats. HiddenLayer Supply Chain for air-gapped scans on the public docs. | A runtime chatbot with no pre-deploy scan. |
| Does shadow GPT and the SaaS agent show up, or only managed AI services? | Unsanctioned GPT is a different asset than SageMaker. | Noma and Mindgard for agent and shadow discovery. Wiz for SDKs and managed services on the graph. | An AI-BOM that only lists Bedrock. |
What practitioners argue about AI-SPM
The live argument is not whether SageMaker exists in the account. It is whether loading a third-party model is code execution, and whether a cloud-posture finding would have caught that file.
PyTorch 2.6 flipped torch.load to weights_only=True by default. Teams still hit checkpoints that will not load until they opt back into the old path, which is the same trust decision AI-SPM is supposed to make before the file reaches production.
yashchhabria on Hacker News, Mar 2026, put a number on the file format itself: pickle’s __reduce__ runs arbitrary Python on deserialization, and about 45% of popular Hugging Face models still use pickle. That is the artifact CSPM never opens.
If you already pay Wiz, turn on the AI-SPM module before adding another platform. If the hole is a model file in CI, run ModelScan tonight, then decide whether Prisma AIRS or HiddenLayer is the scanner you keep.
FAQs
Is AI-SPM the same as CSPM?
No. CSPM watches cloud misconfig. AI-SPM has to inventory models, pipelines, and AI services, and often open the model file. Wiz’s own academy page is the split we used. Posture-only cloud checks sit on the CSPM list.
Is Protect AI still an independent company?
No. Palo Alto Networks completed the acquisition on 22 July 2025. protectai.com now serves Prisma AIRS. The relevant products here are AI Model Security and AI Posture Management. Prisma Cloud is a separate CNAPP SKU.
Why is HiddenLayer on an AI-SPM list?
HiddenLayer is on this shortlist for model-file scanning, supply-chain integrity, and runtime posture on prompts. MCP-proxy products are a separate buying decision.
Is this a scored bake-off?
No. Order is editorial.

