Endor Labs vs Socket: Which One Fits Your Dependency Risk Job?
Choose Endor Labs when reachability-driven SCA and upgrade evidence is the product. Choose Socket when malicious-package detection and install-time blocking is the product.
RFPs still drop Endor Labs and Socket onto one SCA or software supply-chain line. That assumption is wrong. A mid-stage committee that scores both names against the same checkbox is mixing two close-out paths.
Between these two, Endor Labs is the reachability-driven SCA and upgrade-evidence product: call graphs, upgrade impact, and Endor Patches. Socket is the malicious-package and install-time blocking product, centered on Socket Firewall. Endor also ships Package Firewall, and Socket also ships reachability, so treat those as adjacent coverage rather than a reason to treat the names as interchangeable.
Related AppSec coverage lives under Application Security. Socket against a unified AppSec platform is covered in Socket vs Aikido. Other two-tool pages sit on Compare.
Overview
| Job | Reachable dependency risk: call graphs, upgrade impact, Endor Patches | Malicious-package detection and Socket Firewall at install |
|---|---|---|
| How a bad day closes | Mark the CVE unreachable, or land an upgrade / Endor Patch with impact evidence | Block or warn before the package reaches a laptop or CI runner |
| Operator morning unit | Reachable findings and upgrade-impact diffs waiting on an owner | Firewall blocks and malware alerts from overnight CI and laptop installs |
| Deploy | SaaS. Developer Free to start; Core and Pro through quote | SaaS plus Firewall wrapper; Enterprise registry, wrapper, or proxy modes |
| License/pricing | Developer Free; Core/Pro quote per contributing developer (90-day commits); AWS Marketplace EL-OSS-PRO 10-pack $12,960 (checked 9 Sep 2026) | Free $0/dev/mo; Team $25/dev/mo (min 5); Business $50/dev/mo (min 20); Enterprise custom (checked 9 Sep 2026) |
| Who operates it | AppSec and engineering owning reachable dependency risk and upgrades | AppSec and platform engineering owning install-time malware policy |
Shared SCA language on a scorecard does not mean the same ticket closes. One queue is a reachable CVE with an upgrade path. The other is a package that should never unpack.
We reviewed first-party documentation, public pricing, marketplace listings, and live community threads. We did not test the products in paid production environments, so this is not a hands-on benchmark.
Endor Labs
Socket
Editions and pricing
Both publish a free starting line. Endor Labs quotes Core and Pro per contributing developer, counted on commits in the last 90 days, and lists an AWS Marketplace EL-OSS-PRO 10-pack at $12,960 (checked 9 Sep 2026). Socket lists Free at $0 per developer per month, Team at $25 (minimum 5 developers), Business at $50 (minimum 20), and Enterprise as custom (checked 9 Sep 2026). On 20 May 2026 Socket announced a $60M Series C at a $1B valuation. Funding is a durability signal, not proof the products close the same ticket.
| Public free line | Developer Free | Free, $0 per developer per month |
|---|---|---|
| Paid path | Core and Pro are quote, billed per contributing developer (90-day commits) | Self-serve Team and Business; Enterprise custom |
| Published unit (checked 9 Sep 2026) | AWS Marketplace EL-OSS-PRO 10-pack $12,960. No public per-developer list price on Core/Pro | Team $25/dev/mo (min 5); Business $50/dev/mo (min 20) |
| What procurement can start without a call | Developer Free. Core/Pro and marketplace packs still route to quote or listing checkout | Free, Team, and Business on the pricing page; Enterprise still routes to custom |
If procurement only wants a published monthly number, Socket can start that way. Endor Labs still needs a quote for Core or Pro, aside from the listed marketplace pack.
Reachability SCA and upgrade remediation
| Primary surface | Call-graph reachability, upgrade impact, Endor Patches | Reachability sits beside malware work, not as the commercial center between these two |
|---|---|---|
| How a finding gets quieter | Unreachable functions drop out of the morning queue | Reachability can cut CVE noise; malware signals stay first-class |
| How a fix is argued | Upgrade impact plus upgrade remediation evidence for developers | Certified Patches and dependency risk sit next to Firewall, as adjacent coverage |
| What teams argue about | Whether call-graph evidence is enough to stop a zero-CVE image policy | Whether CVE triage depth is required when install blocking is the urgent ticket |
Between these two, do not buy a shared reachability checkbox. Buy the operating surface: Endor Labs when upgrade evidence has to survive a developer challenge; Socket when that graph is supporting cast.
Malicious packages and install-time blocking
| Primary surface | Package Firewall is adjacent coverage between these two, not the product you came here to score | Behavioral malicious-package analysis plus Socket Firewall at install |
|---|---|---|
| Install-time shape | Block unapproved or malicious packages when that module is on; it is not the morning unit in this pairing | Firewall blocks known malware and warns on suspected threats before packages land in laptop or CI |
| What first-party writing emphasizes | Upgrade confidence and reachable risk, with firewall as a companion SKU | Socket Firewall Enterprise (24 Oct 2025): policies and modes around the install path |
| What teams argue about | Whether an adjacent firewall SKU covers the next registry incident | Whether Firewall in every install path is operationally realistic |
Between these two, do not buy a shared malware checkbox. Buy the operating surface: Socket when install-time blocking has to be the first control; Endor Labs when that control is a companion to upgrade work.
Where they overlap
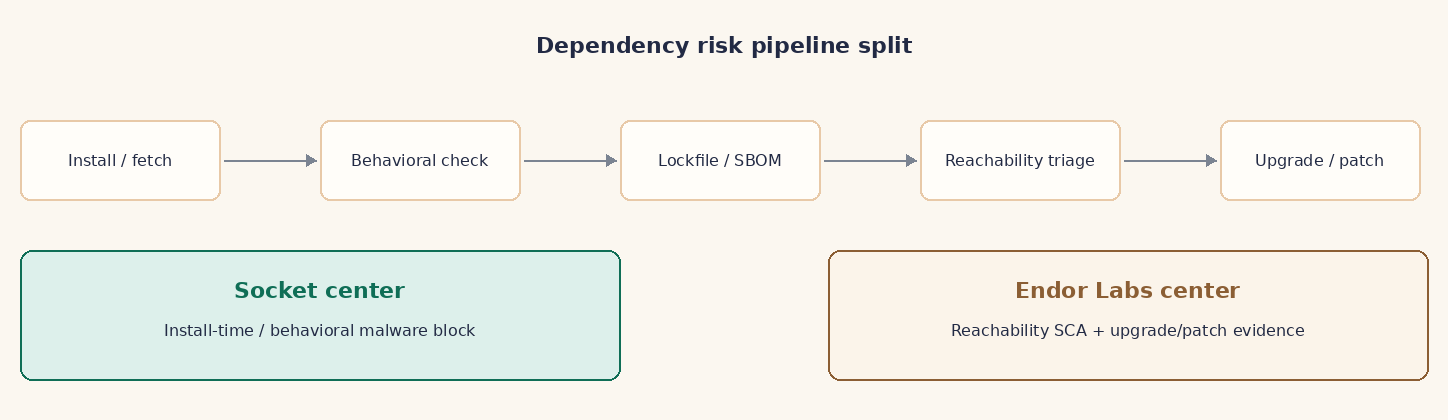
Both talk dependencies, CVEs, and malware. Both sell developer-facing workflows and CI gates. Both ship the other’s adjacent module: Endor Labs has Package Firewall, Socket has reachability. Overlap is category timing and shared vocabulary, not identical close-out. Treating them as interchangeable duplicates spend without covering both jobs.
When to use both
Running both can work when the tickets stay separate: Endor Labs on reachable CVEs and upgrade evidence, Socket on install-time malware policy. Keep ownership clear so two firewalls and two reachability views do not fight the same pull request.
Skip Socket for this pair if the urgent work is upgrade evidence on reachable CVEs and install malware already has an owner. Skip Endor Labs for this pair if the urgent work is blocking malicious packages at install and CVE triage already has an owner.
Decide the job first. If the product must prove which CVEs matter and how an upgrade lands, that is Endor Labs. If the product must stop malicious packages at install, that is Socket. Only then open the pricing pages.
FAQs
Are Endor Labs and Socket the same SCA product?
No. RFPs often file both under SCA or supply chain. Between these two, Endor Labs leads with call-graph triage and upgrade evidence, and Socket leads with install-time malware blocking.
Do either publish list prices?
Socket lists Free $0, Team $25, and Business $50 per developer per month, plus Enterprise custom. Endor Labs publishes Developer Free and an AWS Marketplace EL-OSS-PRO 10-pack at $12,960; Core and Pro are quote per contributing developer (90-day commits). Both checked 9 Sep 2026.
Does Endor Labs include a package firewall?
Yes, as adjacent coverage. Between these two that module is not why you shortlist Endor Labs. Score it if install blocking is already owned and you still want a companion control.
Does Socket include reachability?
Yes, as adjacent coverage. Between these two that graph is not why you shortlist Socket. Score it if malware blocking is the first control and CVE noise reduction is extra.
Should we run both?
Only if the tickets stay separate and someone owns each queue. Two firewalls and two reachability views on the same pull request is a staffing problem, not a feature.

