Legit Security vs Cycode: Which Fits ASPM Plus Pipeline Security?
Choose Legit when AI-native ASPM with VibeGuard at code creation and software-factory visibility is the product. Choose Cycode when Context Intelligence Graph plus Maestro orchestration across AST, SSCS, and ASPM is the product.
AI assistants now write the pull request before AppSec has finished last week’s CVE queue. The painful weekly job is still the same: know what ships, fail the merge that should fail, and push a fix that developers will actually take.
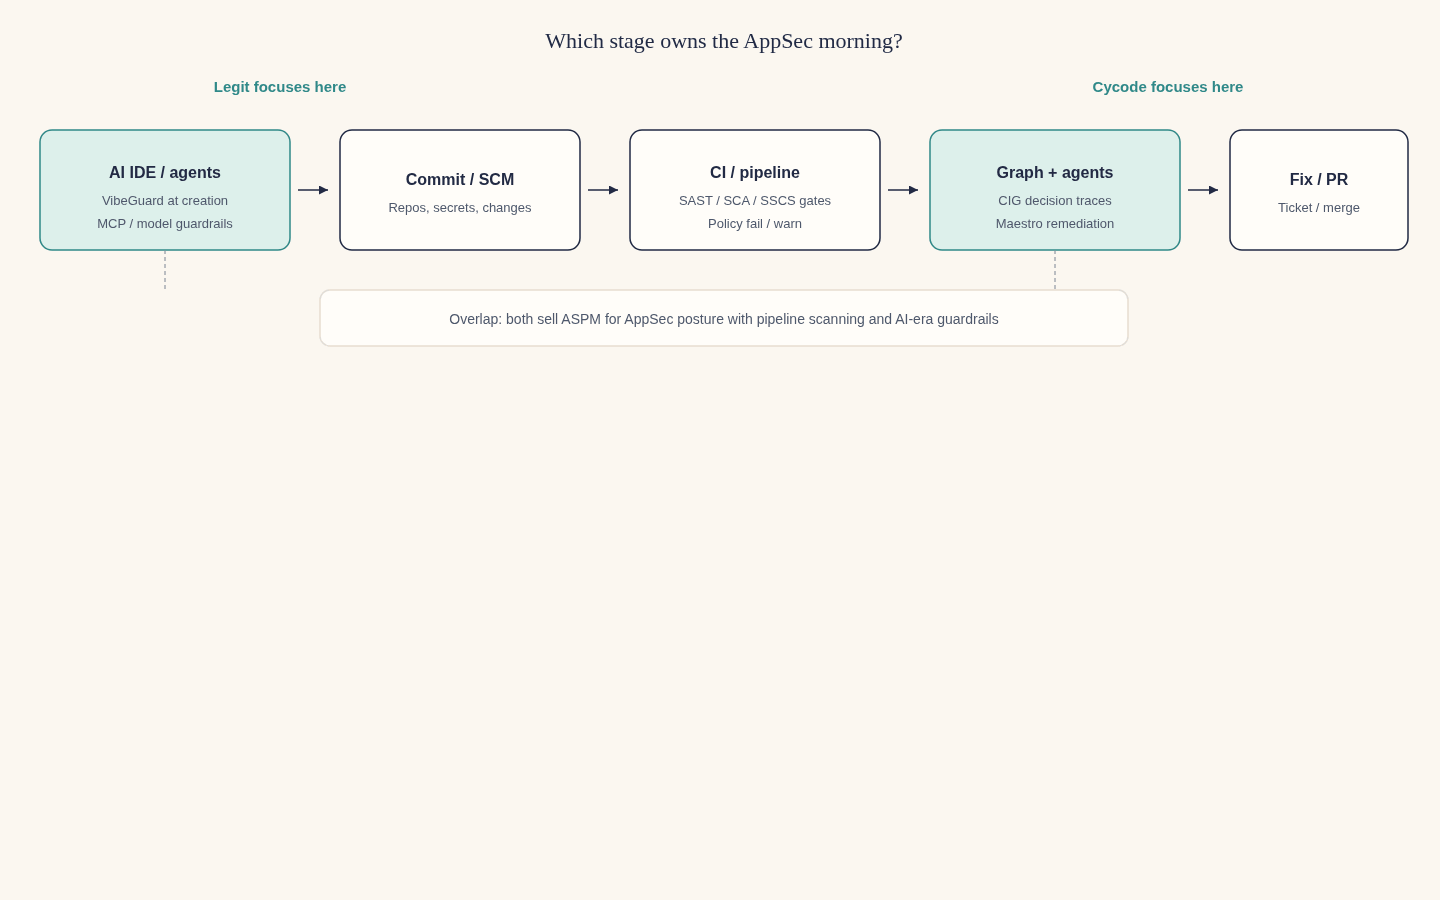
Walk the stages. At the AI IDE, someone needs guardrails on generated code, models, and MCP tools before commit. After commit, scanners and policies have to catch secrets, SAST/SCA findings, and pipeline misconfig. After triage, someone has to own a prioritized posture view and open a fix. That is the ASPM plus pipeline-security buy.
Between these two, Legit productizes AI-native ASPM that starts at the developer endpoint with VibeGuard and extends across software-factory discovery, AST consolidation, secrets, and SSCS. Cycode productizes an Agentic Development Security Platform that converges AST, SSCS, and ASPM on the Context Intelligence Graph with Maestro agent orchestration. Related ASPM shortlists live under ASPM tools. A different ASPM pair is Ox Security vs Cycode.
| Job | AI-native ASPM with VibeGuard at AI IDE creation, plus software-factory discovery and AST/secrets/SSCS consolidation | Agentic Development Security Platform converging AST, SSCS, and ASPM on the Context Intelligence Graph plus Maestro |
|---|---|---|
| How risk is scored | Legit Score with application and business context; AI-assisted prioritization and noise reduction | Context Intelligence Graph decision traces; Exploitability Agent before Maestro triage and remediation |
| Deploy | Connect SCM, CI, and AppSec tools; VibeGuard in AI IDEs; SaaS, private cloud, and on-prem options listed on demo surfaces | SaaS platform with native engines plus connectors; ADLC guardrails for AI coding tools |
| What fails CI | Pipeline and policy gates across AST, secrets, SSCS, and material-change controls | Code Security and Software Supply Chain Security plan gates, including CI/CD security modules |
| License/pricing | Sales-quoted via Book Demo / Schedule a Demo; no public dollar SKU on a first-party pricing table (checked 11 Sep 2026) | Sales-quoted Get Pricing; meters by active developer count and AI usage across modular plans (checked 11 Sep 2026) |
| Who operates it | AppSec owns factory posture; developers meet VibeGuard in the IDE; security owns discovery and Legit Score | AppSec owns the graph and Maestro scope; developers see guardrails and PR-ready fixes |
Recent launches keep those centers visible. On 12 November 2025 Legit launched VibeGuard for securing AI-generated code at the moment of creation and governing coding agents. On 23 March 2026 Cycode unveiled its Agentic Development Security Platform with Maestro orchestration, AI governance, and guardrails. One still leads with creation-time ASPM. The other still leads with CIG plus agent orchestration.
That argument is why creation-time scanning and ASPM consolidation both show up on the same shortlist. It does not mean Legit and Cycode share one product story.
We reviewed first-party documentation, public pricing pages, release notes, and live community threads. We did not test the products in paid production environments, so this is not a hands-on benchmark.
Legit Security
Cycode
Editions and pricing
Neither vendor publishes a self-serve dollar table a spreadsheet can trust without sales. Packaging still differs: Legit sells through demo-led ASPM and VibeGuard packaging; Cycode sells modular plan lines plus separate Cycode AI usage.
| Public price table | No public dollar SKU; Book Demo / Schedule a Demo (checked 11 Sep 2026; /pricing returned 404) | Get Pricing on cycode.com/pricing (checked 11 Sep 2026). No public dollar amounts |
|---|---|---|
| Named lines | Legit ASPM platform capabilities plus VibeGuard for AI IDE / agent governance; native or bring-your-tools AST and secrets | ADLC Security, Code Security, Software Supply Chain Security, Posture Management, Cycode Complete, plus Cycode AI |
| What the quote usually meters | Enterprise scope set in sales (developers, coverage, deployment options). Confirm counting rules on the call | Active developer count and AI usage across the selected plan bundle |
| Free forever SKU | None as a forever-free ASPM SKU on the public site surfaces we checked | None listed as a forever-free SKU on the pricing page |
If procurement needs a published monthly developer price before a call, both vendors will stall that spreadsheet. Ask for developer counting rules, AI-usage true-ups, and which modules or plan lines sit in the same quote.
What fails CI
| Primary gate | Policy and pipeline controls across AST, secrets, SSCS, and material-change signals | Code Security and SSCS policy gates wired into the pipeline you already run |
|---|---|---|
| Scanner surface | Native or connected SAST, SCA, secrets, pipeline/SSCS, and broader AppSec tool results consolidated in ASPM | SAST, SCA, container, IaC on Code Security; CI/CD security, secrets, SBOM on SSCS |
| AI-era control point | VibeGuard blocks issues in the AI IDE before commit and governs models, MCPs, and coding agents | ADLC Security adds AI visibility, governance, and guardrails at the agentic development surface |
| What teams argue about | Which policies block merges vs stay advisory until Legit Score context is trusted | Which plan line owns the fail and how AI-usage metering changes with auto-remediation |
Between these two, do not buy “blocks CI” as a unique checkbox. Both can fail a pipeline when policies say so. Buy the control point your developers will actually feel: Legit VibeGuard before commit plus ASPM gates, or Cycode ADLC guardrails plus Code/SSCS gates.
What each tool produces
| Primary artifact | Deduplicated AppSec posture with software-factory inventory, material-change alerts, and Legit Score context | Context Intelligence Graph records with decision traces across code, build, and runtime signals |
|---|---|---|
| AI-code evidence | VibeGuard visibility into AI assistants, models, MCPs, and pre-commit blocks at the developer endpoint | ADLC visibility and guardrails over prompts, agents, and AI-specific risk categories |
| Remediation shape | AI-assisted remediation guidance, tickets with context, and workflow orchestration into developer tools | Maestro-orchestrated Remediation Agent with PR-ready fixes and an audit trail |
| Operator daily view | Prioritized issues, factory discovery, secrets and SSCS posture, compliance evidence | Graph queries, agent runs, and plan-scoped dashboards (including Posture Management connectors) |
That is why Cycode lands next to enterprise scanner consolidation on ASPM shortlists. Scale across repos is not the same product as VibeGuard at the AI IDE, even when both vendors talk agentic AppSec.
Where they overlap
Both sell ASPM for AppSec teams tired of disconnected SAST, SCA, secrets, and pipeline scanners. Both prioritize contextual, business-relevant risk over raw CVE volume. Both ship AI-era controls for coding agents and both offer sales-quoted enterprise packaging. If your RFP only says “ASPM with pipeline security and AI remediation,” both will tick the box.
When to use both
Running both is rare and usually wasteful. One ASPM graph or factory map is enough for most AppSec programs. Keep a second only during a time-boxed bake-off, or when a regulated program forces parallel validation you cannot fold into one tenant.
Skip Cycode for this pair if the buying committee already standardized on Legit ASPM plus VibeGuard at the IDE, and Maestro-style multi-agent orchestration is not a requirement. Skip Legit for this pair if the team wants Context Intelligence Graph decision traces and Maestro as the default remediation conductor, and is willing to live in Cycode’s plan-line packaging.
Decide the morning queue first. If the product must be AI-native ASPM with VibeGuard at code creation, that is Legit. If the product must be Context Intelligence Graph plus Maestro orchestration, that is Cycode. Only then open the sales quotes.
FAQs
Are Legit Security and Cycode the same ASPM?
No. Both are ASPM platforms for AppSec posture and pipeline security, but between these two Legit leads with VibeGuard at creation plus software-factory ASPM, and Cycode leads with the Context Intelligence Graph and Maestro agent orchestration.
Do I need agentic remediation on day one?
Often no. Start with the posture view and CI gates you trust. Add VibeGuard-scale IDE enforcement or Maestro-driven auto-fix when evidence quality and ownership rules are clear.
Is there a public list price?
Not a trustworthy self-serve dollar table on either first-party pricing surface we checked on 11 Sep 2026. Expect sales-quoted contracts, with Cycode explicitly metering developers and AI usage.
Is this a scored bake-off?
No. Order is editorial.

