Semgrep vs Checkmarx: Which AppSec Queue Fits Your Week?
Choose Semgrep when developer-owned rules-as-code SAST and PR policy are the product. Choose Checkmarx when an enterprise Checkmarx One AppSec platform for RFP-scale SAST is the product.
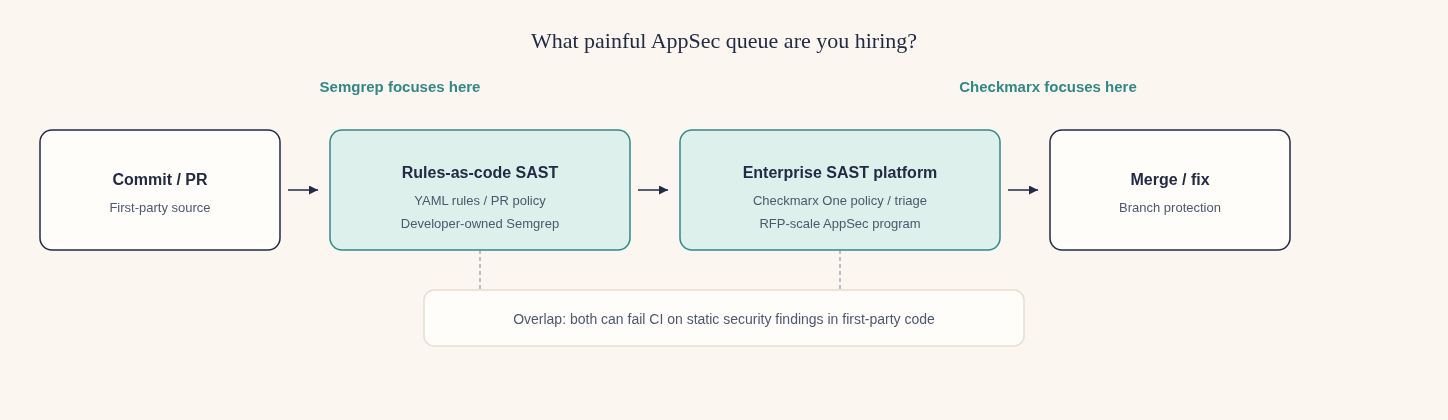
Monday’s merge queue still owns the week. Either a PR fails on a Semgrep rule your team wrote and committed, or AppSec clears a Checkmarx One finding backlog before the release train moves. Both paths can block the same merge. They do not hire the same operators.
Between these two, Semgrep productizes developer-owned rules-as-code SAST and PR-native policy: YAML in the registry or your repo, modular Semgrep Code / Supply Chain / Secrets, plus Guardian for agent-written code. Checkmarx productizes Checkmarx One as an enterprise AppSec platform with SAST as the required core scanner, plus quote-built modules (SCA, secrets, IaC, API, container, DAST, AI supply chain), Risk Orchestration, and Assist agents for triage and remediation. CxSAST remains the on-prem legacy SAST line. Related splits: rules-as-code versus a quality gate is Semgrep vs SonarQube; a unified mid-market AppSec platform versus Semgrep is Aikido vs Semgrep. Broader shortlists live under Application Security.
| Job | Rules-as-code SAST (+ modular Supply Chain / Secrets / Guardian) | Checkmarx One enterprise AppSec platform (SAST core + modules / ASPM) |
|---|---|---|
| How a bad day closes | Rule match becomes a PR annotation or CI fail; Assistant triage/fix; Guardian can catch agent-written issues at write-time | Checkmarx One scan results move through triage, project policy, and Risk Orchestration; Assist agents help prioritize and remediate when licensed |
| CI fail | CLI / PR checks on Code (and sibling products) when policy is configured; custom rules can exit non-zero | CI/CD plugins and Checkmarx One project policies on SAST (and other licensed scanners) |
| Deploy | CLI/CI local or managed; Teams cloud; Enterprise on-prem SCM / custom CI | Checkmarx One cloud platform; CxSAST on-prem for the legacy SAST line |
| Operator morning unit | Rule packs, PR annotations, ignored rules, policy exceptions | Project scan backlog, triage predicates, policy violations, portfolio Risk Orchestration |
| License/pricing | Free to 10 contributors; Teams from $30/contrib/mo (Code / Supply Chain / Secrets modular); Enterprise custom (checked 9 Sep 2026) | Checkmarx One custom quote (developers / apps / usage); Fusion credits add-on; CxSAST separate on-prem (checked 9 Sep 2026) |
| Who operates it | AppSec / platform eng who write and own rules and PR policy | Enterprise AppSec / program owners (often with procurement); developers via IDE and PR integrations |
Recent first-party moves keep the centers visible. Semgrep shipped Guardian on 23 June 2026 so AI agents get scanned at write-time, not only at PR time. Checkmarx published Checkmarx Fusion (Early Access for SAST inside Checkmarx One, blog dated 5 August 2026) as a multi-model add-on on top of Next-Gen SAST, still inside the enterprise platform rather than a developer YAML rules product.
We reviewed first-party docs, public pricing pages, and live community threads. We did not sit in paid production tenants, so this is not a hands-on benchmark.
Semgrep
Checkmarx
Editions and pricing
Semgrep publishes a contributor-metered ladder. Free Edition covers Code and Supply Chain for up to 10 contributors and 10 private repos. Teams starts at $30 per contributor per month with modular Code, Supply Chain, and Secrets. Enterprise is custom for on-prem SCM, custom CI, and unlimited contributors.
Checkmarx One does not publish a self-serve monthly rate card. The pricing builder quotes custom bundles from SAST (required) plus add-on scanners and agentic Assist modules, metered on developers, apps, and usage. Legal license text (Version 2026.03) defines Contributing Developer as a 90-day committer on scanned private repos. Fusion is a usage-based credits add-on. CxSAST stays a separate on-prem SKU without Checkmarx One’s hybrid Next-Gen SAST and Fusion layers. Essentials, Professional, and Enterprise edition names appear in first-party packaging announcements; expect a sales conversation for any of them.
| Public list lines | Free $0 (10 contributors); Teams from $30/contrib/mo modular; Enterprise custom | No public monthly list; Checkmarx One custom quote; Fusion credits; CxSAST on-prem quote |
|---|---|---|
| What the quote usually meters | Contributors (90-day commits on scanned private repos), chosen products, AI credits | Contributing developers, apps, usage, licensed scanners / Assist modules, Fusion credits |
| Self-serve start | Free Edition and Teams checkout on pricing page | Demo / quote path; no self-serve Teams-style checkout on the public pricing builder |
If procurement needs a published monthly rate before a call, Semgrep Teams ($30/contrib) fills a spreadsheet. Checkmarx One packaging is sales-led from the first serious RFP.
What fails CI
| Primary fail signal | CLI / CI job non-zero on matching rules; PR checks when SCM protection is on | Checkmarx One CI/CD plugins and project policies fail builds on configured SAST (and sibling scanner) thresholds |
|---|---|---|
| What the gate usually includes | Security (and optional SCA/secrets) rule policies you own | Enterprise SAST query results plus other licensed scanners under shared policy and triage state |
| Operator morning unit | Which rules fire on this PR, nosemgrep / ignore board, policy exceptions | Which projects failed policy, which findings need triage predicates, release-train blockers |
| Buy the queue | Own and tune what security findings block merge | Own an enterprise AppSec program gate across apps and scanners |
That is the Semgrep CI shape: a rule you can commit and a non-zero exit when it matches. Checkmarx One can be just as strict in pipeline plugins, but the painful unit is usually the program policy and triage backlog across projects, not a YAML file living next to the PR.
What each tool produces
| Finding shape | Rule match with pattern / taint evidence on code (plus SCA/secrets modules when bought) | Checkmarx One SAST results (Next-Gen hybrid engine; Fusion when licensed) correlated in Risk Orchestration with other scanners |
|---|---|---|
| How rules are owned | Public registry, private org rules, YAML in-repo; AppSec authors policies as code | Enterprise queries / policies owned by the AppSec program; developers consume IDE and PR guidance more than authoring YAML packs |
| IDE / agent loop | IDE plugins; Guardian for AI coding agents at write-time | IDE integrations; Developer / Triage / Remediation Assist; MCP packaging on Checkmarx One paths |
| Not the center here | RFP multi-scanner AppSec platform with sales-led portfolio packaging | Commit-your-own YAML rules-as-code as the primary product between these two |
That offline YAML ownership is the Semgrep job between these two. Checkmarx One still wins when the painful unit is an enterprise SAST program with portfolio triage, compliance reporting, and RFP-shaped packaging, not when AppSec needs to ship a custom rule as a PRable artifact.
Where they overlap
Both scan first-party source, decorate pull requests, and can fail CI on security findings. Both ship IDE feedback and market AI-assisted triage or fixes. An RFP that only says “SAST in CI” will shortlist both. Semgrep is not a multi-scanner enterprise AppSec suite with sales-led portfolio packaging, and Checkmarx One is not Semgrep-style rules-as-code ownership as the primary product, so overlap is real and still incomplete.
When to use both
Use both only if you deliberately want developer-owned rules-as-code policy on some repos and a separate enterprise Checkmarx One program gate on regulated or portfolio apps. That is two tools, two exception processes, and two dashboards.
Skip Checkmarx here if primary pain is custom security rules, PR-native policy, and modular SCA/secrets around a SAST engine your engineers can own. Skip Semgrep here if primary pain is an RFP-scale Checkmarx One platform with SAST plus sibling scanners, program policy, and enterprise triage.
Decide which operational pain owns the budget. Developer-owned rules-as-code SAST and PR policy: Semgrep. Enterprise Checkmarx One AppSec platform for RFP-scale SAST: Checkmarx. Only then open the quotes.
FAQs
Are Semgrep and Checkmarx the same SAST product?
No. Both can find security issues in first-party code and fail CI. Semgrep leads on developer-owned rules-as-code SAST and PR-native policy. Checkmarx leads on Checkmarx One as an enterprise AppSec platform with SAST at the core for RFP-scale programs.
Is Checkmarx still CxSAST?
CxSAST is the on-premises traditional SAST line. Current cloud packaging is Checkmarx One, where SAST is a required scanner. Next-Gen SAST and Checkmarx Fusion apply on Checkmarx One, not on classic on-prem CxSAST.
Do I need both?
Only if you deliberately want AppSec-owned YAML rules policy and a separate enterprise Checkmarx One program gate. Most teams pick the weekly queue that hurts more.
Is there a public list price?
Semgrep Free is $0 for up to 10 contributors; Teams starts at $30 per contributor per month (checked 9 Sep 2026). Checkmarx One is custom-quoted from developers, apps, and usage on the public pricing builder, with no published monthly list rate (checked 9 Sep 2026).
Is this a scored bake-off?
No. Order is editorial.

