Phishing Simulation and Awareness Tools for the Weekly Operator Queue
Campaigns, report buttons, LMS seats, and human-risk scores are different jobs.
Verizon’s 2026 DBIR still finds a human element in 62% of confirmed breaches, with social engineering among the top breach patterns.
A green annual training dashboard does not empty Monday’s queue. Operators still schedule simulations, triage employee reports, assign remedial modules, and explain click rates to risk committees. Completion theater and that weekly work are different jobs.
Phishing simulation platforms sit between those jobs. Some products are campaign engines that measure who clicked. Some are LMS libraries that prove compliance. Some turn the report button into a SOC intake path. The newer human-risk desks score people the way vulnerability tools score hosts. Inbox filters and DMARC stay on email security tools and DMARC tools.
This shortlist mixes the category leader, an adaptive engagement platform, a report-led SOC seat, an enterprise threat-intel LMS, a managed mid-market program, and one real open-source campaign toolkit.
How we evaluated
We read first-party product pages, pricing CTAs, licenses, and docs. We asked whether the product runs simulation campaigns you operate weekly, whether employee reports become a triage path, whether training is a real LMS or a landing-page slap, and whether human-risk scoring is a named control or a slide. Marketing pages count as claims, not as proof two tools do the same work.
| Tool | Best for | What to check |
|---|---|---|
| KnowBe4 | Breadth: sims, LMS, PAB, and SmartRisk in one desk | Commercial · published per-seat list · AIDA |
| Hoxhunt | Adaptive gamified training and human-risk outcomes | Commercial · quote · multi-channel sims |
| Cofense PhishMe | Report-button culture tied to real-threat sims | Commercial · Reporter · SOC triage path |
| Proofpoint ZenGuide | Enterprise risk-based LMS with threat-intel sims | Commercial · often bundled · Satori agent |
| Huntress Managed SAT | Managed mid-market episodes plus phishing sims | Commercial · Curricula lineage · try path |
| Gophish | Self-hosted open-source campaign toolkit | MIT · you run it · no LMS SaaS |
KnowBe4
Hoxhunt
Cofense
ZenGuide
Huntress
Gophish
KnowBe4
Best for breadth across simulations, LMS content, report button, and SmartRisk
KnowBe4 is the default awareness desk most mid-market buyers already recognize. The AI-Native SAT pitch combines training libraries, phishing and vishing simulations, the Phish Alert Button, Real-Time Coaching, and SmartRisk scores that roll user behavior into board-ready risk views.
That gap is why operators care about more than completion. KnowBe4’s own baseline claims the industry Phish-prone Percentage starts near 33.1% and can fall to about 4.1% after a year of continuous testing. The product still has to survive employees who treat simulations as office sport.
Key features:
- Unlimited phishing security tests plus callback, USB, and QR simulations
- Phish Alert Button and PhishER triage add-on path
- Foundation and Advanced training libraries with automated campaigns
- SmartRisk Engine, AIDA automation, and Real-Time Coaching
Why we like it:
Published per-seat list pricing is rare in this category, and the console covers the weekly campaign, report, and LMS jobs without forcing a second vendor for basic coverage.
Limits:
Engagement complaints show up whenever templates feel cartoonish. Enterprise human-risk buyers comparing adaptive platforms should not treat library size as the only scorecard.
License or pricing: Commercial SaaS. May 2026 USD list for a 3-year term starts at $2.40 per seat per month (SAT Foundation, 25–50 seats) and $3.75 for SAT Advanced at the same band. Volume steps down; 1001+ is quote-only.
Hoxhunt
Best for adaptive, gamified training that treats awareness as human-risk management
Hoxhunt markets itself as a human-risk platform rather than a content warehouse. Simulations personalize by role and history across email, SMS, phone, and Teams, then drop micro-training when someone fails. Gamification and automated difficulty are the product story, not a once-a-year SCORM dump.
Key features:
- Adaptive multi-channel phishing simulations
- Bite-sized awareness modules with AI-generated content options
- Automated triage help for employee-reported mail
- Behavior and engagement metrics aimed at board reporting
Why we like it:
It answers the engagement failure that classic LMS campaigns create. If the weekly pain is low report rates and employees who ignore training, Hoxhunt is the mid/premium alternative to KnowBe4-class breadth.
Limits:
Pricing is quote-only. Teams that mainly need a cheap campaign engine or a compliance library will overbuy the adaptive story.
License or pricing: Commercial SaaS. Quote-based per employee. Demo path on the first-party site.
Cofense PhishMe
Best for report-button culture tied to real-threat simulations and SOC intake
Cofense still centers PhishMe on conditioning people to report, then feeding those reports into a phishing defense workflow. Simulations lean on real phishing themes, including smishing, vishing, and QR lures, with Responsive Delivery that sends when users are active in mail.
Key features:
- Reporter button as a first-class control
- Multi-channel simulations beyond email-only campaigns
- Playbooks and Smart Suggest for scenario selection
- Analytics aimed at reporting behavior, not only click rates
Why we like it:
When the weekly queue is abuse-mailbox triage, a product that treats reporting as the outcome beats another LMS completion chart. Cofense keeps that SOC-shaped job visible.
Limits:
It is not the broadest training catalog on this list. Buyers who need deep compliance libraries plus phishing will often pair or prefer KnowBe4 or ZenGuide.
License or pricing: Commercial SaaS. Quote-based. Often evaluated as part of the broader Cofense phishing defense platform.
Proofpoint ZenGuide
Best for enterprise risk-based LMS fed by live Proofpoint threat intel
ZenGuide is Proofpoint’s people-risk LMS. It groups users by role and behavior, auto-enrolls learning paths, and markets AI agents such as Satori Phishing Simulation Agent and AI ThreatFlip that turn observed attacks into simulations. The Report Suspicious button spans email and mobile.
Key features:
- Behavioral and role-based risk insights
- Adaptive simulations and just-in-time coaching
- Gamified engagement dashboards
- Human Risk Explorer for board-level risk views
Why we like it:
If mail security already lives on Proofpoint, ZenGuide is the awareness seat that inherits the same threat themes instead of a generic template pack.
Limits:
Standalone pricing is opaque and often bundled. Teams without a Proofpoint email relationship should compare KnowBe4 and Hoxhunt on equal footing rather than assuming ecosystem lock-in is free.
License or pricing: Commercial SaaS. Quote-based; frequently sold with Proofpoint email and collaboration packages.
Huntress Managed SAT
Best for managed mid-market training episodes with phishing simulations done for you
Huntress Managed SAT (Curricula lineage) sells a managed program: story-driven episodes, phishing simulations built from Huntress threat intel, manager reminders, and reporting without a full-time awareness admin. Phishing Defense Coaching and behavior-based assignments target people who fail sims or get compromised in the wild.
Key features:
- Managed learning plans and monthly episode cadence
- Hands-on phishing simulations tied to current threats
- Custom Content Creator and compliance modules
- Gamification and recovery coaching after failures
Why we like it:
It is the credible mid-stage answer when KnowBe4 feels like too much console work and Gophish feels like too little program. MSPs and lean IT teams get a weekly queue that is already scheduled.
Limits:
Less operator authoring depth than KnowBe4 or Cofense for teams that want to craft every lure. Enterprise human-risk scoring desks will still look at Hoxhunt or ZenGuide.
License or pricing: Commercial SaaS. Public try/login path; seat pricing via sales. Fits SMB through mid-market and MSP delivery.
Gophish
Best for a self-hosted open-source toolkit when the job is campaigns only
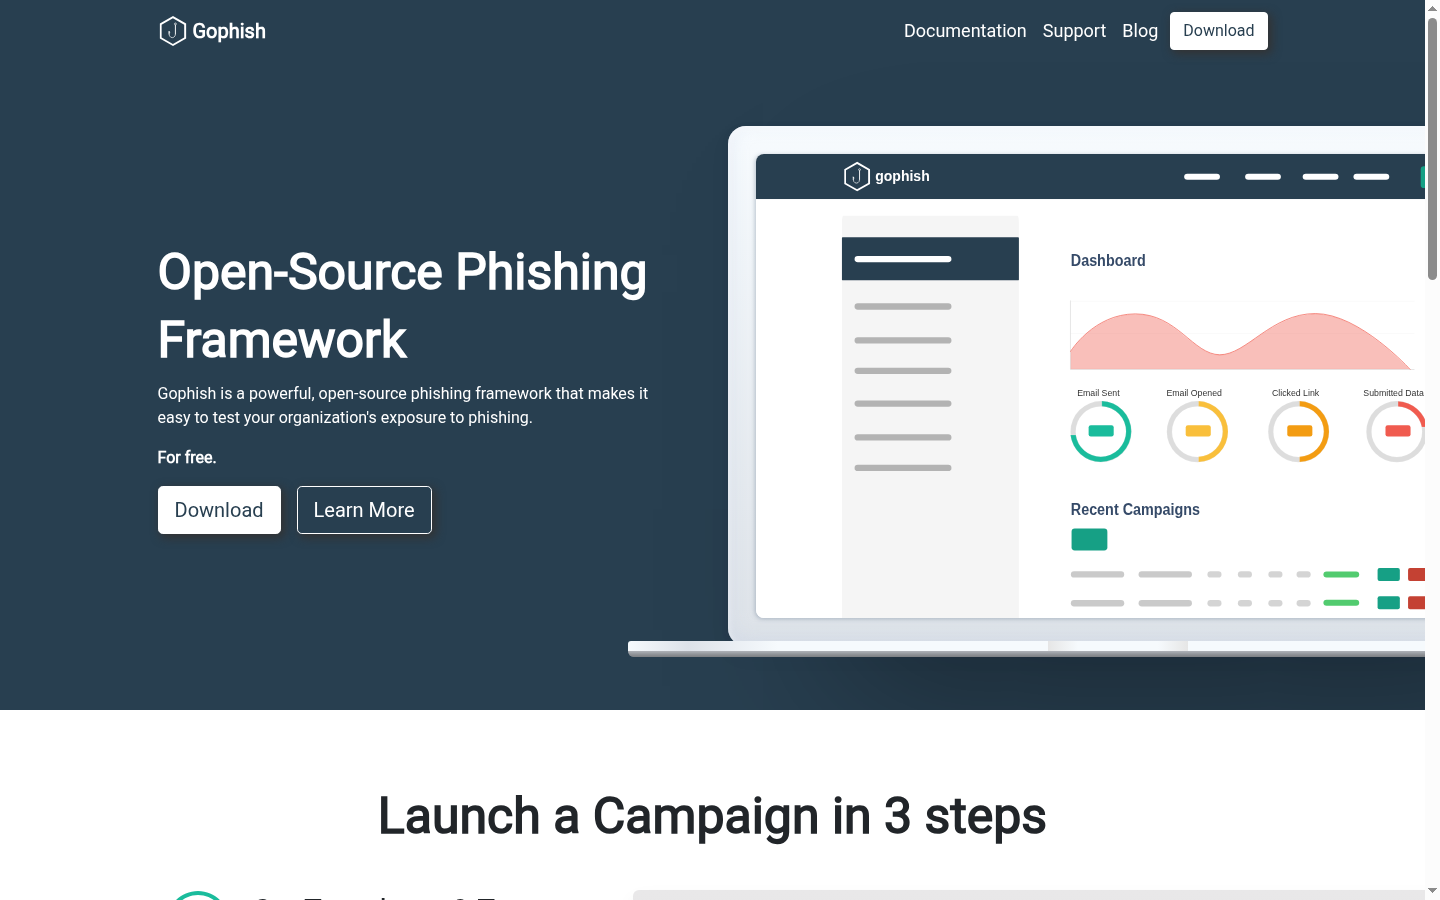
Gophish is the open-source phishing framework operators still reach for when they need sent/opened/clicked/submitted tracking without a SaaS LMS. You host it, build landing pages and SMTP profiles, and run campaigns. It is not a training content catalog and it is not a human-risk score product.
Key features:
- Campaign dashboard with sent, opened, clicked, and submitted metrics
- Templates, landing pages, and sending profiles you control
- Single-binary community edition under MIT
- API for automation in lab and red-team workflows
Why we like it:
It is a real OSS seat, not a parked README. Teams that already own training elsewhere can keep simulation campaigns on software they operate.
Limits:
You own SMTP reputation, legal review, and the training LMS gap. There is no SmartRisk, no managed episode library, and no vendor-run report triage.
License or pricing: MIT License (Gophish Community Edition). Free to run. You pay for infrastructure and operator time.
How to choose a phishing simulation tool
- Name the Monday job. If you need campaign metrics and landing pages, start with KnowBe4 or Gophish. If the pain is report triage, put Cofense on the shortlist. If engagement is dead, evaluate Hoxhunt before buying another SCORM pack.
- Separate LMS evidence from behavior change. Auditors want completion. Attackers care about click and report rates. Pick the primary KPI before comparing library size.
- Count channels. Email-only sims miss SMS, voice, QR, and Teams lures. Hoxhunt and Cofense document multi-channel paths; Gophish is email-campaign shaped unless you extend it.
- Keep filters on their own RFP. SEG and API inbox desks belong on email security tools. Do not force awareness vendors to replace MX controls.
What we left out
- Microsoft Attack Simulation Training: useful E5 starter, not a third-party platform buy on this shortlist.
- IRONSCALES: already covered as report remediation on email security tools.
- Mimecast Awareness, SoSafe, Living Security, CybSafe, usecure, and NINJIO: credible, but the sixth seat goes to Gophish for a real OSS campaign option.
- King Phisher: quieter than Gophish for the open-source campaign job in 2026.
What practitioners argue about awareness training
Live threads keep returning to the same tension: simulations can train report muscles or train people to tip each other off and treat training as theater. We quoted the argument, not the score.
Hacker News · May 2026
“We (and reseach) have found that the "phishing simulation" technique has not been effective. … We have seen people alerting each other on private channels "be careful with this email, that’s the phishing, simulation!". So IT have false data and people are not actually learning much…”
From the Shira Show HN thread (22 May 2026). The dissenting beat is that some teams still want realistic pressure tests; the shared worry is contaminated metrics when the campaign is obvious office gossip.
Hacker News · June 2026
“I hate him because of how many times I had to be put through mind numbing security training with his mug as the opener. ‘I’m Kevin Mitnick’ and KnowBe4 are seared into my brain at a ptsd level for terminal boredom.”
Engagement failure is a product risk even for the category leader. Adaptive and gamified desks exist because boredom is an operator metric, not just a joke.
Hacker News · August 2026
“Disclosure: I work at SafeInstinct, which sells security awareness training. We published this partly because the evidence base for our own category is weaker than the marketing suggests.”
Even a vendor in the category is arguing for skepticism. Treat Phish-prone charts as program evidence to challenge, not as proof the seat replaces mail filters.
If you need one desk for campaigns, LMS, and reporting, start with KnowBe4. If engagement is the failure mode, put Hoxhunt on the quote. If the weekly queue is report triage, evaluate Cofense. Extend Proofpoint with ZenGuide when threat intel already feeds that stack. Use Huntress Managed SAT when you want the cadence managed. Keep Gophish when the only job is a self-hosted campaign lab.
FAQs
Is this the same page as email security tools?
No. That page covers API inbox defense, gateways, report remediation for mail, and DMARC. This page is the phishing simulation and awareness cut: campaigns, LMS, report culture, and human-risk scoring.
Does KnowBe4 replace a secure email gateway?
No. KnowBe4 trains and tests people. Gateways and API desks filter or remediate mail. Many estates run both.
Is Gophish enough for compliance training evidence?
Usually not. Gophish measures campaign outcomes. Auditors typically want LMS completion records that a commercial awareness desk or Huntress-style managed program produces.
Is this a scored bake-off?
No. Order is editorial.

