Security Operations
Top AI SOC Tools in 2026: Triage and Automation Compared
Show the query and the evidence before the case closes. A sidecar that only restates the alert title is not triage.
Microsoft Security Copilot integrates with Microsoft Defender XDR and Microsoft Sentinel. It sits on those consoles. It is not a SIEM replacement.
A sidecar that never prints the query will still miss the case the SIEM already opened. A useful product shows the KQL and the evidence before it closes the ticket.
Copilot-on-SIEM, agentic triage over API, and a runner or case desk are different places the work lands. Playbooks that fire isolate and revoke without that review already live on SOAR tools.
Buy the shape that dumps a query a reviewer can rerun. Treating the sidecar as the queue is the wrong assumption.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof two products do the same work. We cared about whether triage shows the query, whether the product sits on a SIEM you already run, whether you operate it, and whether a case or workflow can leave the product.
| Tool | Best for | What to check |
|---|---|---|
| Dropzone AI | An autonomous analyst that queries the stack you already have | Commercial · agentic hunt · evidence trail |
| Microsoft Security Copilot | A copilot already sitting in Defender, Sentinel, Entra, Intune, and Purview | Commercial · copilot on Microsoft · hunt |
| Shuffle | An open-source SOAR you can actually run | AGPL-3.0 · you operate it · response |
| TheHive | Collaborative cases, observables, and Cortex responders | Commercial freemium · the case · you can host it |
| Keep | A single pane of glass over messy alerts | MIT + Enterprise · alert pane · respond |
| Vega | Federated hunt and transparent triage | Commercial · query in place · show the work |
Dropzone AI
Best for an autonomous analyst that queries the stack you already have
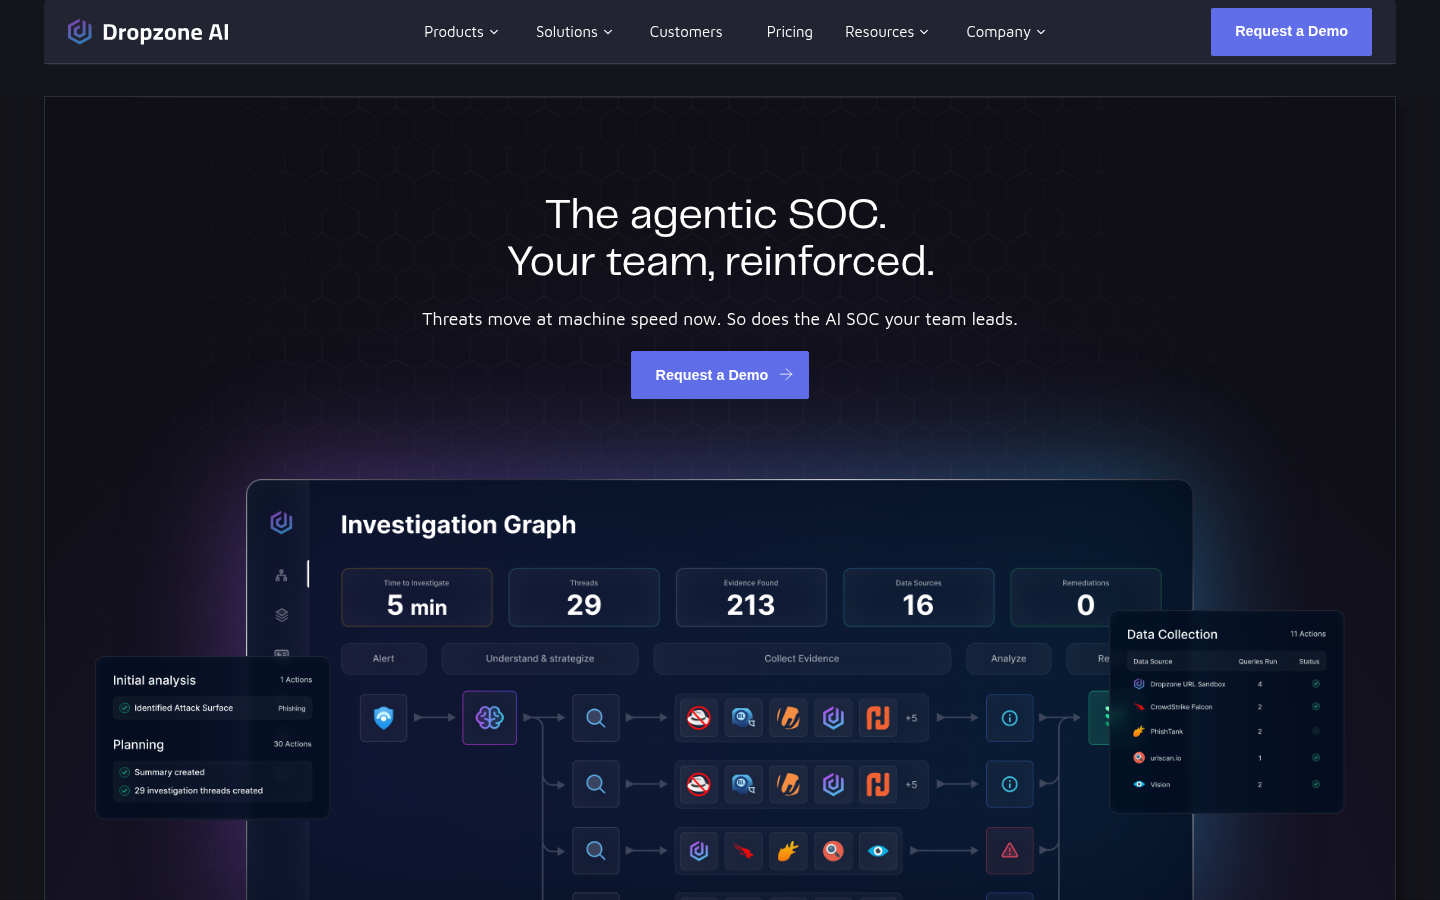
Dropzone investigates alerts across SIEM, EDR, identity, and email via API. No data lift. The site says the analyst shows the evidence behind each verdict.
It occupies the same job as a junior analyst without asking you to become a Microsoft shop or to ingest a lake.
Key features:
- End-to-end investigation with a visible evidence trail
- Hypothesis-driven hunts across SIEM, EDR, and cloud
- Integrations on the public docs, queried over API
- Self-guided demo on the public site
Why we like it:
When you want an investigation that shows its work and you will not move the lake, this is the agentic row.
Limits:
Commercial, sales-quoted. We could not find a current first-party price list.
License or pricing: Commercial.
Microsoft Security Copilot
Best for a copilot already sitting in Defender, Sentinel, Entra, Intune, and Purview
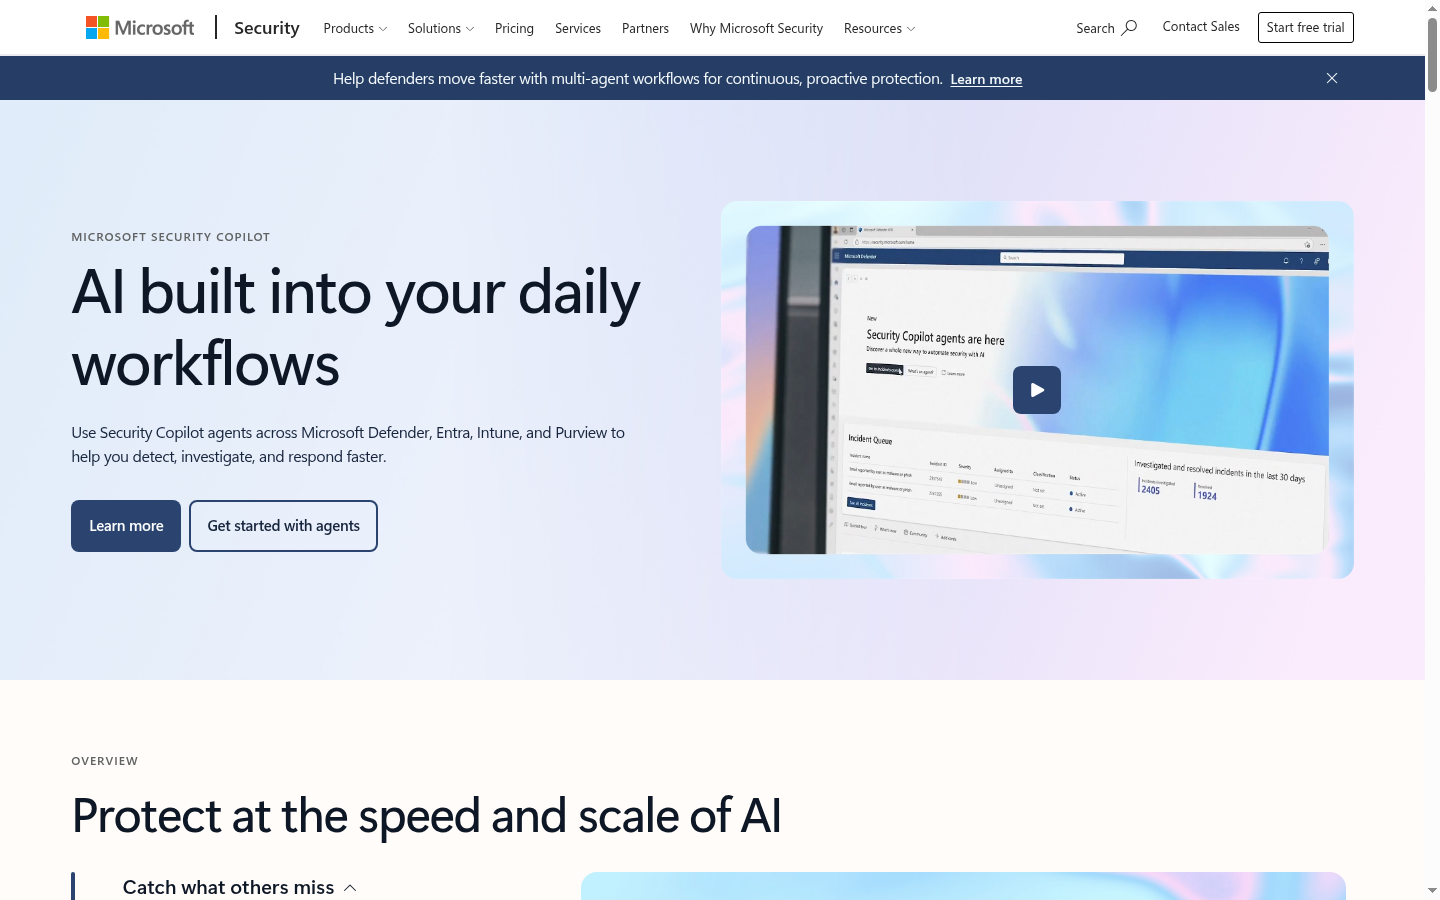
Security Copilot is the hyperscaler on this list. Standalone chat plus embedded agents in the Microsoft Security products you already open.
You do not migrate a lake to try it. The actual work is guidance and first-pass triage on that tenant.
Key features:
- Embedded agents in Defender, Entra, Intune, and Purview
- Natural-language hunt and KQL generation
- Promptbooks and partner plugins
- Inclusion on the public docs for eligible Microsoft plans
Why we like it:
If the tenant is already Microsoft-heavy, this is the copilot that sees the same incidents the analysts already open.
Limits:
Non-Microsoft telemetry needs plugins.
License or pricing: Commercial.
Shuffle
Best for an open-source SOAR you can actually run
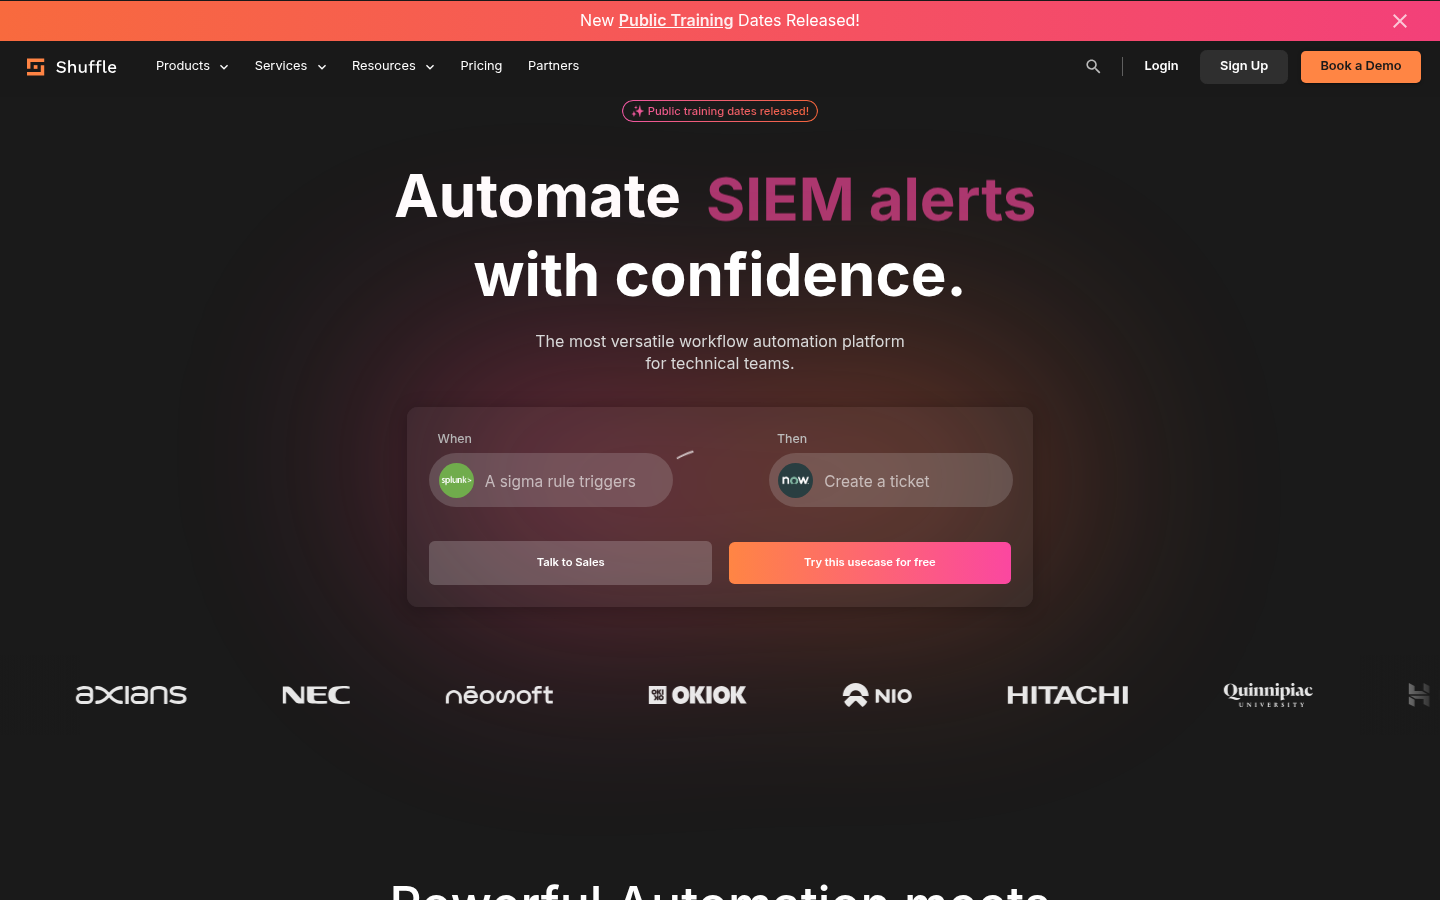
Shuffle is SOAR. Workflows you can read. Apps from OpenAPI. Self-host, cloud, or hybrid. The loop you get is the loop you draw.
Most AI SOC pitches skip the glue. This is the glue: webhook in, enrich, ticket, contain.
Key features:
- Workflow editor plus premade apps for common security tools
- Build new apps from OpenAPI specs
- Org and sub-org control aimed at MSSPs
- Optional hybrid sharing with shuffler.io
Why we like it:
A playbook you can export is rarer than a copilot slide. You can read the backend.
Limits:
You author the playbooks. There is no autonomous investigator in the default install.
License or pricing: AGPLv3 / MIT.
TheHive
Best for collaborative cases, observables, and Cortex responders
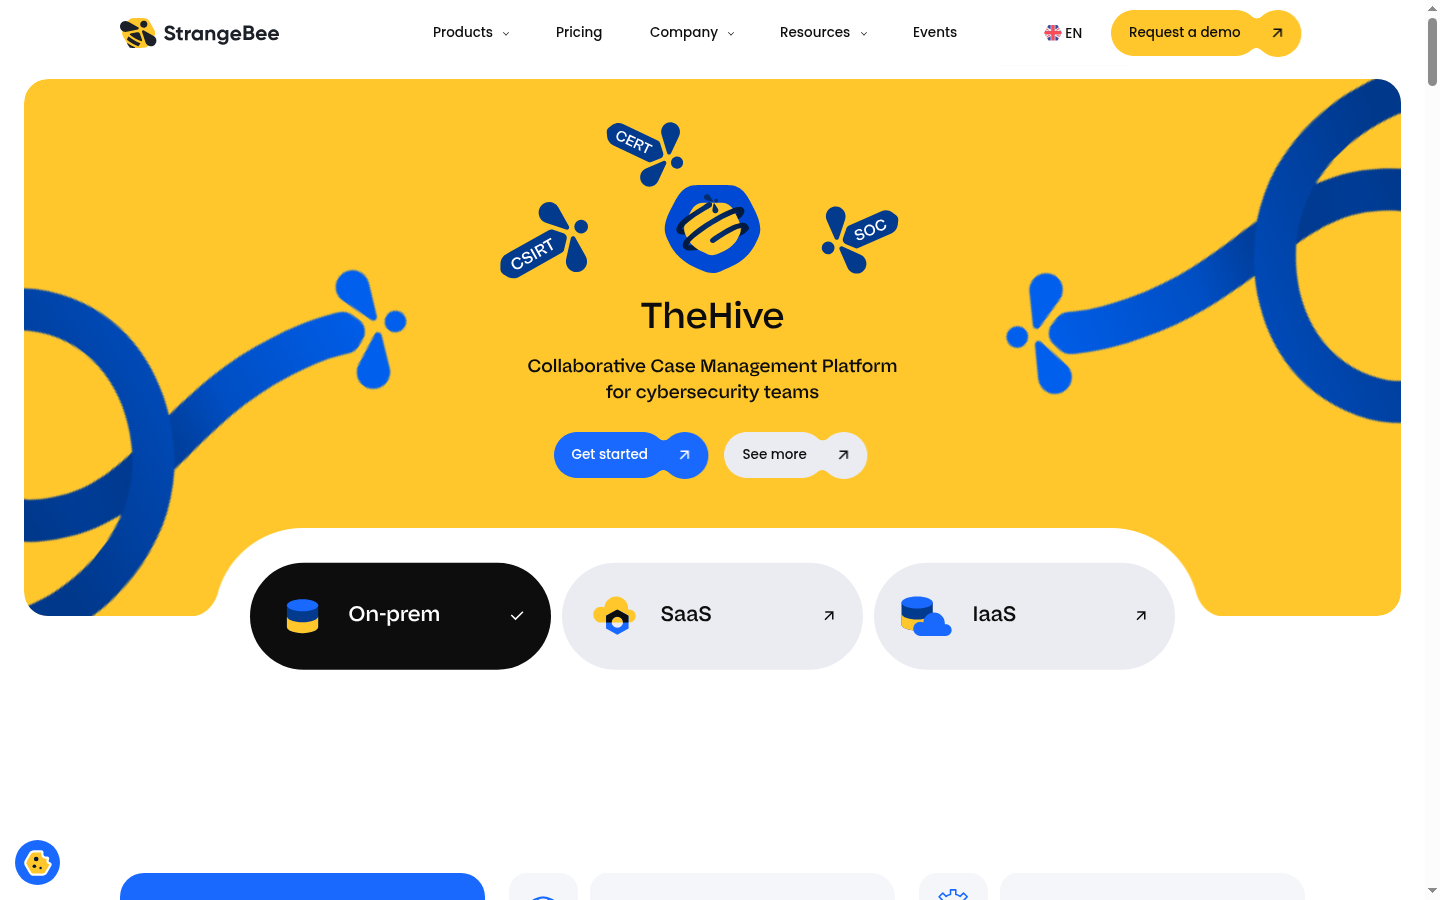
TheHive is the case desk. Alerts in, cases out, observables, Cortex responders. TheHive 5 is the live product. Three and four are end of life.
Do not call the current line open source. StrangeBee moved TheHive 5 to commercial freemium.
Key features:
- Alert triage, case tasks, observables, and timelines
- Cortex analyzers and responders
- MISP import and export; MITRE ATT&CK mapping
- Multi-tenant orgs; on-prem, SaaS, or IaaS images
Why we like it:
AI SOC tools still dump work into a case. Multi-party investigations and a report at the end are the parts copilots skip.
Limits:
Community is free for limited use. Gold, Platinum, and MSSP are paid. It is not an autonomous hunter.
License or pricing: TheHive 5 commercial.
Keep
Best for a single pane of glass over messy alerts
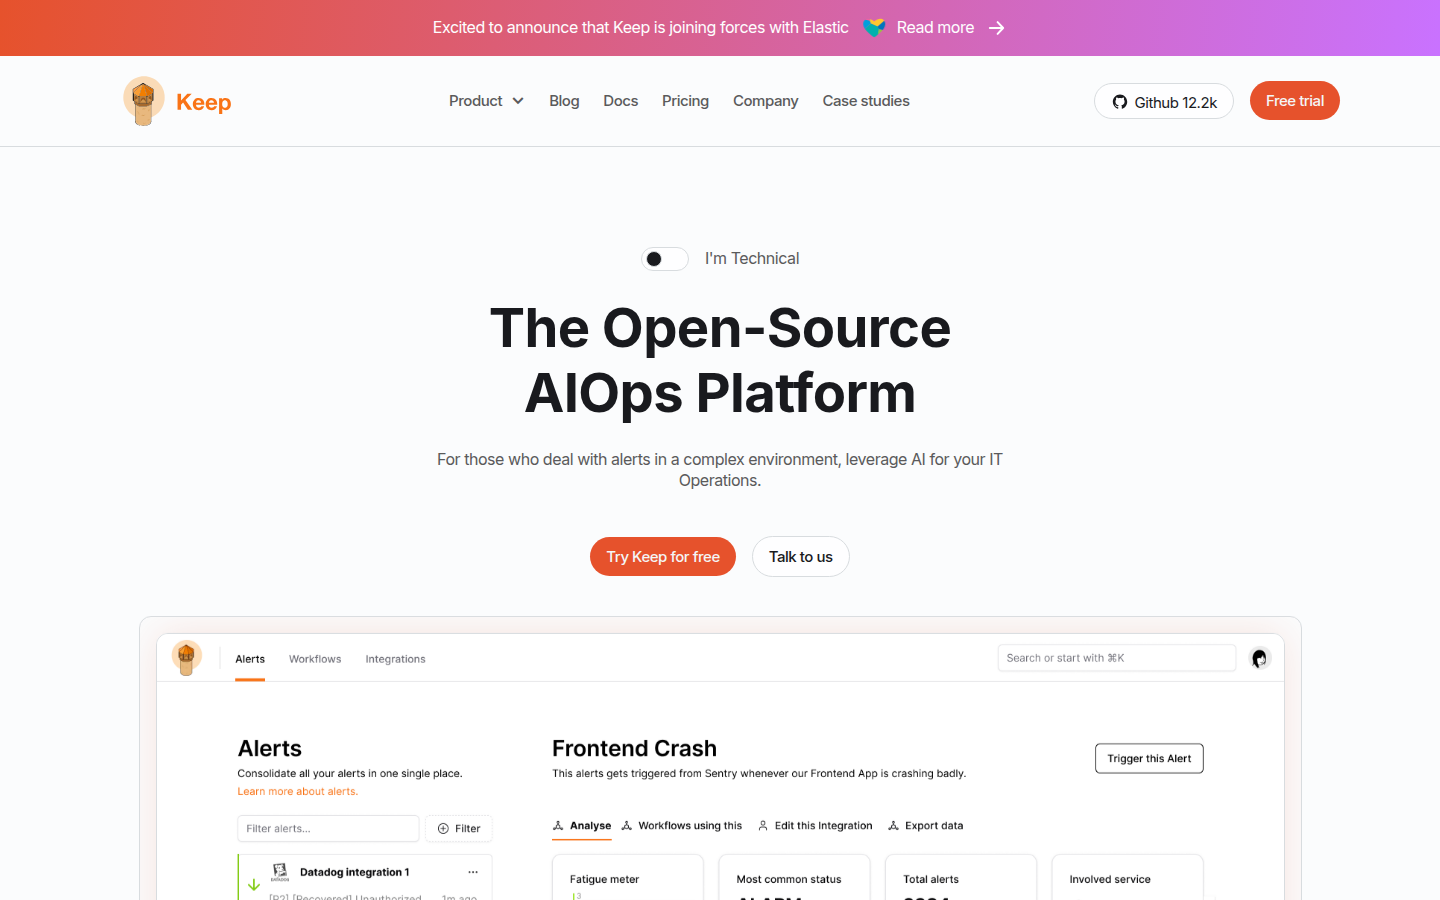
Keep is YAML workflows over monitoring tools. Dedup, enrichment, one alert UI. AI correlation sits on Enterprise. Elastic bought it in May 2025.
SOC noise is often just IT noise with a worse SLA. This is blunt about collapsing muted channels.
Key features:
- Dedup, correlation, filtering, and enrichment
- YAML workflows with triggers, steps, and actions
- Self-host with Docker or Kubernetes
- SSO and RBAC on the Enterprise-ready list
Why we like it:
When the hole is five Slack channels and no slice, a pane you can host is the useful buy.
Limits:
AIOps first, SOC second. It will not hunt across a SIEM you never connected.
License or pricing: MIT + Enterprise.
Vega
Best for federated hunt and transparent triage
Vega markets a post-SIEM agentic platform. The mesh queries data where it already lives, then hunts, detects, and triages in one loop.
The interesting claim is architectural. Most copilots summarize what a SIEM already ingested. Their pages refuse that tax and still show the work.
Key features:
- Security Analytics Mesh: natural language, KQL, or MCP in place
- Agentic hunting, detection skills, and triage in one investigation
- Question, query, and evidence trail meant to stay visible
- No-ingestion pitch on the public site
Why we like it:
When you are leaving a SIEM because half the sources never landed, a mesh that still shows the query is the agent that still shows the query.
Limits:
Founded 2024. Not an EDR and not a case desk. No public list price.
License or pricing: Commercial. No public list price.
How to choose an AI SOC tool
Four questions before the quote. Names below are tools, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Can a reviewer see the query and the evidence before a case auto-closes? | A summary is not a verdict you can audit. | Dropzone and Vega sell a visible trail. Copilot generates hunt KQL on a tenant you already open. | Silent auto-close with no query. |
| Are we buying a copilot on a SIEM we already pay for, or an agentic loop? | That is the migrate-or-not fork. | Microsoft Security Copilot on Defender. Dropzone over API. Vega as a mesh that refuses ingest. | A fourth copilot on a console nobody opens. |
| Where does the case live if the agent is wrong tomorrow? | A finding that dies in a vendor chat is not a record. | TheHive is the case desk. Shuffle is the runner you can export. | No export path. |
| Do we operate the glue? | A playbook you cannot read is a hope. | Shuffle and Keep you can host. Copilot and Dropzone you cannot. | An action runner with no author. |
AI SOC threads treat silent auto-close as the failure mode. A summary is not a verdict you can audit.
Start with the copilot on a SIEM you already pay for, and still demand the query. Pick a runner you can read if you need an action after the note.
FAQs
Is Vega a SIEM or an EDR?
Neither, on their own pages. Vega markets a post-SIEM agentic platform on a Security Analytics Mesh. It does not ship an endpoint sensor.
Is TheHive still open source?
The live product is not. TheHive 5 is StrangeBee commercial freemium. TheHive 3 reached end of life on 31 December 2021 and TheHive 4 end of support on 31 December 2022.
Does Shuffle or Keep replace an AI SOC analyst?
No. Shuffle is a SOAR you program. Keep is an alert-management layer. They shrink the queue and fire the actions. They do not independently investigate a novel compromise.
Is this a scored bake-off?
No. Order is editorial.

