Identity
Best Certificate Lifecycle Tools for CLM in 2026
An expired cert still takes production down at 3am.
A single forgotten TLS certificate can still remove a login path for 1000s of users with no CVE to blame. Certificate lifecycle management discovers, issues, renews, installs, and retires machine identities before expiry becomes an outage.
CyberArk Certificate Manager (Venafi) and peers split between enterprise machine-identity control planes, CA-centric portals, network-device automation, cloud-native PKI, and Kubernetes-native issuance.
If privileged human access is the pain, see PAM tools. For identity threat detection, use ITDR tools.
How we evaluated
We read first-party CLM, machine-identity, and cert-manager pages on 19 Sep 2026. We asked whether discovery covers multi-CA estates, whether renewal and install automation reaches network devices and workloads, whether Kubernetes paths exist, and whether an open path is first-class. Outage anecdotes are community evidence, not vendor scorecards.
| Tool | Best for | What to check |
|---|---|---|
| CyberArk Certificate Manager (Venafi) | Enterprise machine-identity control plane | Commercial · sales-led |
| Keyfactor Command | Vendor-neutral CLM with strong AD CS depth | Commercial · quote-based |
| DigiCert Trust Lifecycle Manager | CA-centric CLM for DigiCert estates | Commercial · DigiCert packaging |
| AppViewX AVX ONE CLM | Network-device certificate automation | Commercial · workflow-heavy |
| HashiCorp Vault PKI | Short-lived cloud-native certificates | Open core · enterprise options |
| cert-manager | Kubernetes certificate automation | Open source · cluster-scoped |
CyberArk Certificate Manager (Venafi)
Best for large regulated machine-identity programs
CyberArk Certificate Manager, the Venafi platform lineage, is the long-running enterprise control plane for discovering and governing certificates across large machine-identity estates.
Choose it when integration breadth and regulated scale dominate the RFP.
Key features:
- Broad discovery and policy control
- Multi-CA and machine-identity workflows
- Enterprise integrations including Kubernetes paths via ecosystem
- Sales-led packaging for large programs
Why we like it:
Fortune-scale PKI teams get a control plane sized for thousands of applications and owners.
Limits:
Commercial and sales-gated. Smaller teams may find Keyfactor or DigiCert paths faster to start.
License or pricing: Commercial. Quote-based. Checked 19 Sep 2026.
Keyfactor Command
Best vendor-neutral CLM with deep AD CS and automation
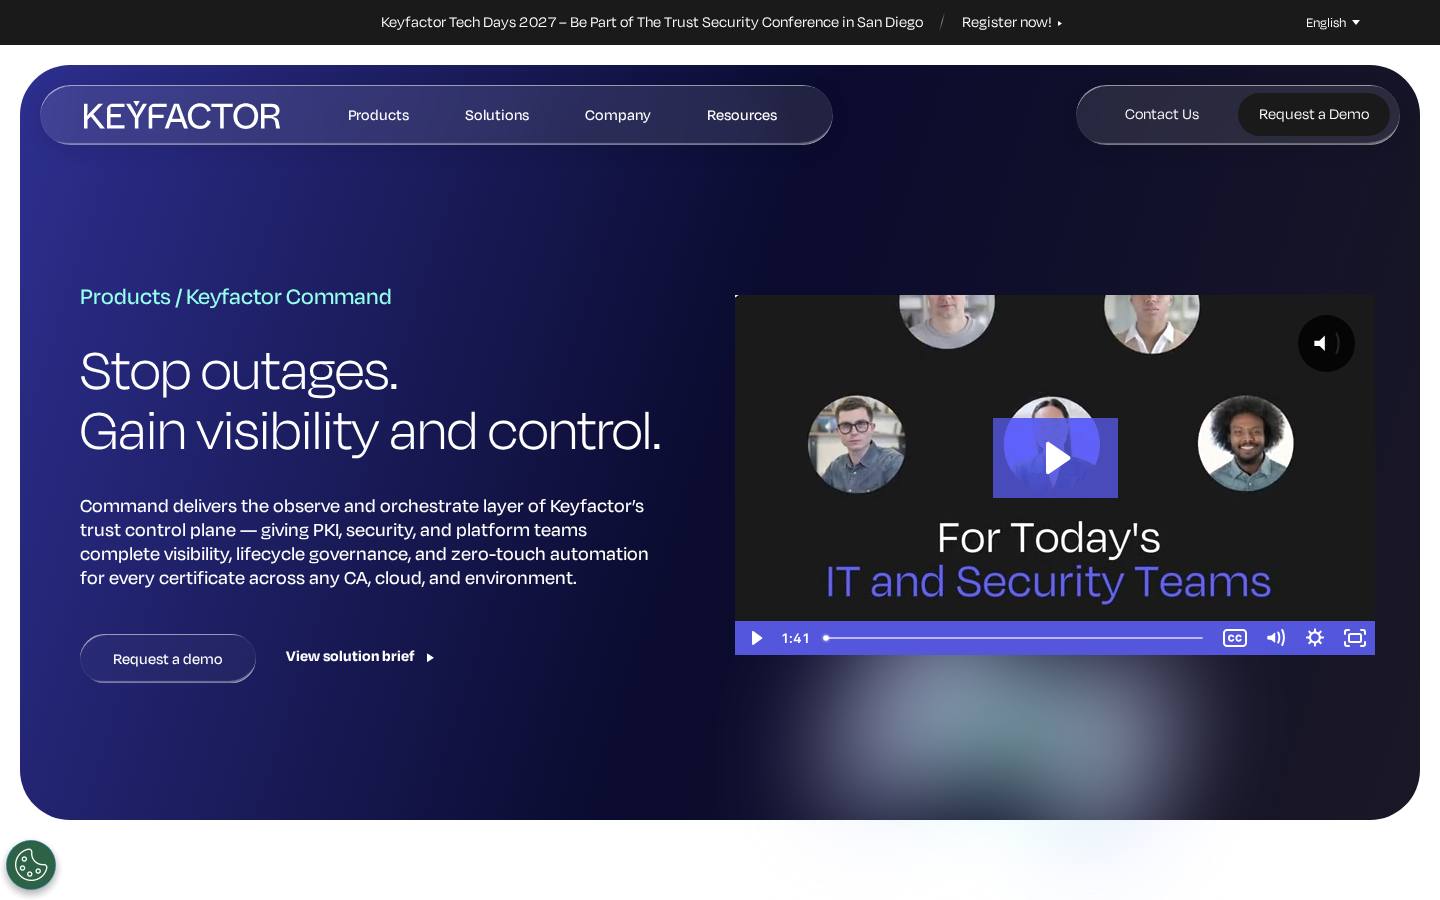
Keyfactor Command positions as the observe-and-orchestrate layer for certificates across public, private, and cloud CAs, with strong AD CS and EJBCA adjacency in the Keyfactor stack.
It is the pragmatic multi-CA pick many teams shortlist beside Venafi.
Key features:
- Continuous discovery and inventory
- Orchestrators for renewal and install
- AD CS and multi-CA connectivity they document
- PQC and crypto-agility readiness messaging
Why we like it:
Multi-CA enterprises get automation without assuming a single public CA portal.
Limits:
Commercial quote. Confirm orchestrator coverage for your ADCs and cloud workloads.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
DigiCert Trust Lifecycle Manager
Best when DigiCert is already the public CA of record
DigiCert Trust Lifecycle Manager / CertCentral packaging joins public certificate issuance with lifecycle workflows DigiCert documents for enterprise customers.
Pick it when certificate spend and issuance already center on DigiCert.
Key features:
- Public CA issuance plus CLM workflows
- Discovery and renewal automation they publish
- Private PKI options in DigiCert packaging
- Enterprise portal and API access
Why we like it:
DigiCert-first shops reduce swivel-chair between CA portal and a separate CLM.
Limits:
Commercial and DigiCert-centric. Multi-CA neutrality may favor Keyfactor or Venafi.
License or pricing: Commercial. Often tied to certificate spend; confirm on 19 Sep 2026.
AppViewX AVX ONE CLM
Best for network-device certificate automation workflows
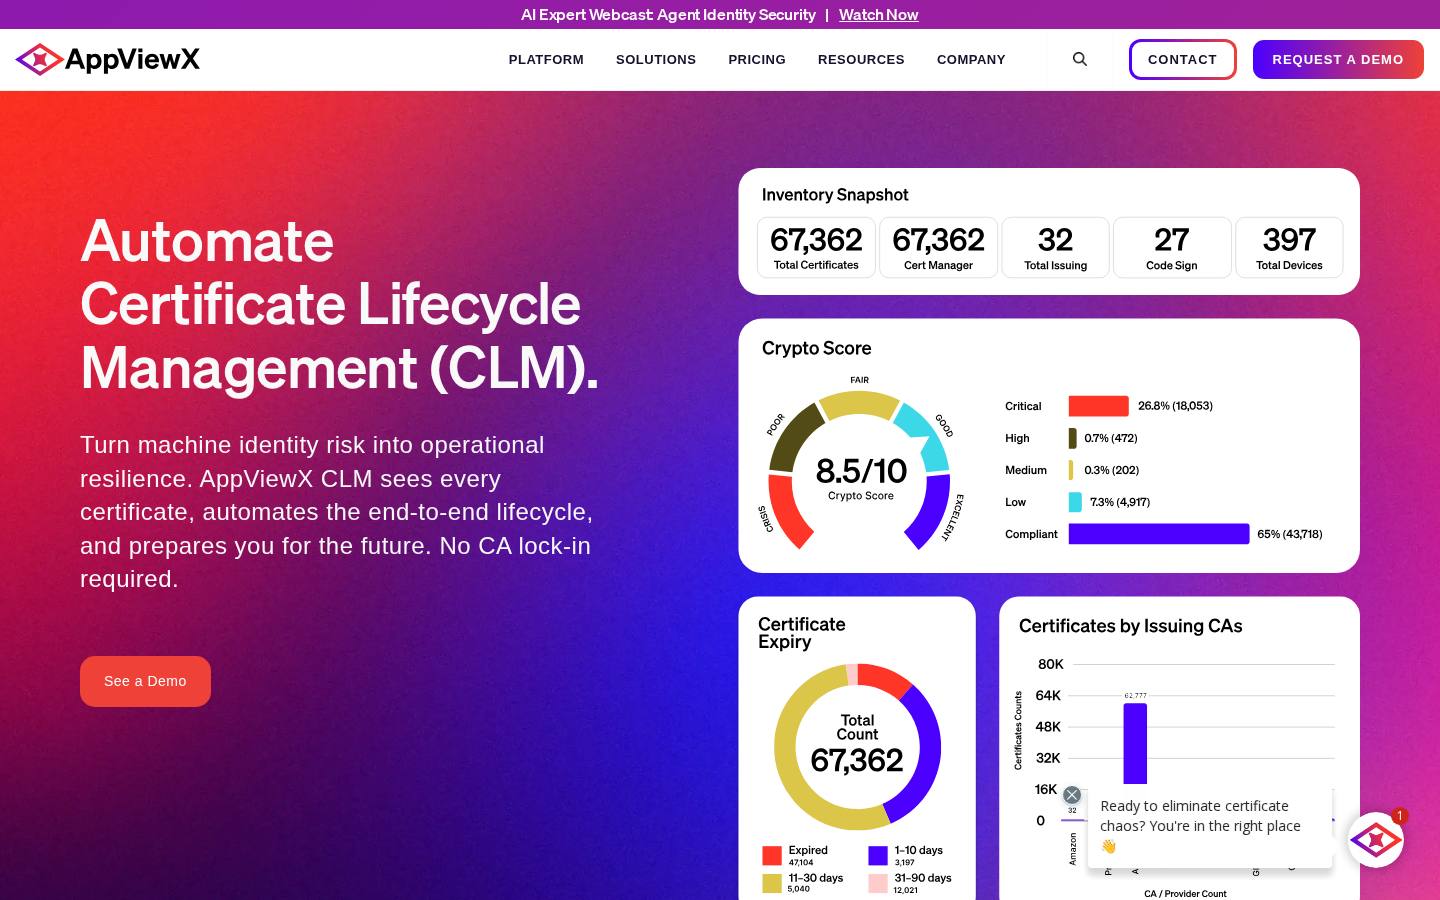
AppViewX CLM emphasizes end-to-end certificate automation with particular strength on network devices such as load balancers and ADCs.
Choose it when F5/Citrix-class installs are where renewals fail.
Key features:
- Discovery across hybrid estates
- Visual workflow automation
- Network device install and renewal focus
- Multi-CA support without lock-in they advertise
Why we like it:
Network teams get CLM that speaks ADC workflows other tools treat as afterthoughts.
Limits:
Commercial. Validate Kubernetes and cloud workload coverage if those dominate.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
HashiCorp Vault PKI
Best for short-lived cloud-native certificates in Vault estates
Vault PKI issues short-lived certificates as part of the Vault secrets platform, fitting dynamic cloud workloads that should not rely on year-long static certs.
It is DevOps PKI more than enterprise multi-CA discovery CLM.
Key features:
- Dynamic short-lived certificate issuance
- API-driven workflows for apps and services
- Integration with Vault auth and policy
- Enterprise Vault packaging options
Why we like it:
Platform teams already on Vault get certificate issuance that matches ephemeral workloads.
Limits:
Not a full multi-CA discovery CLM by itself. Pair with enterprise CLM or cert-manager for broader inventory.
License or pricing: Open core with commercial Vault editions. Confirm packaging on 19 Sep 2026.
cert-manager
Best open Kubernetes certificate issuance automation
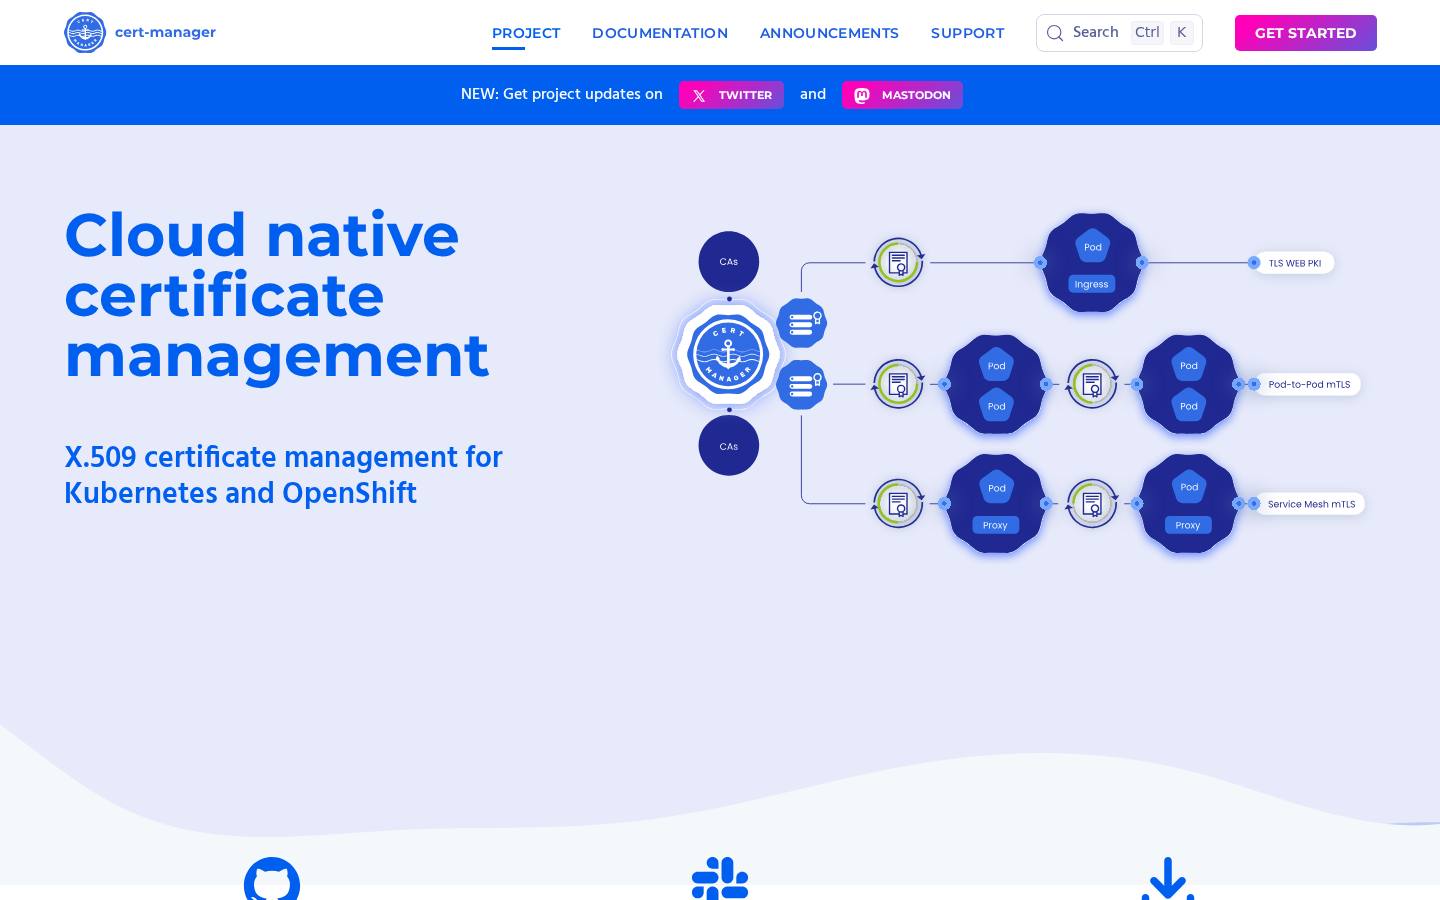
cert-manager automates certificate issuance and renewal inside Kubernetes using issuers such as Let’s Encrypt, Vault, Venafi, and others.
It is cluster-scoped automation, not enterprise-wide multi-CA CLM for every laptop and ADC.
Key features:
- Kubernetes-native certificate resources
- ACME and external issuer integrations
- Automated renewals in-cluster
- Open-source project with wide ecosystem use
Why we like it:
Platform engineers keep cert-manager as the default K8s issuance path even beside Venafi or Keyfactor.
Limits:
Kubernetes only. No global enterprise inventory of non-cluster certificates by itself.
License or pricing: Open source. Confirm project license on 19 Sep 2026.
How to choose a certificate lifecycle tool
Four questions before the quote. Names are the shortlist, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| How many CAs and certificate owners exist? | Multi-CA estates break CA portals. | Venafi or Keyfactor for neutrality; DigiCert if spend is DigiCert-first. | Assuming one portal sees every private CA. |
| Where do renewals fail operationally? | ADCs and firewalls are common outage sources. | AppViewX for network-device workflows. | CLM that stops at email alerts. |
| Are workloads ephemeral? | Year-long certs fight cloud-native reality. | Vault PKI and cert-manager short-lived paths. | Static certs copied into every pod. |
| Is Kubernetes the main issuance surface? | Cluster automation differs from enterprise CLM. | cert-manager first; enterprise CLM for the rest. | Buying only enterprise CLM then ignoring clusters. |
What practitioners argue about certificate lifecycle
Threads are about inventory and outages, not logo wars. CLM fails when nobody knows where the certs live.
Hacker News
“Operationally, the issue is rooted in simple monitoring and accurate inventory. You also need to know where all your certificates are located. We were using Venafi for the auto discovery and email notifications.”
Dec 2025 comment (linked in the Venafi entry). Inventory remains the CLM failure mode.
cert-manager
“cert-manager adds certificates and certificate issuers as resource types in Kubernetes clusters, and simplifies the process of obtaining, renewing and using those certificates.”
Project framing on cert-manager.io (same project URL linked in the entry). Kubernetes issuance is a different job than enterprise multi-CA CLM.
If privileged access is next, read PAM tools. For identity attacks after login, use ITDR tools.
FAQs
Is CLM the same as a public CA portal?
No. A CA portal issues certificates. CLM discovers, renews, installs, and governs certificates across CAs and environments.
Do I still need cert-manager if I buy Venafi or Keyfactor?
Often yes for Kubernetes-native issuance. Enterprise CLM may integrate with cert-manager rather than replace it.
Can Vault PKI replace enterprise CLM?
Vault PKI excels at short-lived app certificates. It does not by itself inventory every ADC and legacy private CA certificate.
Is this a scored bake-off?
No. Order is editorial.