Cloud Security
Best CNAPP Tools for Cloud-Native Protection in 2026
CSPM can be green while a vulnerable workload still reaches the public role.
Teams often split cloud risk across 3 green dashboards: CSPM for accounts, image scans for registries, and a runtime sensor for clusters. Each queue can look healthy while a public role, a critical CVE, and a privileged identity still form one path.
CVE-2024-21626 in runc showed how a container breakout condition becomes urgent when the workload also has cloud reach. A CVE list alone does not explain that path. CNAPP is the category that tries to join posture, workload, and runtime context into one prioritized risk view.
This shortlist covers commercial platforms that sell CSPM+CWPP+runtime/graph class coverage. It is not the CLI CSPM shelf on CSPM tools, and it is not the mixed OSS-plus-platform shelf on cloud security platforms.
How we evaluated
We read first-party CNAPP product pages, pricing CTAs, and module descriptions on 17 Sep 2026. We asked whether the product correlates posture with workload and identity context, whether runtime is a named pillar or a slide, whether deployment is agentless-first or agent/runtime-deep, and whether packaging is one CNAPP SKU or a pile of add-ons. Marketing pages are claims.
| Tool | Best for | What to check |
|---|---|---|
| Wiz | Agentless Security Graph CNAPP | Commercial · custom quote |
| Prisma Cloud | Code-to-cloud enterprise suite | Commercial · module SKUs |
| Sysdig Secure | Runtime-first CNAPP | Commercial · Falco lineage |
| Aqua Platform | Container-lifecycle CNAPP | Commercial · quote |
| Falcon Cloud Security | Cloud risk inside Falcon | Commercial · Falcon packaging |
| Tenable Cloud Security | Exposure-led CNAPP + CIEM heritage | Commercial · quote |
Wiz
Best for agentless Security Graph CNAPP coverage
Wiz connects cloud accounts through APIs and builds a Security Graph that links misconfigurations, vulnerabilities, identities, and data. First-party CNAPP pages emphasize toxic combinations and attack paths rather than isolated CSPM queues.
On this shortlist Wiz is the agentless graph seat. It overlaps the platforms page on purpose; here the job is CNAPP correlation across CSPM, CWPP signals, and path risk.
Key features:
- Agentless multi-cloud inventory via APIs
- Security Graph toxic-combination prioritization
- Code-to-cloud and runtime modules Wiz documents
- Ticket and developer workflows they publish
Why we like it:
When the buying question is which risks are reachable together, Wiz’s graph framing matches CNAPP better than a flat misconfig list.
Limits:
Commercial custom quote. Agentless scanning clones volumes to Wiz infrastructure on paths they document; legal and residency reviews still matter.
License or pricing: Commercial. Custom quote on wiz.io/pricing as of 17 Sep 2026.
Prisma Cloud
Best for code-to-cloud breadth in a large enterprise suite
Prisma Cloud is Palo Alto Networks’ CNAPP: CSPM, CWPP, IaC, runtime, and related modules under one brand. First-party pages stress code-to-cloud visibility across build and run.
Choose Prisma when platform breadth and an existing Palo Alto relationship matter more than a lean agentless-only rollout.
Key features:
- CSPM and compliance posture modules
- Workload and container protection paths they document
- IaC and pipeline scanning
- Runtime defense options in the Prisma Cloud suite
Why we like it:
The suite answer when procurement already standardized on Palo Alto and needs CNAPP coverage under one contract family.
Limits:
Commercial. Module packaging is easy to over-buy. Confirm which CNAPP pillars are on the SKU, not only the umbrella name.
License or pricing: Commercial. Sales-quoted as of 17 Sep 2026.
Sysdig Secure
Best for runtime-first CNAPP with Falco lineage
Sysdig Secure grew from runtime visibility and open-source Falco. The commercial CNAPP story still leads with live workload detection, then posture and scanning around that center of gravity.
That is the opposite of agentless-first graphs: you buy Sysdig when catching what a container does at runtime is the urgent job.
Key features:
- Runtime threat detection rooted in Falco heritage
- Image and IaC scanning in the Secure product line
- Kubernetes and cloud posture views they document
- Forensics and incident response workflows
Why we like it:
Runtime-first CNAPP for Kubernetes-heavy estates that already believe process and syscall context.
Limits:
Commercial quote. Agent and eBPF deployment is operational work. Posture breadth should be proven against a graph-first rival in PoC.
License or pricing: Commercial. Quote-only on sysdig.com/pricing as of 17 Sep 2026.
Aqua Platform
Best for container-lifecycle depth inside a CNAPP
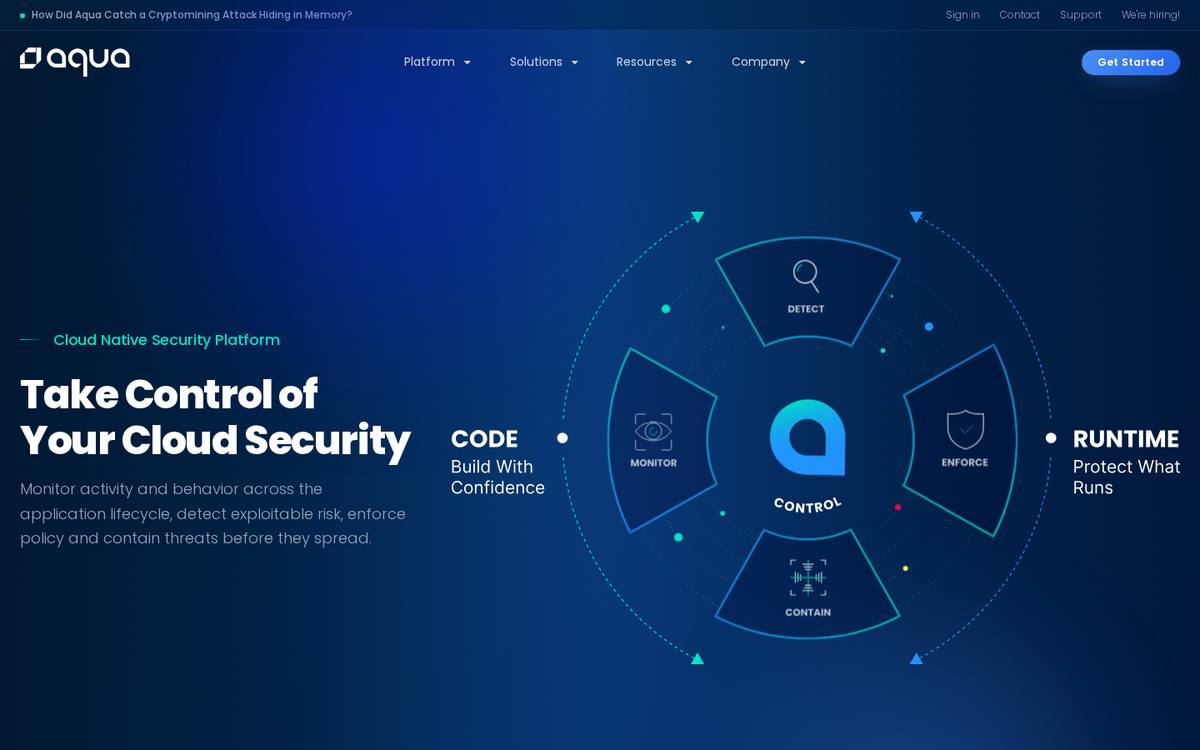
Aqua builds CNAPP capability from container and supply-chain roots: image assurance, admission controls, and runtime policies for cloud-native workloads. First-party pages still read container-native even as the platform widens.
Pick Aqua when container lifecycle controls are the center of the CNAPP evaluation, not a checkbox module.
Key features:
- Image scanning and assurance pipelines
- Admission and policy controls they document
- Runtime protection for containers and serverless paths
- Supply-chain and SBOM-oriented workflows
Why we like it:
Container-depth CNAPP when Kubernetes and image gates are the daily risk surface.
Limits:
Commercial. Multi-cloud CSPM breadth may trail graph-first rivals; validate outside container estates.
License or pricing: Commercial. Quote CTAs on aquasec.com/pricing as of 17 Sep 2026.
CrowdStrike Falcon Cloud Security
Best for consolidating cloud risk into Falcon
Falcon Cloud Security extends CrowdStrike’s platform into cloud workload and posture use cases so cloud findings share the console teams already use for endpoints.
This is the consolidation CNAPP seat: one operator workflow across endpoint and cloud, not the deepest agentless-only graph story.
Key features:
- Cloud posture and workload protection in Falcon
- Runtime and agent-based cloud protections they document
- Identity and threat context shared with Falcon
- Unified detection workflows for Falcon customers
Why we like it:
Strong when Falcon is already the SOC home and adding a second cloud console would split response.
Limits:
Commercial Falcon packaging. Agentless-only buyers should compare Wiz or Tenable on deployment model.
License or pricing: Commercial Falcon licensing. Quote-only as of 17 Sep 2026.
Tenable Cloud Security
Best for exposure-led CNAPP with CIEM heritage
Tenable Cloud Security (Ermetic lineage) frames CNAPP as exposure management: toxic combinations across identities, vulnerabilities, and cloud posture. CIEM depth remains a visible part of the story.
It is the mid-to-enterprise alternative when you want CNAPP plus strong identity exposure without defaulting to Wiz or Prisma.
Key features:
- Risk exposure and toxic-combination analysis
- CIEM-oriented entitlement insights
- CSPM and workload findings in one product family
- Integration into Tenable One exposure narratives they publish
Why we like it:
Exposure-management CNAPP with identity emphasis for teams already in the Tenable ecosystem.
Limits:
Commercial. Confirm CNAPP vs vulnerability-management SKU boundaries on the quote.
License or pricing: Commercial. Sales-quoted as of 17 Sep 2026.
How to choose a CNAPP tool
Four questions before the multi-year cloud security quote.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Do we need attack-path context or another misconfig feed? | CNAPP value is correlation. | Wiz / Tenable for graph-exposure; reject CSPM-only SKUs labeled CNAPP. | A CSPM relabeled as CNAPP with no workload context. |
| Is runtime a pillar or a slide? | Breakouts happen after admit. | Sysdig / Aqua when sensors matter; confirm runtime on the quote. | Runtime sold as a roadmap slide only. |
| Are we consolidating onto an existing platform? | Operator attention is finite. | Falcon or Prisma when that suite is already home. | A fourth console for the same cloud accounts. |
| What is in the SKU? | CNAPP bundles hide module gaps. | Written pillar list: CSPM, CWPP/runtime, identity/CIEM, IaC. | Umbrella brand with posture-only entitlements. |
What practitioners argue about CNAPP
The live argument is less “who won a quadrant” and more whether agentless graphs and runtime sensors answer the same morning queue.
Hacker News
“Wiz combines a graph search for asset management with agentless vuln and malware scanning that clones EBS volumes and scans them on their infrastructure.”
Practitioner summary quoted on HN in Mar 2025 (permalink in the Wiz entry). The pushback in related threads is data residency and trust in vendor-side scanning copies, which belongs in legal review.
Hacker News discussion
“Go fat binaries and big stdlibs cause most enterprise-mandated CVE scanners to light up with zillions of false positives constantly.”
May 2026 thread about scanner noise. That is why CNAPP buyers ask for reachability and runtime context instead of raw CVE counts alone. Second HN mention is text-only.
If you only need account misconfig checks, stay on CSPM tools. If you need the mixed OSS-plus-platform shelf, use cloud security platforms. For entitlements alone, see CIEM tools.
FAQs
Is CNAPP the same as CSPM?
No. CSPM focuses on cloud account and resource misconfigurations. CNAPP aims to combine CSPM with workload protection, often identity and runtime context, into one prioritized risk program.
Why is Wiz on more than one SecureCoding list?
Because buyers search different jobs. Platforms and CSPM pages cover adjacent shelves. This page frames Wiz as a CNAPP correlation platform next to runtime-first and suite alternatives.
Does CNAPP replace container image scanning in CI?
No. Pipeline scanners still gate builds. CNAPP correlates what reached production with cloud context. See also container security tools.
Is this a scored bake-off?
No. Order is editorial.