GRC and Compliance
Vendor Risk Management Tools in 2026: 6 Options for Third-Party Security Reviews
Open the report and check where production keys for that vendor actually sit. An unread A grade is not a review.
Expertise: GRC and Compliance · Level: Intermediate · 6 min read
The vendor dashboard showed an A. Nobody opened the report. Production API keys for that vendor still sat in 1 shared inbox.
Vendor risk is the packet you send outside the company: a questionnaire, an outside-in grade, a file you can show an auditor. A score nobody read is not a review.
Collectors you run on systems you operate are a different packet. This shortlist is the third party. The production miss is a vendor with a pretty grade and a key that never rotated.
Questionnaires you send, outside-in ratings, and evidence files you can export split that packet. Choose the review someone will actually open before the contract renews, not the unread A on a dashboard nobody exported before renewal.
How we evaluated
We read first-party docs, source, licenses, and release notes, and we treat a marketing page as a claim, not as proof that two products do the same work.
We cared about whether the product is an outside-in rating or a questionnaire desk, whether it is a suite module or a focused product, and whether the docs treat a grade as a signal rather than access.
We read first-party docs, licenses, and release notes. Unless a write-up says otherwise, we did not run a paid tenant.
| Tool | Best for | What to check |
|---|---|---|
| SecurityScorecard | Outside-in grade on a vendor you already contract | Outside-in grade · commercial · portfolio view |
| BitSight | The other known security rating | Outside-in grade · commercial · enterprise motion |
| Whistic | Questionnaire exchange vendors will actually finish | Questionnaire exchange · commercial · vendor profiles they sell |
| ProcessUnity | TPRM workflow on a GRC desk you staff | TPRM workflow · commercial · issue tracking |
| OneTrust | TPRM module on a suite you may already own | TPRM module · commercial · same suite as privacy |
| UpGuard | Outside scan plus vendor questionnaires | Scan plus questionnaire · commercial · stay in scope |
SecurityScorecard
Best for outside-in grade on a vendor you already contract
SecurityScorecard sells letter grades from outside signals. Useful as a queue, not as a pentest.
A stale grade is a reason to reopen the questionnaire. It is not a finding in their SIEM. Easy to fetishize the letter.
Key features
- Ratings they sell
- Portfolio view
- Alerts
- Commercial
Why we like it
A letter you can sort is a conversation starter. It is not access.
Limits
Outside-in. Easy to fetishize the letter.
BitSight
Best for the other known security rating
BitSight is the other rating procurement already wrote. Same job family as SecurityScorecard. Overlap declared.
List both so we are not a one-logo ratings page. A rating is not a SOC 2. Do not treat it as access.
Key features
- Ratings they sell
- Third-party monitor
- Enterprise motion
- Commercial
Why we like it
The other known rating keeps this page from becoming a single-vendor recap.
Limits
Commercial. A rating is not a SOC 2. Do not treat it as access.
Whistic
Best for questionnaire exchange vendors will actually finish
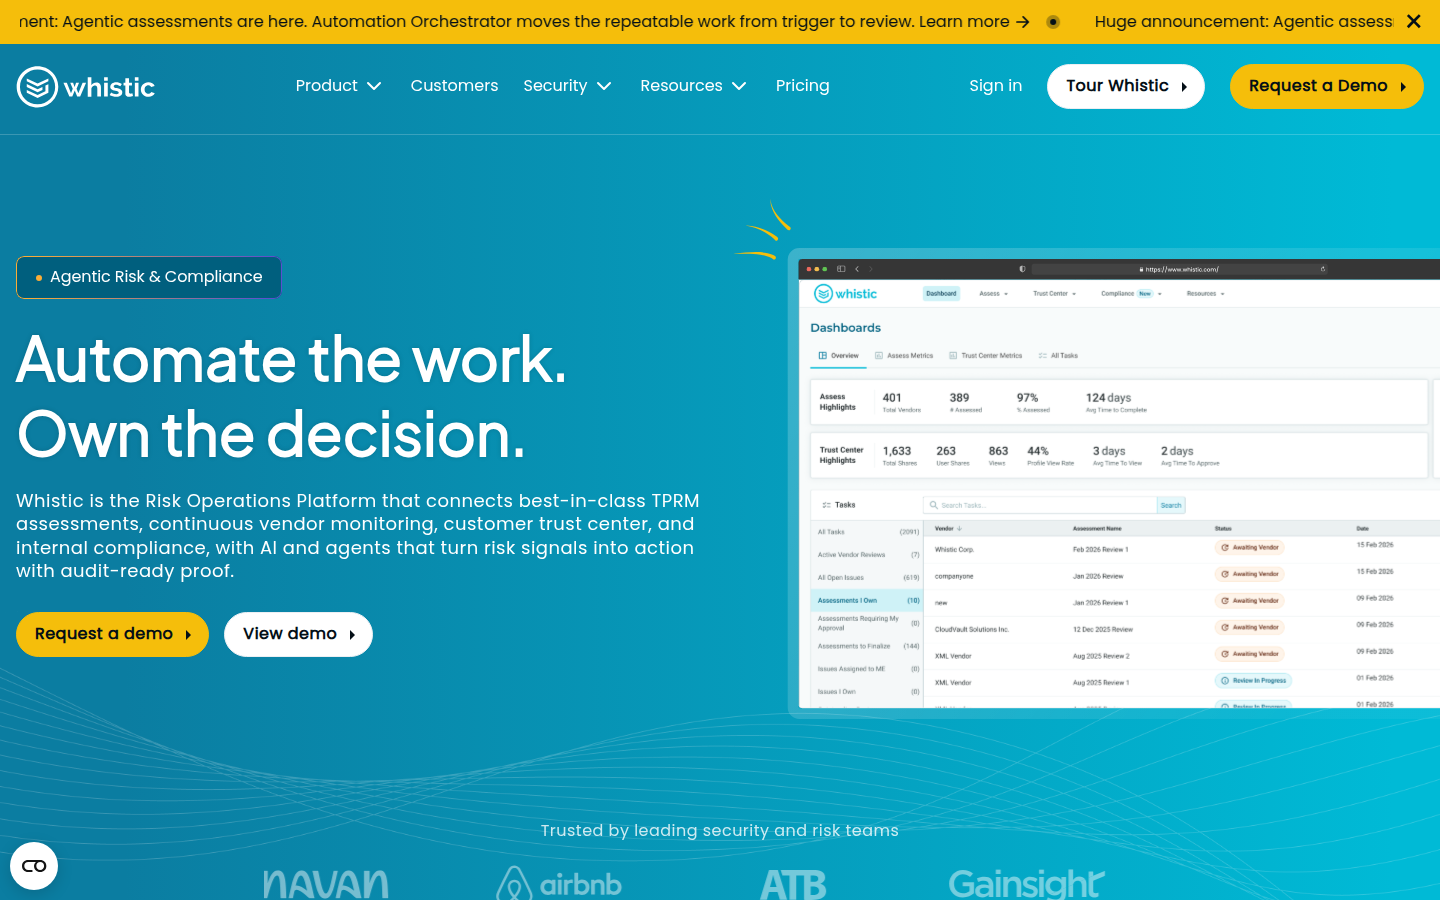
Whistic is a request-and-respond desk for security questionnaires. The artifact is a completed packet, not a grade.
When the hole is a spreadsheet in legal’s inbox, an exchange vendors will finish is the job. A finished packet can still be a lie. You still read it.
Key features
- Questionnaire exchange
- Vendor profiles they sell
- Workflow
- Commercial
Why we like it
A packet vendors will actually complete beats a spreadsheet nobody can find.
Limits
Commercial. A finished packet can still be a lie. You still read it.
ProcessUnity
Best for TPRM workflow on a GRC desk you staff
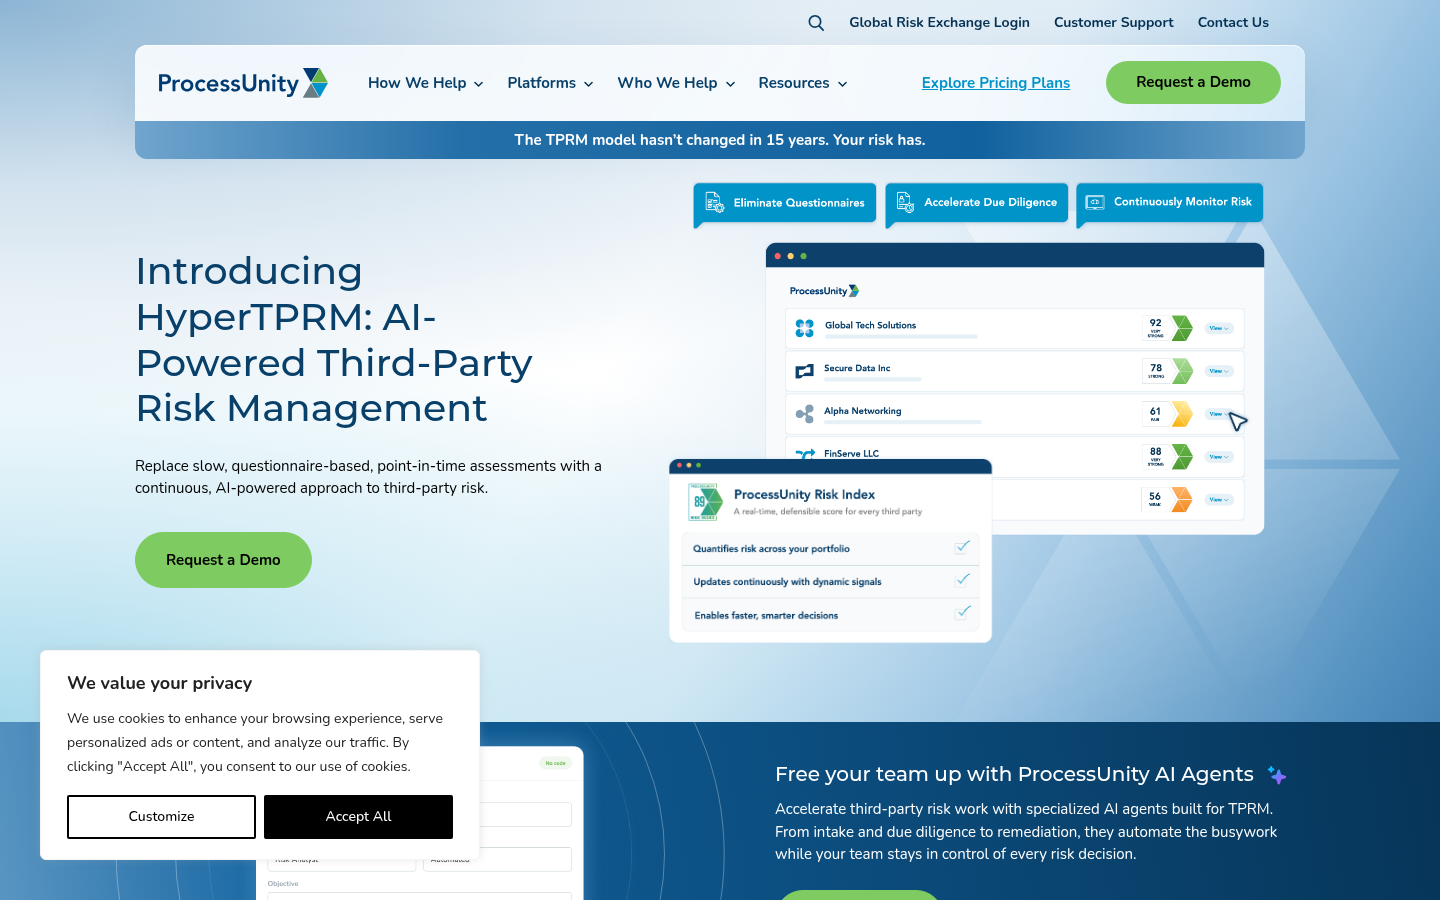
ProcessUnity sells third-party risk workflow. Assessments, issues, a queue. Heavier than a rating widget.
When vendor risk is a program, not a PDF, you need a queue. Implementation time is the catch.
Key features
- Assessment workflow
- Issue tracking
- Enterprise TPRM
- Commercial
Why we like it
A program needs issues and owners, not only a letter.
Limits
Commercial. Implementation time.
OneTrust
Best for TPRM module on a suite you may already own
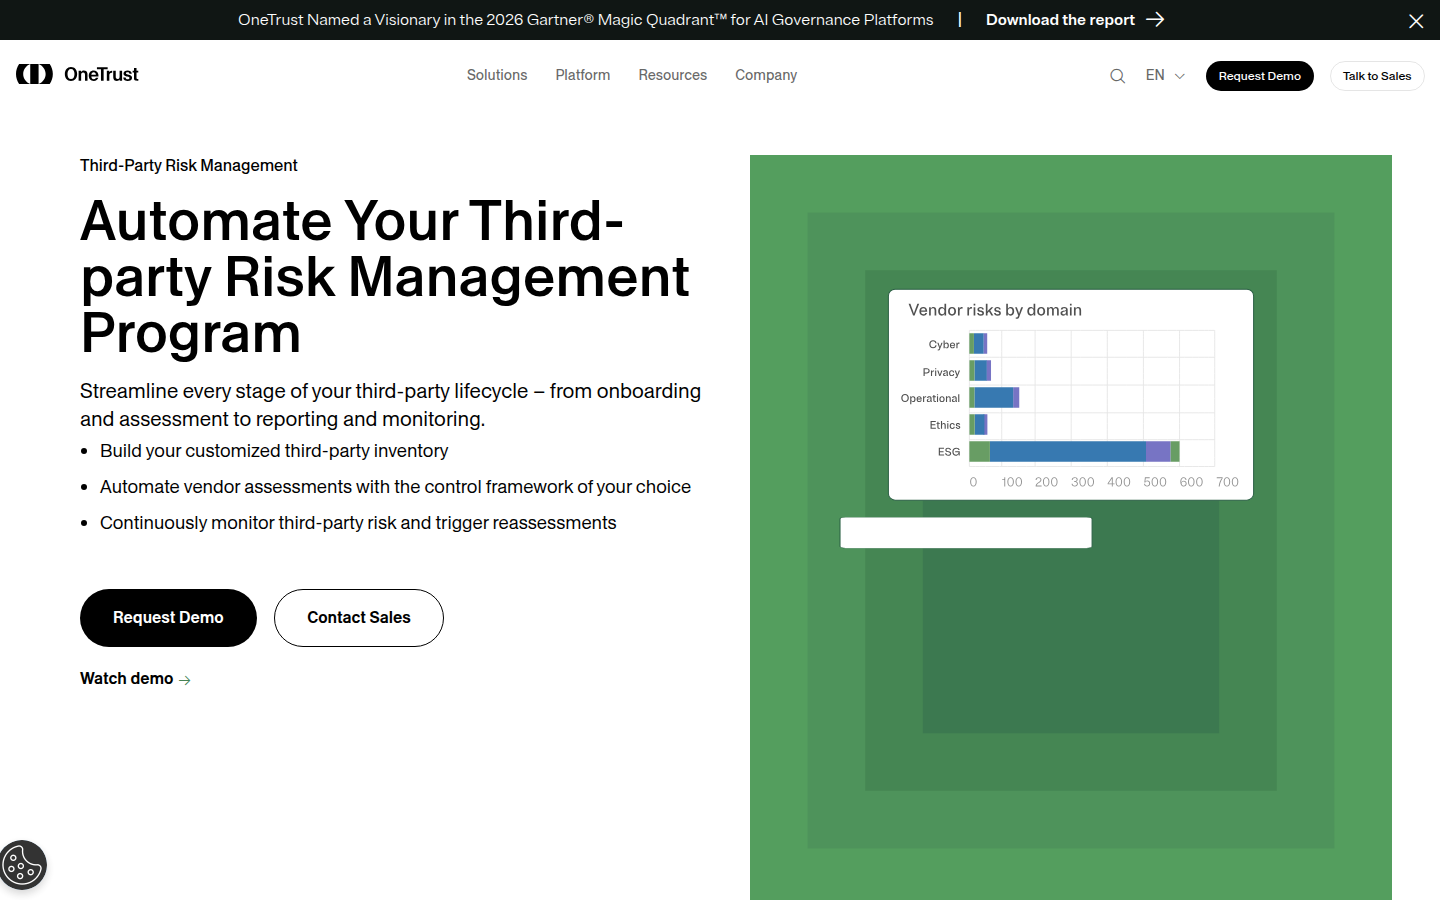
OneTrust includes third-party risk next to privacy modules. Overlap with the consent list is declared. Do not buy it twice.
If the suite is already there, start with the module. A module is not a rating feed unless you add one. Suite gravity is the catch.
Key features
- TPRM they sell
- Same suite as privacy
- Workflow
- Commercial
Why we like it
Honesty. The suite you already pay for is the first TPRM desk.
Limits
Suite gravity. Commercial. A module is not a rating feed unless you add one.
UpGuard
Best for outside scan plus vendor questionnaires
UpGuard mixes attack-surface style scans with vendor workflows. Overlap with ASM is declared. Only scan what you have permission to see.
When someone wants one vendor for grade and packet, this is that pick. Outside scans are not a pentest. Stay in scope.
Key features
- Vendor scores they sell
- Questionnaires
- Breach monitor stories
- Commercial
Why we like it
Grade and packet in one desk is useful when two vendors were the reason nothing shipped.
Limits
Commercial. Outside scans are not a pentest. Stay in scope.
What we left out
- ServiceNow Vendor Risk Management. Large shops already file vendor work on the ITSM they pay for. Public pricing is quote-only and ServiceNow is the TPRM desk, not an ITSM bake-off.
- Prevalent. People want another questionnaire exchange vendors will finish. Whistic and ProcessUnity already cover that job on this page.
Questions before you buy
If procurement cannot get written answers, you are still buying a brochure.
- Can I see which vendor questionnaire is stale without opening a spreadsheet?
- Are we buying a letter grade, a completed packet, or a suite module we already pay for?
- Do we have written permission if anyone wants to scan the vendor’s perimeter?
Read the answers. A grade is not a control.
FAQs
Does a rating replace a SOC 2?
No. A rating is outside-in. A report is a point in time. Read both.
Can I scan a vendor’s perimeter?
Only with written permission. This page is desks, not a scan cookbook.
OneTrust or a specialist?
Suite if you already pay for it. Specialist if the queue is the only job.
Is this a scored bake-off?
No.

