Best Autonomous Pentesting Tools in 2026: AI Agents That Prove Exploit Paths
Five tools that attack your own environment on a schedule, prove what is exploitable, and retest the fix.
AWS Marketplace lists a 12-month Pentera contract at USD 120,000. Teams pay that because a yearly manual pentest goes stale fast: the environment changes every week, and the report describes a network that no longer exists.
These tools run attacks against your own systems with an agent instead of a consultant, chain weaknesses into attack paths, prove exploitability, and retest after a fix. Pentera and Horizon3.ai’s NodeZero built the category on internal network testing. XBOW focuses on web applications and APIs. Strix is the open source option. A Security, out of stealth since June 2026, sells one loop from finding to fix.
A Security is listed last: its capabilities are launch claims, stated rather than independently demonstrated, while XBOW at least has a public HackerOne ranking and Pentera and NodeZero publish prices and deployment models.
How we evaluated
We read each vendor’s product pages, marketplace listings, repositories, and public documentation on 14 Oct 2026, and checked each one against the same questions: which attack surfaces it tests, whether it proves exploitability with evidence, how a human approves or scopes a run, whether it retests fixes, and how it is priced. Where public material does not cover a question, we write “not documented”.
| Tool | Best for | What to check |
|---|---|---|
| Pentera | Internal, external, and cloud validation with remediation orchestration | USD 120,000 per 12 months on AWS |
| Horizon3.ai NodeZero | Internal and external autonomous pentests with fix verification | From USD 25,000 per 12 months, 500 assets |
| XBOW | Web app and API exploitation with proof per finding | Quote |
| Strix | Open source AI pentesting agents for apps and CI | Apache-2.0 · free |
| A Security | One loop: find, prove, chain, fix, and retest across apps and infrastructure | Launched Jun 2026 · quote |
Pentera
NodeZero
XBOW
Strix
A Security
Capability comparison: safety, proof, deployment, retesting
These are the 5 rows that decide whether an autonomous pentest is safe to run in production and whether its findings can be trusted.
| Pentera | NodeZero | XBOW | Strix | A Security | |
|---|---|---|---|---|---|
| Testing safety | Controlled runs, every action logged | Safely exploits, no agents installed | not documented | Runs your code dynamically; scope is yours to set | Attack plan reviewed and approved before anything runs |
| Exploit verification | Audit proof per exploit | Exploits chained attack paths and shows proof | Proves exploitability before a finding reaches the team | Validates with proofs of concept | Proves exploitability per finding, per vendor launch material |
| False positives | Findings are validated exploits, not scanner scores | Findings are validated exploits | not documented; proof-first design is meant to filter them | One public user report says runs did not complete | not documented |
| Deployment | Core, Surface, and Cloud products | Free Docker host or OVA internal; Horizon3.ai cloud for external | Point at a URL, SaaS | CLI and GitHub Actions; Strix Cloud sold separately | not documented |
| Retesting | Resolve orchestrates remediation of validated findings | Quick Verify reruns the relevant path after a fix | not documented | Reruns on each pull request via GitHub Actions | Validates closure after remediation, per vendor |
Cells summarize each vendor’s public documentation as cited in its entry below. Vendor wording is not independent testing.
Autonomous pentesting is not the same as continuous validation
Autonomous pentesting behaves like an attacker: it discovers, exploits, and chains real weaknesses in your environment, and the output is a proven attack path. NodeZero, XBOW, and Strix sit here.
Continuous validation is the broader program: test on a schedule, prove which exposures are exploitable, check that controls keep working after every change, and confirm fixes. Pentera frames itself this way. It calls its platform “exposure validation” and says it “includes autonomous penetration testing, but it operates differently from traditional pentests” (Pentera). A Security’s find-fix-retest loop also leans toward validation.
Buy pentesting when you need proof of exploitable paths. Buy validation when you need ongoing evidence that exposures are closed and controls hold. Many teams need both.
Pentera
Best for enterprise exposure validation across internal, external, and cloud
Pentera splits validation into products: Core for internal networks, Surface for the external attack surface, and Cloud for cloud identity and hybrid environments. Resolve orchestrates remediation of validated findings, and web app and API testing are newer AI-native use cases.
Runs are controlled and logged, with audit proof for each exploit.
Key features:
- Core, Surface, and Cloud validation
- Resolve remediation orchestration
- Controlled execution with audit proof
- SECTOR11 adversarial testing services
Why we like it:
Core, Surface, and Cloud validate internal, external, and cloud exposure with audit proof per exploit, so one contract shows which findings are actually exploitable.
Limits:
Priced for enterprises. Module scope is set in private offers.
License or pricing: AWS Marketplace lists USD 120,000 for a 12-month contract, with scope set in a private offer.
Horizon3.ai NodeZero
Best for frequent internal pentests with published pricing
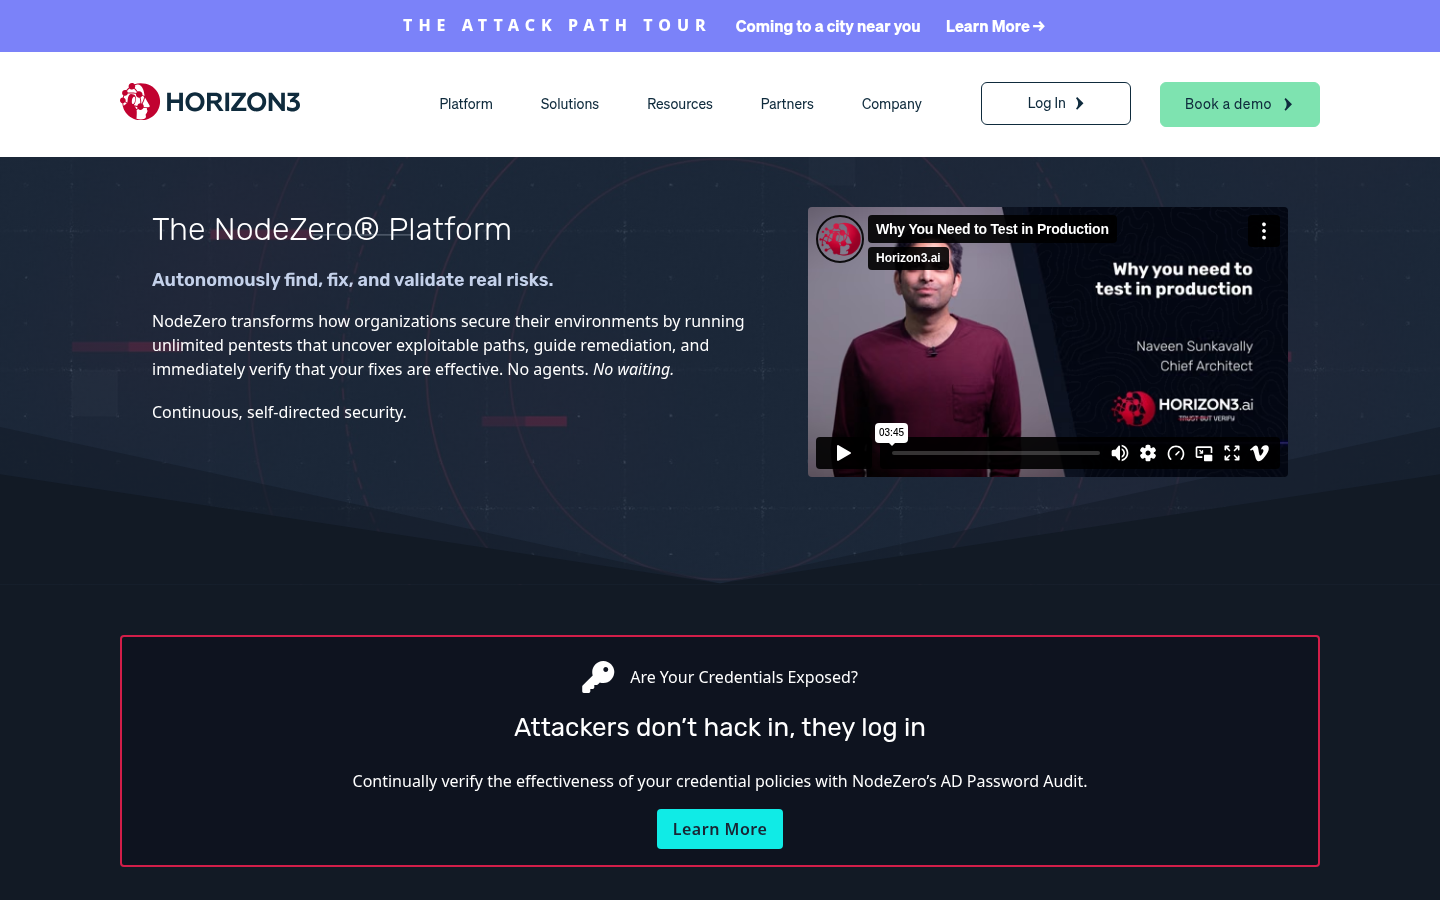
NodeZero runs internal pentests from a free Docker host or OVA, and external tests from the Horizon3.ai cloud, with no agents installed. It chains credentials, misconfigurations, and weak policies into attack paths, safely exploits them, and shows progress in real time.
After a fix, Quick Verify reruns the relevant path. It also runs AD password audits.
Key features:
- Internal and external pentests, schedulable daily
- No installed agents
- Fix guidance and Quick Verify
- AD password audit
Why we like it:
It is the easiest to price and schedule, and the fix-verify loop is mature.
Limits:
Its strength is networks and identity. Deep web application testing is not its focus.
License or pricing: AWS Marketplace, 12 months for 500 assets: Core USD 25,000, Pro USD 32,500, Elite USD 42,500.
XBOW
Best for continuous web app and API exploitation with proof
XBOW points at a URL, explores applications and APIs like an attacker, chains vulnerabilities, and proves exploitability before a finding reaches the team. In June 2025 it became the first autonomous system to rank #1 on HackerOne.
XBOW says it has found more than 14,000 zero-days in customer applications and serves 150+ security teams. Those are vendor figures.
Key features:
- Autonomous web and API testing
- Chained attack paths with working exploits
- Scoped runs with full action logs
- Developer-ready remediation per finding
Why we like it:
It chains web and API vulnerabilities and proves exploitability before a finding reaches the team, which cuts triage of unexploitable scanner noise.
Limits:
Internal network and Active Directory testing are not its focus.
License or pricing: Quote. AWS Marketplace lists a USD 50,000 12-month Attack Credit package.
Strix
Best free option for developers testing their own apps
Strix runs teams of AI agents that execute your code dynamically, find vulnerabilities, and validate them with proofs of concept. It ships as a developer CLI and integrates with GitHub Actions to test each pull request.
Strix Cloud and an Enterprise edition are sold separately.
Key features:
- Multi-agent orchestration
- Proof-of-concept validation
- CI and pull request integration
- Auto-fix suggestions and reports
Why we like it:
No license cost, and it fits into CI where developers already work.
Limits:
Results depend on the model and token budget you supply. At least one public user report says runs did not complete.
License or pricing: Free and open source under Apache-2.0. Strix Cloud and Enterprise are commercial.
A Security
Best for one continuous loop from exploit to verified fix
A Security came out of stealth in June 2026 with agents that find exposure, prove exploitability, chain attack paths across web, AI, network, and infrastructure, remediate at the source or in compensating controls, and validate closure.
It builds a prioritized attack plan that the team reviews and approves before anything runs, logs every move, and pushes fixes through ITSM.
Key features:
- Approved attack plans before execution
- Attack chains across web, AI, network, and infrastructure
- Remediation and retest through ITSM
- Full logging of every action
Why we like it:
It treats remediation as part of the test, which is where most pentest programs stall.
Limits:
Launch-stage. Supported environments and customer references are not documented.
License or pricing: Commercial. No public pricing.
How to choose an autonomous pentesting tool
- Map the surface you need tested. Internal network and AD point to Pentera or NodeZero. Web apps and APIs point to XBOW or Strix.
- Ask for a sample finding. Look for a working exploit, the full path, and the fix guidance.
- Check safety controls. Confirm scoping, approval, and logging before any run in production.
- Price per asset or per credit. Compare the AWS Marketplace listings against your asset count.
What we left out
- Breach and attack simulation tools, which test controls rather than exploit paths. See Pentera vs SafeBreach.
- Shannon: another open source AI pentester, left out to keep one open source pick.
- Armadin: another AI offensive security option. See XBOW vs Armadin.
What the internet thinks about autonomous pentesting
Live threads, quoted for the argument, not the score.
Hacker News · April 2026
“As far as black-box testing, I haven’t seen anything that impressive yet.”
From a researcher who has tested AI pentesting agents. Vendors reply that black-box results improve with context, which is why XBOW and A Security ask for more than a URL.
Hacker News · May 2026
“Tried a bunch of open source pentesters, including strix (though we never managed to get strix to actually complete.)”
The same commenter said another open source tool beat a USD 10K pentest in a white-box test. The lesson either way: pilot on your own app before trusting anyone’s benchmark.
Choose Pentera for enterprise exposure validation across internal, external, and cloud. Choose NodeZero for frequent internal pentests at a published price. Choose XBOW for web apps and APIs. Choose Strix to test your own apps for free in CI. Choose A Security when you want one loop from exploit to verified fix and can pilot a launch-stage vendor first.
FAQs
What is autonomous pentesting?
Software agents that attack your own systems, chain weaknesses into attack paths, prove exploitability, and retest after fixes, without a human tester driving each step.
Does autonomous pentesting replace manual pentests?
Not fully. It covers breadth and frequency. Many compliance programs still expect a human-led test.
Is there a free autonomous pentesting tool?
Strix is free under Apache-2.0. You supply the model and compute.