Network Security
Best NDR Tools for Network Detection and Response in 2026
EDR quiet does not mean the lateral move was invisible.
Endpoint agents can stay green for 8 hours while credential abuse and living-off-the-land traffic move east-west. Network Detection and Response watches packet and flow evidence to catch what EDR never saw.
ExtraHop RevealX and peers split hard: deep protocol forensics, attack-signal prioritization, autonomous behavioral response, open Zeek evidence, and NetFlow-led enterprise monitoring.
If the edge is the product, see SSE tools. For identity-aware access paths, use ZTNA tools.
How we evaluated
We read first-party NDR, RevealX, Open NDR, and Zeek pages on 19 Sep 2026. We asked whether detection uses packets or metadata, whether investigation evidence is first-class, whether response is autonomous or analyst-led, and whether an open path exists. Decrypt and throughput claims are vendor claims.
| Tool | Best for | What to check |
|---|---|---|
| ExtraHop RevealX | Packet-depth NDR and protocol forensics | Commercial · decrypt focus |
| Vectra AI | Attack-signal prioritization for SOC | Commercial · hybrid coverage |
| Darktrace / NETWORK | Self-learning detection and autonomous response | Commercial · Antigena path |
| Corelight Open NDR | Zeek-based open network evidence | Commercial · open core |
| Cisco Secure Network Analytics | NetFlow-led enterprise NDR | Commercial · Cisco estate |
| Zeek | Open network evidence framework | Open source · you operate |
ExtraHop RevealX
Best for packet-level protocol forensics and decrypt-heavy NDR
ExtraHop RevealX centers immutable packet insights, broad protocol decoding, and decryption options they document for hybrid networks.
Choose it when investigation depth and protocol clarity beat metadata-only NDR.
Key features:
- Packet-level visibility and forensics
- Decryption and protocol decoding they advertise
- Behavioral detections on network activity
- Hybrid and multi-cloud network coverage packaging
Why we like it:
SOCs that live in packet investigations get evidence EDR tickets never carry.
Limits:
Commercial and appliance or SaaS sizing matters. Decrypt programs need clear legal and performance design.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
Vectra AI
Best for attacker-behavior signal prioritization
Vectra AI emphasizes Attack Signal Intelligence: fewer, higher-confidence detections mapped to attacker behaviors across network and identity context.
Pick it when SOC noise, not packet forensics, is the weekly pain.
Key features:
- Behavioral attack detections
- Identity and network correlation they publish
- MITRE-oriented investigation views
- Hybrid network and cloud packaging
Why we like it:
Alert-fatigued SOCs get prioritized attacker narratives instead of raw anomaly floods.
Limits:
Commercial. Packet retention depth may trail ExtraHop-style forensics.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
Darktrace / NETWORK
Best for self-learning behavioral detection and autonomous response
Darktrace / NETWORK uses self-learning behavioral models and Cyber AI Analyst narratives, with Antigena autonomous response options they document.
Choose it when machine-speed containment is the buyer thesis.
Key features:
- Self-learning behavioral detection
- Cyber AI Analyst investigation narratives
- Autonomous response actions they list
- Network and hybrid coverage packaging
Why we like it:
Teams that want autonomous containment get a product built around that operating model.
Limits:
Commercial. Autonomous actions need careful change control. Confirm false-positive handling in PoC.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
Corelight Open NDR
Best for Zeek-based open network evidence at enterprise scale
Corelight Open NDR builds on Zeek, Suricata, and related open sensors to deliver structured network evidence for detection engineering and hunting.
It fits teams that want open evidence formats with commercial platform packaging.
Key features:
- Zeek-centric network evidence
- Suricata and Smart PCAP options they publish
- Open ecosystem integrations
- Detection engineering oriented workflows
Why we like it:
Detection engineers who already think in Zeek logs get an enterprise path without abandoning open evidence.
Limits:
Commercial appliances or cloud packaging. You still staff detection content.
License or pricing: Commercial. Sales-quoted. Checked 19 Sep 2026.
Cisco Secure Network Analytics
Best for NetFlow-led enterprise NDR in Cisco estates
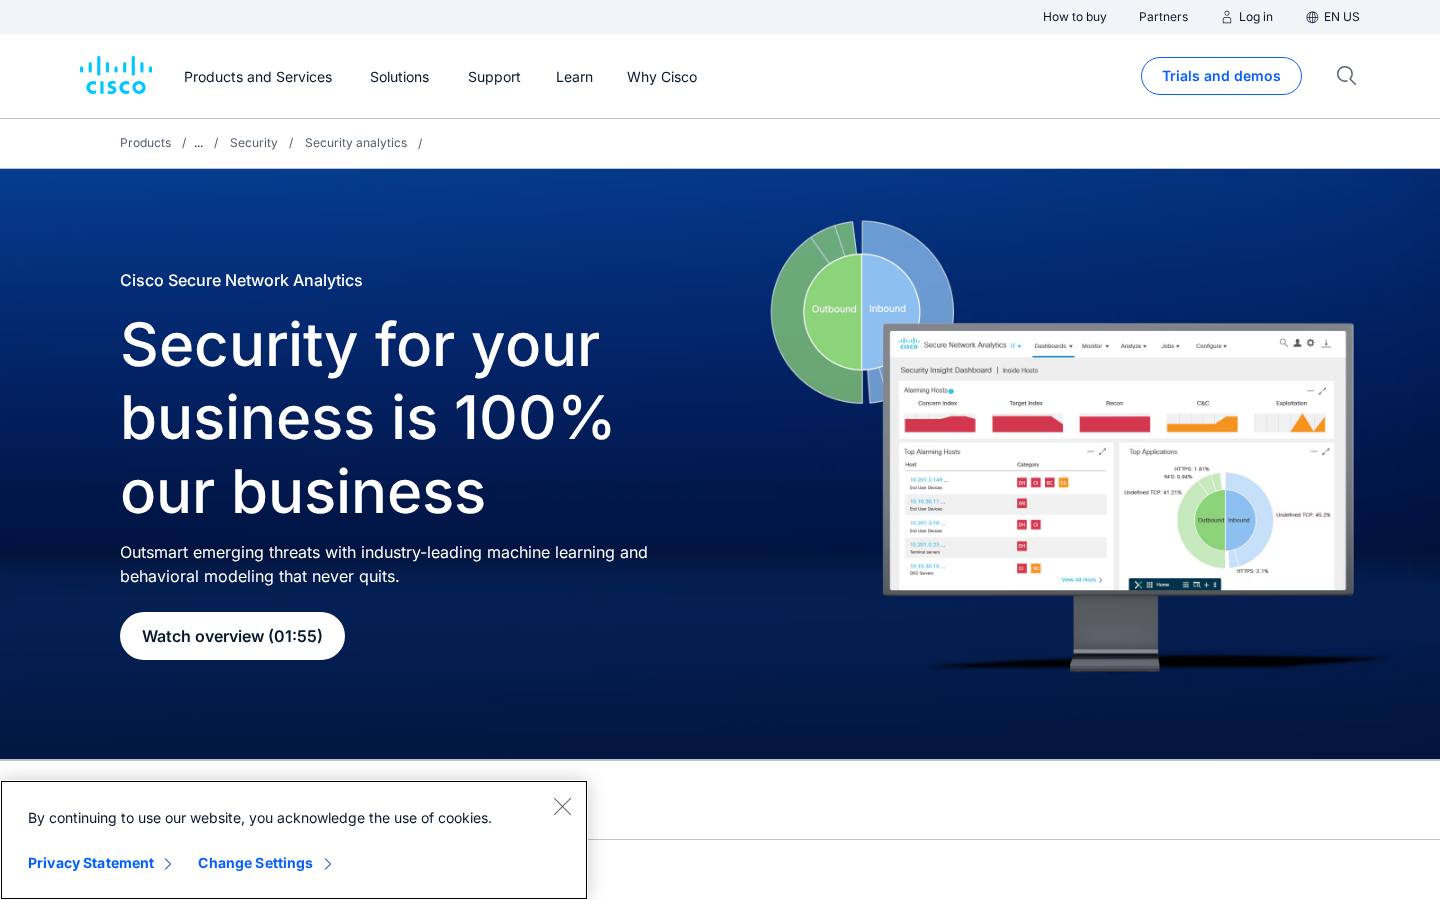
Cisco Secure Network Analytics (Stealthwatch lineage) emphasizes NetFlow and telemetry-driven behavioral analytics for enterprise networks already deep in Cisco infrastructure.
Pick it when flow telemetry is abundant and full packet capture is selectively applied.
Key features:
- NetFlow and telemetry analytics
- Behavioral detections on enterprise traffic
- Cisco ecosystem integrations
- Enterprise scale packaging
Why we like it:
Cisco-heavy networks get NDR without inventing a second telemetry fabric.
Limits:
Commercial and Cisco-centric. Packet forensics depth may need companions.
License or pricing: Commercial. Cisco packaging; confirm on 19 Sep 2026.
Zeek
Best open network analysis framework you operate
Zeek is the open-source network analysis framework formerly known as Bro, producing rich structured logs for detection engineering and hunting.
It is open evidence infrastructure, not a managed NDR SaaS. Corelight and others commercialize around it.
Key features:
- Open network analysis framework
- Rich protocol logs and scripting
- Community and research ecosystem
- Integrations into SIEM and data lakes
Why we like it:
Teams that need portable network evidence keep Zeek even after buying commercial NDR.
Limits:
You operate sensors, storage, and content. No turnkey SOC console by itself.
License or pricing: Open source. Confirm license on 19 Sep 2026.
How to choose an NDR tool
Four questions before the quote. Names are the shortlist, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Do investigations need full packets? | Metadata cannot reconstruct every payload fight. | ExtraHop or Corelight packet paths. | NetFlow-only when forensics is the KPI. |
| Is alert volume the crisis? | Signal quality beats more sensors. | Vectra-style prioritization. | Buying autonomy without tuning owners. |
| Do you want autonomous containment? | Response policy is political. | Darktrace Antigena with change control. | No rollback plan for false containment. |
| Can you run open evidence first? | Cheap truth before enterprise NDR. | Zeek under change control; Corelight if you need support. | Skipping logs then blaming the platform. |
What practitioners argue about NDR
Threads are about evidence formats and operational ownership, not logo heat maps.
Hacker News
“my search yielded this which seems relevant (to the network monitoring tool once named Bro, now Zeek)”
Dec 2025 comment (linked in the Corelight entry). Zeek evidence still anchors serious network detection talk.
ExtraHop
“Expose threat actors and accelerate your response workflows with immutable, packet-level insights.”
ExtraHop RevealX product framing (same ExtraHop security URL linked in the opener). Packet evidence is the ExtraHop thesis.
If the edge fabric is the gap, read SSE tools. For remote access paths, use ZTNA tools.
FAQs
Is NDR a replacement for EDR?
No. EDR watches endpoints. NDR watches network conversations. Mature SOCs correlate both.
Do I need full packet capture for NDR?
Not always. Metadata and behavioral NDR cover many detections. Packet capture still matters for deep forensics.
Can Zeek replace a commercial NDR platform?
Zeek provides evidence and scripting. It does not replace enterprise investigation UX, support, or managed response packaging by itself.
Is this a scored bake-off?
No. Order is editorial.