Network Security
Best SSE Tools for Security Service Edge in 2026
ZTNA can be green while SaaS uploads still skip every inspection point.
Private-app ZTNA can show healthy sessions for 100% of contractors while a managed laptop still reaches Salesforce and ChatGPT on a split-tunnel path that never hits a Secure Web Gateway. The access tile is green. The data path is not.
CISA’s June 2024 joint guide on modern network access documented over 22 Known Exploited Vulnerabilities tied to VPN compromise and urged organizations to move toward Secure Service Edge controls: cloud SWG, CASB, ZTNA, and related services instead of a flat remote network.
Security Service Edge packs SWG, CASB, and ZTNA onto one cloud policy plane so internet and SaaS traffic get inspection, not only private apps. Some products stay security-edge focused. Others fold SD-WAN into a full SASE fabric. Browser-first controls sit on a different shortlist.
If you only need private-app access, start with ZTNA tools. If the gap is last-mile browser DLP or remote isolation, see enterprise browsers.
How we evaluated
We read first-party SSE and SASE product pages, plan pages, and public licenses on 19 Sep 2026. We asked whether SWG, CASB, and ZTNA are named products on one plane, whether data inspection (DLP / CASB API or inline) is first-class or bolted on, whether the vendor sells security-edge SSE or converged SASE with SD-WAN, and whether pricing is public. Marketing pages are claims, not a lab bake-off.
| Tool | Best for | What to check |
|---|---|---|
| Cloudflare One | Edge SWG + ZTNA with public plans | Commercial · Free tier to 50 users |
| Netskope One SSE | CASB and data-centric SSE | Commercial · NewEdge network |
| Zscaler Zero Trust Exchange | Proxy SWG + ZTNA at scale | Commercial · ZIA / ZPA packaging |
| Prisma Access | Palo Alto SSE inside SASE | Commercial · threat stack adjacency |
| Skyhigh Security SSE | Focused SWG / CASB / ZTNA | Commercial · non-mega SSE specialist |
| Cato Networks | Converged SASE with SSE jobs | Commercial · SD-WAN included |
Cloudflare One
Best for edge SWG and ZTNA with published plans
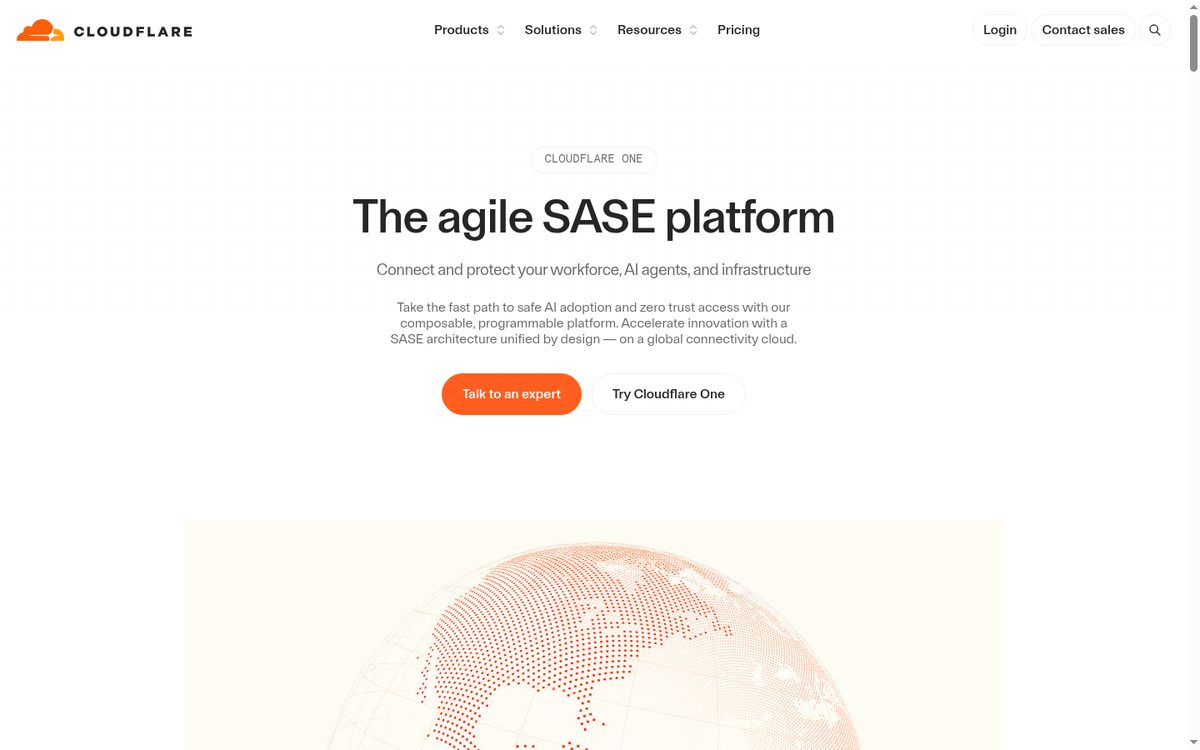
Cloudflare One (Cloudflare’s SASE / Zero Trust pack) puts Access (ZTNA), Gateway (SWG), CASB, DLP, and Browser Isolation on the same connectivity cloud. First-party pages emphasize one control plane for private apps and internet traffic without hairpinning a corporate VPN concentrator.
On this shortlist it is the public-pricing path into SSE-shaped controls. CASB and DLP maturity still trail the data specialists for some estates, so treat it as edge-led SSE, not a Netskope clone.
Key features:
- Gateway SWG with DNS and HTTP filtering on Cloudflare’s edge
- Access ZTNA for private apps without a flat VPN
- CASB and DLP services Cloudflare documents on Zero Trust plans
- Browser Isolation and email security add-ons on the same plane
Why we like it:
When the team wants SWG + ZTNA without a nine-month SASE RFP, Cloudflare’s published Free (up to 50 users) and paid Zero Trust plans on the plans page make a pilot honest.
Limits:
Data security depth and legacy private-app oddities still decide many bake-offs against Netskope or Zscaler. Agent DNS ownership fights are real, as the community note shows.
License or pricing: Commercial Zero Trust / Cloudflare One packages. Free plan covers up to 50 users on Cloudflare’s published Zero Trust plans (checked 19 Sep 2026).
Netskope One SSE
Best for CASB-led data protection inside SSE
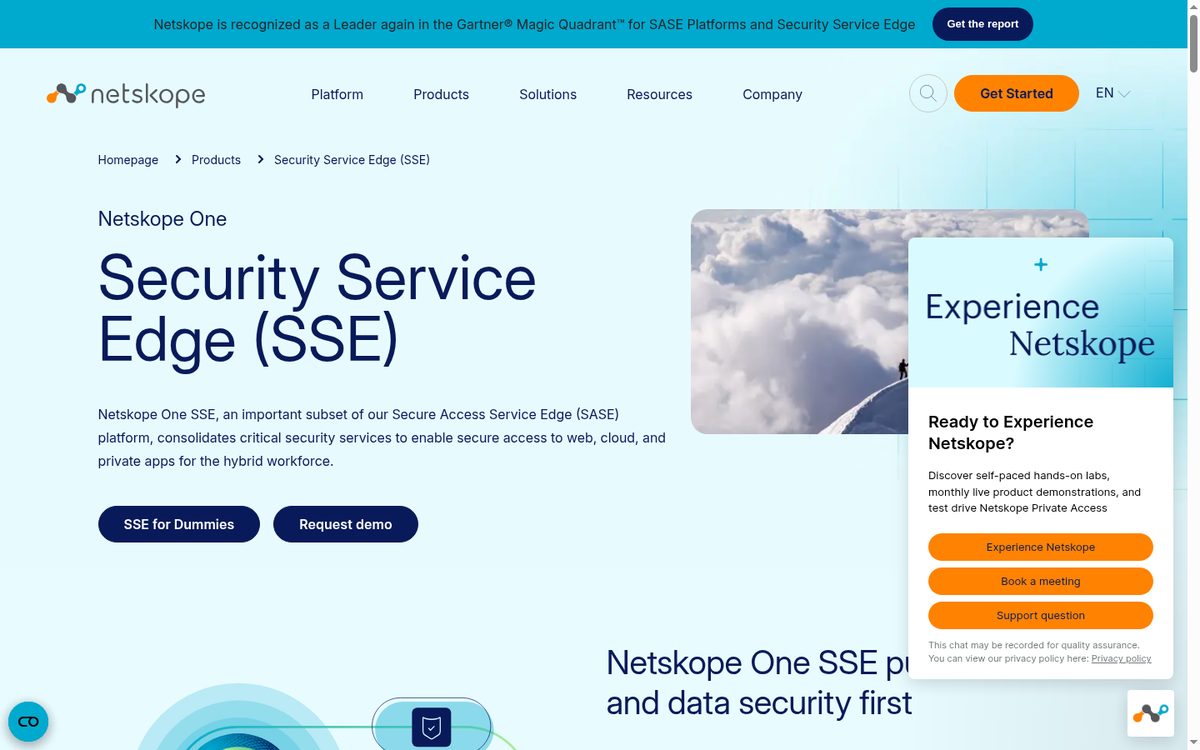
Netskope One SSE centers Next Gen SWG and CASB, then layers Private Access (ZTNA), FWaaS, and RBI on the NewEdge network. First-party copy is explicit that SWG and CASB converge at the core so cloud and web data share one inspection pass.
Choose Netskope when the painful weekly queue is SaaS data movement and shadow apps, not only private-app ZTNA.
Key features:
- Next Gen SWG for web and cloud destinations
- CASB for managed and unmanaged cloud apps
- Private Access ZTNA with endpoint SD-WAN options they document
- Inline DLP and threat inspection across those channels
Why we like it:
If ZTNA already exists and uploads to personal Google Drive still walk out clean, Netskope’s data-first SSE framing matches the miss.
Limits:
Commercial, quote-led. PoC latency and connector scope on your real SaaS set matter more than Magic Quadrant slides.
License or pricing: Commercial. No public per-user list price on 19 Sep 2026.
Zscaler Zero Trust Exchange
Best for large-scale proxy SWG with ZTNA
Zscaler’s Zero Trust Exchange is the cloud proxy fabric behind Zscaler Internet Access (SWG) and Zscaler Private Access (ZTNA), plus data protection services. First-party architecture messaging is direct-to-app, TLS inspection at scale, and no inbound firewall VIP for private apps.
It is the scale SWG + ZTNA reference many enterprises already run. CASB breadth versus Netskope is a PoC question, not a slogan.
Key features:
- ZIA cloud SWG with TLS inspection they document
- ZPA application-level ZTNA without network placement
- Data loss protection across web and cloud channels
- Digital experience monitoring add-ons on the same exchange
Why we like it:
When the estate already thinks in ZIA/ZPA SKUs and needs one proxy policy for internet and private apps, Zscaler owns that operating model.
Limits:
Commercial packaging is modular. Confirm which SSE pieces are on the paper versus logo slides. SSL inspection and app exceptions dominate rollout pain.
License or pricing: Commercial. Quote-only on 19 Sep 2026.
Prisma Access
Best for Palo Alto SSE inside a SASE path
Prisma Access delivers cloud SWG, CASB/enterprise DLP, ZTNA, and FWaaS from Palo Alto’s SASE portfolio. First-party pages position it with Prisma SD-WAN when the program is full SASE, and as the security edge when branches already have networking.
Pick it when WildFire / threat prevention consistency with existing Palo Alto controls matters as much as the SSE checkbox list.
Key features:
- Cloud-delivered SWG and threat prevention
- ZTNA for private applications
- CASB and data security services on the SASE page
- Optional Prisma SD-WAN for converged networking
Why we like it:
Useful when the security org already standardizes on Palo Alto policy objects and wants SSE without a second threat vocabulary.
Limits:
Commercial. Full SASE economics and Strata Cloud Manager roles need a clear RACI so networking and security do not fight the same change window.
License or pricing: Commercial. No public list price on 19 Sep 2026.
Skyhigh Security SSE
Best for a focused SWG / CASB / ZTNA specialist
Skyhigh Security SSE packages Secure Web Gateway, Remote Browser Isolation, Private Access (ZTNA), and CASB on a cloud security service edge. The lineage is McAfee enterprise cloud security; the current brand is a specialist SSE vendor rather than a full connectivity cloud.
It is the non-mega SSE option on this list: honest when you want SWG/CASB depth without buying a global SD-WAN story.
Key features:
- Cloud SWG with threat and data controls they document
- CASB for SaaS visibility and control
- Private Access ZTNA module
- Remote browser isolation option for risky destinations
Why we like it:
When procurement wants an SSE shortlist that is not only the four megaplatform logos, Skyhigh still ships the three core SSE services as the product.
Limits:
Commercial. Validate PoP coverage for your user map and how Private Access compares to a dedicated ZTNA tool on hard protocols.
License or pricing: Commercial. Quote/demo CTAs on 19 Sep 2026.
Cato Networks
Best for converged SASE when WAN and SSE move together
Cato SASE Cloud converges SD-WAN with cloud security services (SWG, CASB, ZTNA, FWaaS, and related controls) on one global private backbone. First-party positioning is a single platform for sites and remote users, not a security-only edge bolted onto someone else’s WAN.
Put Cato on the list when the program is “replace MPLS and the VPN stack,” not when you only need a CASB API connector.
Key features:
- SD-WAN plus security services on one SASE cloud
- SWG, CASB, ZTNA, and FWaaS capabilities they document
- Single management plane for sites and users
- Global private backbone for WAN and security traffic
Why we like it:
Mid-market teams that refuse two vendors for WAN and SSE get a coherent converged path without pretending security-edge SSE is the same project.
Limits:
Commercial. If networking will not move, a security-edge SSE (Cloudflare, Netskope, Zscaler, Skyhigh) is the cleaner scope.
License or pricing: Commercial. No public per-user list on 19 Sep 2026.
How to choose an SSE tool
Four questions before the quote. Names are the shortlist, not a scored bake-off.
| Critical question | Why it matters | What to evaluate | Red flag |
|---|---|---|---|
| Is the failure private-app access or web/SaaS data? | ZTNA-only leaves SWG/CASB gaps. | Netskope, Zscaler, Skyhigh, Cloudflare Gateway for data path; ZTNA shortlist if access only. | Buying ZTNA and calling the VPN program closed. |
| Is SD-WAN in this program? | SASE and SSE are different scopes. | Cato or Prisma when WAN moves; security-edge SSE when networking stays. | A SASE RFP that only prices SWG seats. |
| Do you need public pilot pricing? | Quote fog kills early learning. | Cloudflare Zero Trust published plans for a 50-user trial shape. | Assuming every SSE vendor lists per-user prices. |
| Is the browser the control point? | Enterprise browsers are not SSE. | Island / Prisma Browser / RBI on the browser shortlist. | Replacing SWG with an extension and hoping SaaS API CASB appears. |
What practitioners argue about SSE
Live threads rarely say “Security Service Edge” out loud. They argue about agents fighting over DNS, and about whether replacing VPN without SWG still leaves SaaS wide open.
Hacker News
“Claude Cowork grabs local DNS resolution on macOS which conflicts with secure web gateway aka ZTNA aka SASE products such as Cloudflare Warp which do similar.”
Hacker News comment, March 2026 (same thread cited in the Cloudflare entry). The practical point for SSE buyers: Gateway and ZTNA agents own path and DNS. Anything else that grabs the same resolver will break, including AI desktop tools. Plan the endpoint conflict matrix before the PoC.
CISA joint guide
“CISA has discovered over 22 Known Exploited Vulnerabilities (KEVs) related to VPN compromise, leading to broad access to victim networks.”
Modern Approaches to Network Access Security (June 2024). The guide’s answer is not “more VPN hardening” alone. It walks SWG, CASB, ZTNA, and FWaaS as the SSE-shaped path off flat remote access.
If private apps are the only gap, use ZTNA tools. If the browser is the control you can actually enforce on BYOD, read enterprise browsers.
FAQs
Is SSE the same as SASE?
No. SSE is the security stack (typically SWG, CASB, ZTNA, often FWaaS/DLP). SASE adds networking such as SD-WAN. Cato sells converged SASE; several others can be bought as security-edge SSE.
Does ZTNA replace SSE?
No. ZTNA covers private-app access. SSE adds inspection and control for internet and SaaS data paths. Many ZTNA projects still leave SWG/CASB undone.
Is Cloudflare One an SSE product?
Cloudflare One packages Gateway SWG, Access ZTNA, CASB, DLP, and related services on Cloudflare’s edge. That is SSE-shaped even when Cloudflare markets the broader SASE story.
Is this a scored bake-off?
No. Order is editorial.