Best Workforce Security Platforms in 2026: 6 Tools for Access You Can Revoke
Six tools that show which people and AI agents can reach sensitive data, and that can revoke or restrict that access when it is no longer justified.
When an AI assistant is connected to a shared drive, a permission that has been wrong for 90 days becomes an immediate exposure. Workforce security is the work of knowing which people and AI agents can reach which sensitive data, and of revoking or restricting that access when it is no longer justified.
DSPM inventories sensitive data at rest. Insider risk tools open cases around people and events. SSE and enterprise browsers control the path to the web and SaaS. ISPM and IGA govern identity posture and access requests. Security awareness trains people not to click. None of those, on its own, answers who can reach a given file or dataset, including an AI agent, and whether you can revoke that access.
The six platforms below approach that work from different angles. We start with Varonis, whose product pages document classification, permissions analysis, and automated remediation of overexposed access, including what AI agents can reach. Cymphony, which raised USD 30 million on 9 Sep 2026, is a launch-stage vendor; capabilities below are vendor-stated.
How we evaluated
We read each vendor’s product pages, documentation, and pricing pages on 12 Nov 2026, and checked each one against the same questions: what it shows about who or what can reach sensitive data, whether AI agents are in that view, and what access it can revoke or restrict. Capabilities are vendor-stated unless noted.
| Tool | Best for | What to check |
|---|---|---|
| Varonis | Classify data, analyze permissions, and remediate overexposed access | Quote-based |
| Microsoft Purview | Labels, DLP, and access restriction in Microsoft 365, including Copilot data | USD 12 per user per month, paid yearly |
| Cyberhaven | Lineage and enforcement as data moves across people, agents, and channels | Quote-based |
| Cyera | Identity-to-data view with in-product access revocation | Quote-based |
| Proofpoint | DSPM access governance in a human-security portfolio, including AI-agent exposure | Quote-based |
| Cymphony | Connected view of people, agents, and the data they can reach, with in-product revoke | Quote-based |
Varonis
Purview
Cyberhaven
Cyera
Proofpoint
Cymphony
Capability matrix: who can reach the data, and what you can change
Each cell restates what the vendor documents on the product or documentation pages cited in its entry. Uncited claims are omitted; if a product does not document a capability, the cell says so in a full sentence.
| Varonis | Purview | Cyberhaven | Cyera | Proofpoint | Cymphony | |
|---|---|---|---|---|---|---|
| What it shows about access | Where sensitive data lives, which identities can reach it, and how it is accessed, including a stated view of what AI agents can reach | Who can reach labeled Microsoft 365 content, with suite tools that also cover DLP and insider risk cases | Lineage and identity context as data moves across endpoints, browsers, cloud, and AI workflows | Which identities are breaking access policy on classified data, across the stores Cyera discovers | Users, apps, and AI agents mapped to classified data, as the DSPM product page describes | A connected map of people, AI agents, and machine identities to the data they can reach, as the company describes it |
| What you can revoke or restrict | Automated remediation of overexposed permissions, with dependency checks, simulation, and rollback described in the product FAQ | Restriction or removal of access to labeled content in Microsoft 365, plus DLP policies; Copilot data protection is documented in the Suite | Policy enforcement as data moves; a full, in-product permissions cleanup of the kind Varonis and Cyera document is not the focus of the product page we reviewed | In-product actions to revoke access, remove public or organization-wide sharing, mask data, or apply labels, with previews and audit trails | Remediation described as removing risky shares, reducing permissions, and closing exposure; some Microsoft 365 revoke workflows are documented as beta | In-product actions to revoke access or notify an owner, including remediations the company says can run in parallel |
| AI agents and assistants | A documented workflow that maps what each agent can reach, rightsizes that access, and monitors prompts and data access | Documented protections for Microsoft 365 Copilot data in the Purview Suite | Agentic Data Security as a named part of the Flow platform, covering AI-driven workflows | AI agents are described most clearly on the separate Cyera Identity offering; confirm what the DSPM plan includes | AI data exposure visibility for copilots, GenAI tools, and agents, as the DSPM page describes | AI agents are included in the identity map, and an AI module is described for seeing which AI tools people and agents use and what data they expose |
| Where it runs | A published catalog of data stores, collaboration platforms, and AI tools; core platform versus Atlas, DAM, and Interceptor modules | Microsoft 365 and other Purview-connected locations you license; some non-Microsoft coverage is a separate, sometimes metered, capability | Endpoints, browsers, cloud, and AI workflows, as the Flow product page describes | Cloud, SaaS, and related stores Cyera discovers; Identity is a related product for non-human identities | Cloud services and SaaS applications in Proofpoint DSPM, alongside other Proofpoint channel products you may already run | Agentless ingestion from identity systems and data sources, as Cymphony states it, with no endpoint agent to install |
Worked example: a departed contractor and an AI assistant on an overshared folder
A contractor still has access to a client folder 90 days after the project ended. An AI assistant connected to the same shared drive can read an overshared HR directory. Here is what each product documents that it would show, and what access you could revoke or restrict.
None of the vendors publishes this exact scenario; the cells restate capabilities from the entries below.
| What it would show | What you can change | |
|---|---|---|
| Varonis | The folder as classified data, the contractor and the assistant as identities that can reach it, and the permission paths that expose it | Automated remediation that removes the unnecessary access, with the option to simulate or roll back the change, as the product FAQ describes |
| Microsoft Purview | Labels on the Microsoft 365 content, the people or groups who can reach it, and whether Copilot protection in the Suite applies | Restriction or removal of access to the labeled library, plus DLP policies; the exact Copilot control depends on the Suite capabilities you license |
| Cyberhaven | Lineage showing how the folder’s data moved, and whether the contractor or the assistant used it across endpoints, browsers, or AI workflows | Policy enforcement on that path. A standing permissions cleanup of the contractor’s grant is not the focus of the public product page we reviewed |
| Cyera | The contractor and any other violating identities on the classified files, including inherited access where Cyera documents it | A guarded in-product action that revokes the contractor’s access across the affected files, or removes a public or organization-wide share |
| Proofpoint | The users, apps, and AI agents mapped to the classified data, as DSPM describes that exposure view | Remediation that removes risky shares or reduces permissions. Confirm whether a given Microsoft 365 revoke action is generally available or documented as beta |
| Cymphony | The contractor and the assistant on a connected map of identities and the data they can reach, as the company describes it | An in-product revoke or an owner notice, including remediations the company says can run together from that view |
This is our illustration of a common access-and-revoke day, not a vendor-published walkthrough of this incident.
Varonis
Best for classifying sensitive data, seeing who can reach it, and fixing overexposed permissions, including AI agents
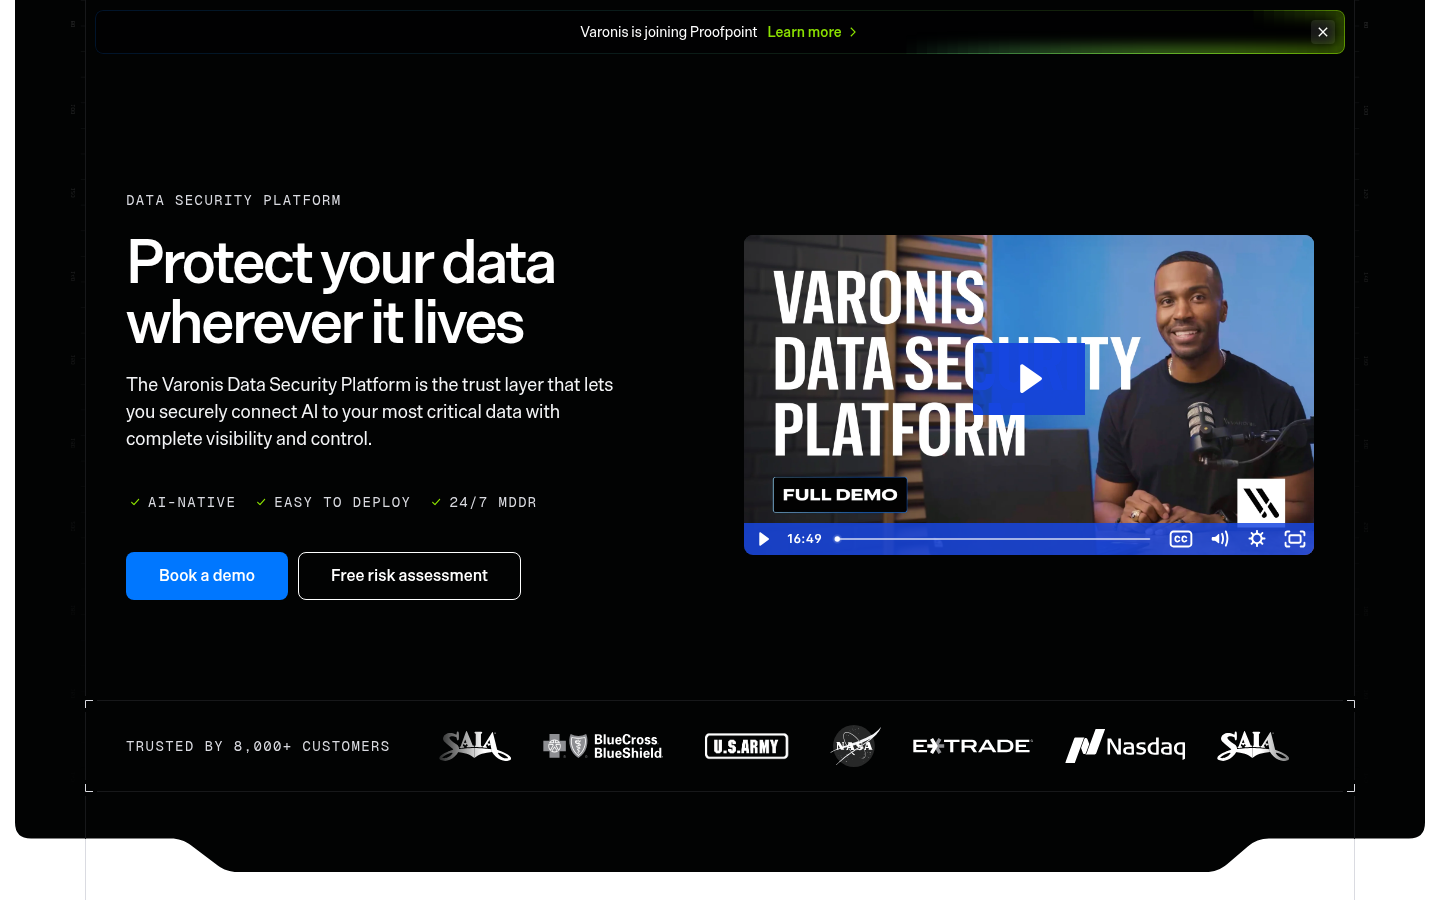
Varonis Data Security Platform is documented as showing where sensitive data lives, which identities can reach it, and how to remove unnecessary access, including a stated workflow that maps what AI agents can reach and rightsizes that access. Automated fixes are described with dependency checks, plus the option to simulate a change or roll it back.
The same product pages describe a 24-hour MDDR service and separate Atlas, DAM, and Interceptor modules that are not part of the core platform. Proofpoint announced an agreement to acquire Varonis on 15 Oct 2026, expected to close in the first half of 2027; both companies say the products remain separate until then. Public list prices with a defined billing unit are not on the Varonis site.
Key features:
- Classification of sensitive data, with permissions analysis for identities and AI agents
- Automated remediation of overexposed access, with simulation and rollback described in the product FAQ
- A searchable activity trail of data access, logins, and permission changes
- Optional MDDR, plus Atlas, DAM, and Interceptor as separate modules
Why we like it:
It ties classified data to the identities that can reach it, then documents an automated way to remove the access that should not be there.
Limits:
Atlas, DAM, and Interceptor are separate modules, and MDDR is an add-on service. Public list prices with a defined billing unit are not on the Varonis site, checked 12 Nov 2026.
License or pricing: Quote-based. Varonis’s public platform pages do not list a USD price with a defined billing unit, checked 12 Nov 2026. A free data risk assessment is offered on the product page.
Microsoft Purview
Best for labeling, restricting, and monitoring access to sensitive data in Microsoft 365, including Copilot
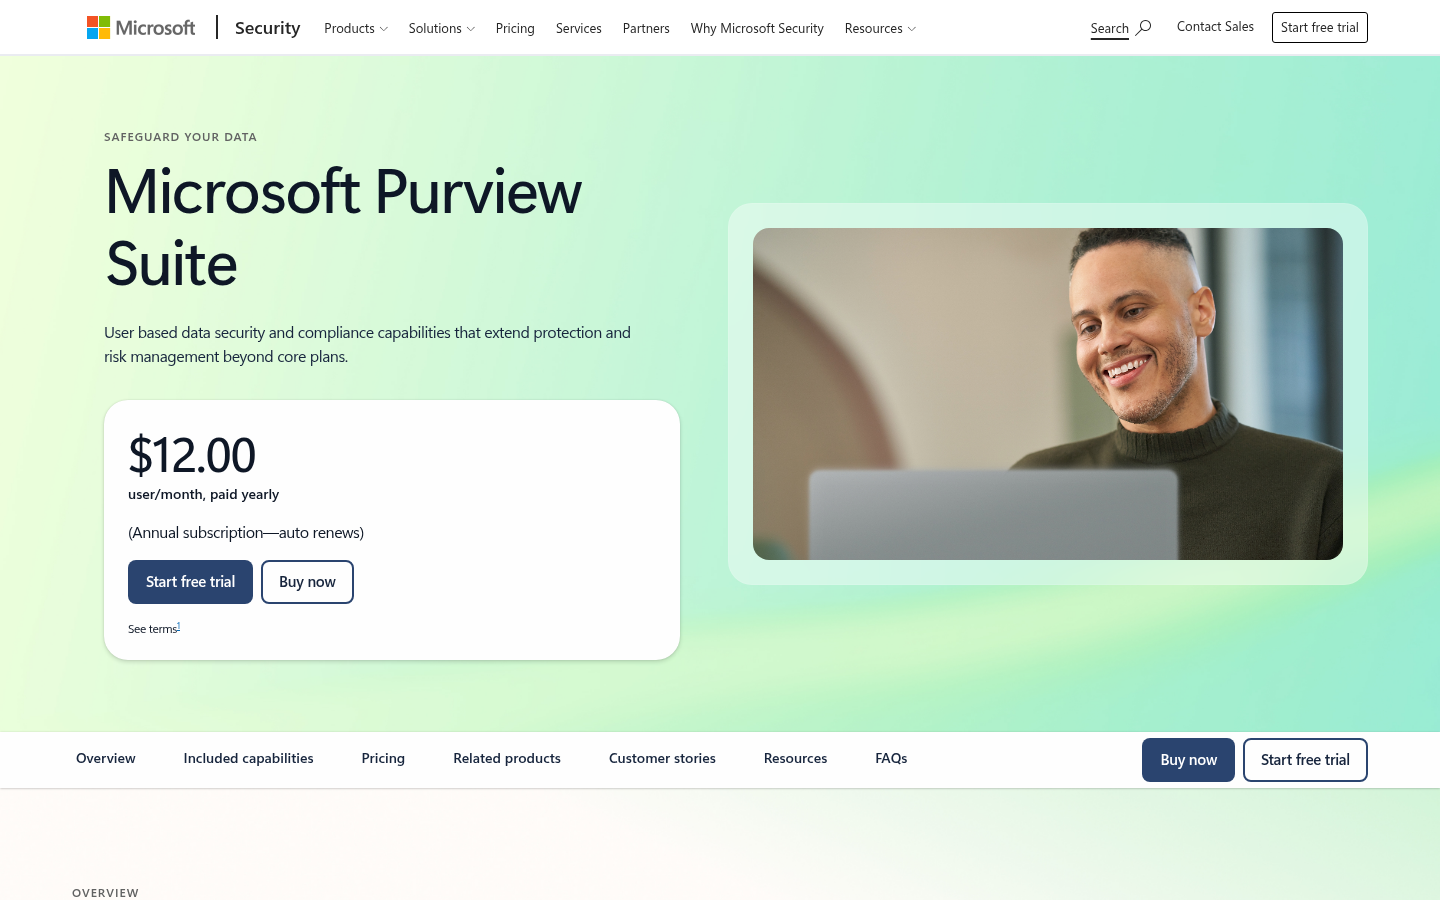
Microsoft Purview Suite is documented as unifying information protection, data loss prevention, insider risk management, and related compliance tools, with protection described for Microsoft 365 Copilot data. The workforce question this page asks is whether you can label sensitive content in Microsoft 365 and then restrict or remove access to it, including when Copilot or another Microsoft assistant can reach that content.
Insider Risk Management, which scores activity and opens cases, is part of the same suite and is covered in more depth on our insider risk page. Public pricing for the Suite is USD 12 per user per month, paid yearly, and requires Microsoft 365 E3, or Office 365 E3 plus Enterprise Mobility and Security E3, checked 12 Nov 2026.
Key features:
- Information protection and sensitivity labels in Microsoft 365
- Data loss prevention across email, files, and apps in the suite
- Documented protections for Microsoft 365 Copilot data
- Insider Risk Management in the same suite, for case-driven review
Why we like it:
It lets you label sensitive Microsoft 365 content and restrict who, or which Copilot experience, can reach it under licenses many teams already buy.
Limits:
The documented control plane is the Microsoft 365 and Purview world you license. Coverage of non-Microsoft stores depends on the Purview capabilities you add, and some of those are metered separately. Insider risk cases are a different workflow from a permissions cleanup on a file share.
License or pricing: Microsoft Purview Suite is USD 12 per user per month, paid yearly, and requires Microsoft 365 E3, or Office 365 E3 plus Enterprise Mobility and Security E3, per Microsoft’s Purview Suite page, checked 12 Nov 2026.
Cyberhaven
Best for tracing sensitive data as people and agents move it, then enforcing policy in that path
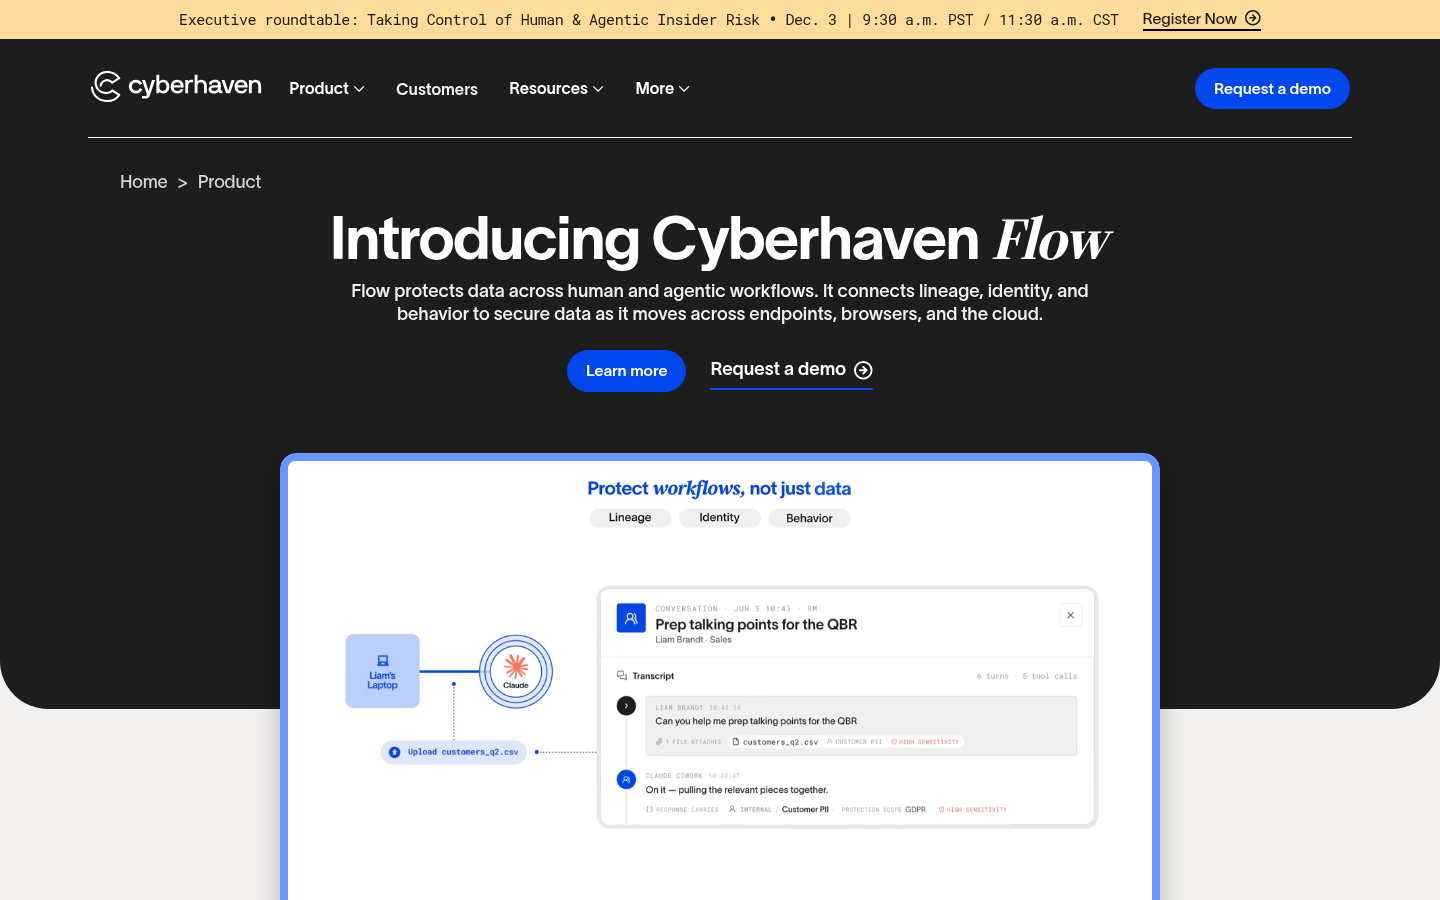
Cyberhaven Flow is documented as connecting lineage, identity, and behavior so protection can follow data as it moves across endpoints, browsers, cloud, and AI workflows. The company groups Agentic Data Security, Human Data Security, and DSPM in one platform, with classification that updates as the data changes and policies that use that context, not only a permissions list after the fact.
That is a different starting point from a data-store access inventory. If your immediate need is to rightsize standing permissions on a file share, confirm how Flow’s remediation compares with a permissions-first product. Pricing is quote-based.
Key features:
- Data lineage across creation, movement, and transformation
- Agentic and human data security, plus DSPM, in one platform
- Policy enforcement as context changes along the data path
- Investigation support described through Linea analyst and detection agents
Why we like it:
It follows sensitive data as people and agents move it, so a policy can land on the path itself rather than only on a static permission.
Limits:
Public pages emphasize lineage and enforcement on the move. A full, in-product permissions cleanup of the kind Varonis and Cyera document is not the focus of the product page we reviewed. Pricing is quote-based.
License or pricing: Quote-based. Cyberhaven’s public product pages do not list a USD price, checked 12 Nov 2026.
Cyera
Best for tying classified data to the identities that can reach it, then revoking that access in the product
Cyera’s remediation pages document a view of which identities are breaking access policy on classified data, and in-product actions to revoke access, remove public or organization-wide sharing, mask data, or apply labels, with previews and audit trails before a change lands. That is the access-and-revoke job asked here, not only a map of stores.
Cyera Identity, described after the company’s acquisition of Oasis Security, is a related offering for non-human identities and AI agents. Confirm what is in the DSPM plan you would buy and what sits in that identity product. Pricing is quote-based.
Key features:
- Identity-to-data view for overexposed or policy-breaking access
- In-product revoke, unshare, mask, and label actions, with previews and audit trails
- Classification and discovery across cloud, SaaS, and related stores, as Cyera describes them
- A separate Cyera Identity offering for non-human identities and AI agents
Why we like it:
It shows which identities can reach classified data and documents a guarded, in-product way to revoke that access.
Limits:
The DSPM plan and the Identity offering are not automatically the same purchase. Public pages do not list a USD price, checked 12 Nov 2026.
License or pricing: Quote-based. Cyera’s public remediation and pricing pages do not list a USD price, checked 12 Nov 2026.
Proofpoint
Best for data access governance inside a human-security portfolio, including what AI agents can reach
Proofpoint DSPM is documented as discovering and classifying sensitive data, mapping the users, apps, and AI agents that can reach it, and remediating over-permissioned access, including removing risky shares and reducing permissions. The same product family sits in a broader human-security portfolio, so DLP, email, and insider-threat tools may already be in the account.
Proofpoint Insider Threat Management, which we cover on the insider risk page, and ZenGuide awareness training are different jobs from this access-governance question. Pricing is quote-based.
Key features:
- Data access governance that maps users, apps, and AI agents to sensitive data
- Remediation described as removing risky shares, reducing permissions, and closing exposure
- AI data exposure visibility for copilots, GenAI tools, and agents
- A broader Proofpoint portfolio that also includes DLP, email security, and insider threat management
Why we like it:
It puts data access governance, including what AI agents can reach, inside a human-security portfolio many enterprises already run.
Limits:
Some Microsoft 365 revoke workflows appear in Proofpoint DSPM documentation as beta capabilities; confirm what is generally available in the edition you would buy. Pricing is quote-based. Insider threat forensics and awareness training are separate products.
License or pricing: Quote-based. Proofpoint’s public DSPM pages do not list a USD price, checked 12 Nov 2026.
Cymphony
Best for a connected view of people, agents, and the data they can reach, with in-product revoke from that view
Cymphony’s site describes an agentless platform that maps people, AI agents, and machine identities to the data they can reach, then lets a team revoke access or notify an owner from that view. Investigation can run in plain language through an assistant the company calls Maestro, which the same pages say can draft notices and run remediations in parallel.
The company also describes four modules for AI tools, exposed data, identity hygiene, and in-progress insider activity. Independent validation is not documented. Pricing is quote-based, and a product trial is not documented on the public pages we reviewed.
Key features:
- A connected map of identities, including people and AI agents, to the data they can reach
- In-product actions to revoke access or notify an owner
- Plain-language investigation and remediation through Maestro, as Cymphony describes it
- Agentless ingestion, as the company states it, with no endpoint agent to install
Why we like it:
It starts from people and agents and documents a way to revoke the data access those identities should no longer have.
Limits:
Independent validation is not documented. Public pages do not list a USD price, and a free product trial is not documented on the site we reviewed, checked 12 Nov 2026.
License or pricing: Quote-based. Cymphony’s public pages do not list a USD price, checked 12 Nov 2026. The site offers a demo and a free AI readiness assessment; a product trial is not documented there.
How to choose a workforce security platform
- Start from the artifact you need to change. If the job is to rightsize standing permissions on classified data, Varonis, Cyera, Microsoft Purview, and Cymphony document that path. If the job is to see people and agents as they use or move data, Cyberhaven and Proofpoint are the closer starting points.
- Decide whether a suite you already own is enough. Purview is bought as a Microsoft add-on or as part of a broader Microsoft 365 bundle. Proofpoint DSPM may already sit next to email and DLP you run. An independent platform is the better comparison when the data lives outside that suite.
- Ask what happens to an AI agent, not only to a user. Every vendor on this page mentions agents or Copilot in some form. Have them show the inherited access an assistant gets from a shared drive, and the control that removes it.
- Price the public number first, then the quote. Purview Suite has a public USD 12 per user per month rate, paid yearly, on E3. The others are quote-based. Ask what is in the core platform versus a module, an identity add-on, or a managed service.
What we left out
- Exabeam: a SIEM and UEBA platform for detecting and investigating user behavior in a SOC. We left it out because first-party docs describe analytics and casework on security telemetry, not a data-access inventory with in-product revocation of file or dataset permissions. See Exabeam.
- BigID: already listed on our DSPM tools page and compared in BigID vs Varonis. We left it out here so this list stays on who can reach data and whether you can revoke that access, rather than reprinting that discovery shortlist.
- Harmonic Security: a 14 Oct 2026 raise around governing how employees use AI tools. We left it out because that job is already adjacent to our AI workspace and browser-security coverage, not the access-and-revoke question asked here.
What the internet thinks about workforce security platforms
Published customer comments, quoted for the argument, not the score. These appeared on vendor pages, so read them as vendor-selected.
Varonis customer comment · Jacob Lorz, VP Information Technology and CISO
“Leveraging Varonis to properly permission our files gives me the confidence to move forward with AI adoption.”
A named comment published on Varonis’s Data Security Platform page. It is a vendor-selected reference about permissions as a precondition for AI use, not a measured reduction figure.
Cymphony customer comment · Sean Mullins, CISO
“Who has access and what’s at risk used to be two separate questions. AI made them one, and Cymphony is the first platform we’ve seen that’s built that way.”
A named comment published on Cymphony’s homepage. Treat it as a vendor-selected reference; it speaks to combining access and risk questions, not to an independent test of revocation.
Choose Varonis when you need classification, permissions analysis, and automated remediation of overexposed access across many data stores, including what AI agents can reach. Choose Microsoft Purview when the data that matters already lives in Microsoft 365 and you want labels, DLP, and access restriction under a published Suite price. Choose Cyberhaven when the job is to follow sensitive data as people and agents move it, and to enforce policy on that path. Choose Cyera when you want an identity-to-data view and a guarded, in-product action that revokes access or removes a share. Choose Proofpoint when data access governance, including AI-agent exposure, should sit in a human-security portfolio you may already run. Choose Cymphony when you want to rightsize standing access for people and agents from a connected view of the data they can reach, with in-product revoke, and can pilot a launch-stage vendor first.
FAQs
What is a workforce security platform?
It is software that shows which people and AI agents can reach which sensitive data, and that can revoke or restrict that access when it is no longer justified. It is not the same as a data-at-rest inventory, a case file about a person, a network or browser control, an identity-governance review, or an awareness course.
How is this different from DSPM or insider risk tools?
DSPM tells you where sensitive data lives and how it is exposed in stores. Insider risk tools collect evidence and open cases when a person or agent behaves in a risky way. A workforce security platform is judged here on whether it can also show the access path and change it, by removing a permission, a share, or an inherited right, before or after a case exists.
Do these platforms replace IGA, SSE, or security awareness?
No. IGA still runs joiner-mover-leaver and access requests. SSE and enterprise browsers still control the path to the web and SaaS. Awareness still trains people. The platforms here can complement those programs when the missing piece is a current view of who can reach a file or dataset, and a way to take that access back.
Can one product cover both standing permissions and data in motion?
Some vendors document both a permissions cleanup and a movement or behavior control, but they do not start from the same place. A data-store inventory with revoke is a different operating rhythm from lineage or channel enforcement. Ask to see both workflows on the same overshared folder and the same AI assistant, rather than assuming one screen does both jobs.